InfoSecBulletin Cybersecurity for mankind
Japan’s Digital Agency found a data leak that may have exposed about 246,000 records with personal information of government workers. The agency explains that the attacker got in by taking advantage of a weak spot in a VPN device used by the Government Solution Service (GSS).
An investigation began on June 25 when the agency found a big file access from a maintenance and operations worker’s account. “On July 9th, it was discovered that a third party had used a vulnerability in a network-connected device (VPN) to gain access to the system and gain unauthorized access,” reads the announcement.
Daily Cyber security update for 14.11. 2026

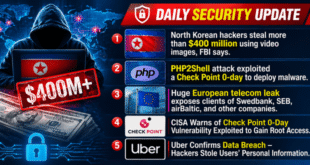
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

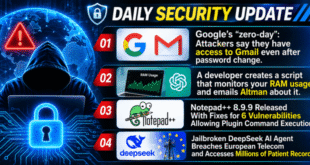
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

“On the same day, we suspended the account of the maintenance and operations personnel in question, cut off communication between the compromised equipment and the outside world, and prevented further unauthorized access.”
It is not clear which VPN product was affected or what weakness was used in the breach. The Japanese agency said in a separate Q&A that the problem had a medium severity rating and was not a zero-day.
The investigation revealed that the following data may have been exposed:
236,000 names
231,000 email addresses
94,000 telephone numbers
1,000 physical addresses
People whose information was exposed include government workers, public leaders, and businesses or individuals connected to the GSS system.
The event did not reveal personal data of the public. The information that might be at risk does not include My Number IDs, bank account info, or pension numbers.
The agency has not found any real misuse of the affected information, but it still warned about the high risk of impersonation and phishing. It told people not to open links or attachments in unexpected messages. The Digital Agency reminded everyone that it will never ask for passwords or credit card details by email or phone.
Affected people will be contacted directly, and the agency also created a special support line.
The agency told Japan’s Personal Information Protection Commission on July 15. They explained that the delay in informing the public was because it was complicated to figure out how the intrusion happened, what information might be affected, and who was impacted.
The agency says the effect was only on the affected system, and there was no confirmed unauthorized access, data leaks, or similar breaches on other systems. It also mentioned that the incident and response actions didn’t disrupt government services.