InfoSecBulletin Cybersecurity for mankind
Cybersecurity researcher Jeremiah Fowler discovered a large, unprotected database with sensitive insurance and vehicle information. It contained over 5.1 million files, totaling 10TB, including powers of attorney, vehicle registrations, repair invoices, and images of damaged vehicles showing license plates and VIN numbers.
According to Fowler, “The publicly exposed database was not password-protected or encrypted. It contained 5,170,256 files and images.”
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

A sampling of these files revealed a wide range of personally identifiable information (PII):
Names, physical addresses, phone numbers, and emails.
Registration documents with VINs, vehicle year, make, and model.
Nearly 16,000 powers of attorney documents granting legal authority to transfer or assign titles, some even including the IP addresses of individuals who signed them electronically.
Fowler discovered internal documents, including software licenses and sensitive business records that were improperly exposed.
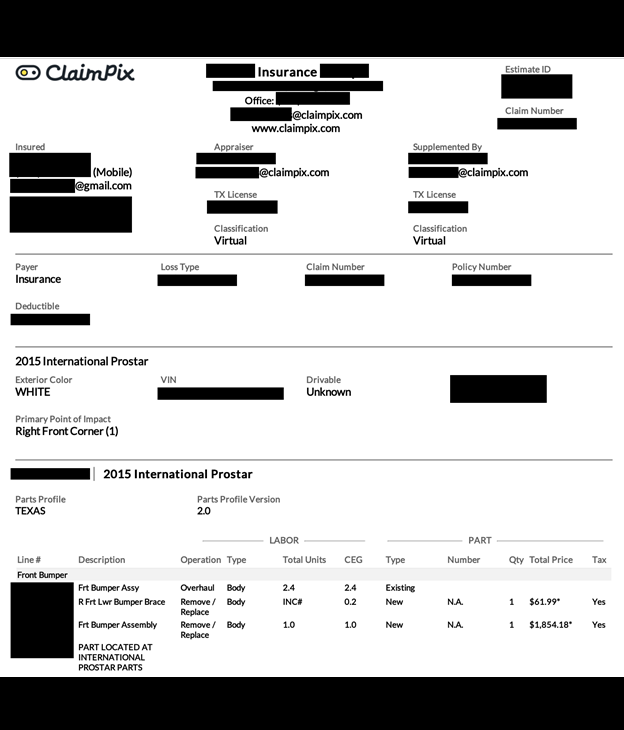
The exposed data appeared to belong to Illinois-based ClaimPix, a platform used across the U.S. for managing and filing auto insurance claims. Fowler explained, “Information inside the database (and the name of the database itself) indicated the records belonged to Illinois-based ClaimPix… I immediately sent a responsible disclosure notice to ClaimPix, and the database was restricted from public access shortly after.”
It is still unknown if the data was exposed for a long time or accessed by unauthorized users before being fixed.
The type of data exposed poses severe risks of fraud and identity theft. Fowler warned, “The exposure of personal data, insurance information, and even identification documents pose numerous potential risks both online and offline.”
For example:
VIN cloning: using stolen VINs to illegally register stolen or salvaged cars.
Insurance fraud: impersonating policyholders to file fraudulent claims or intercept payouts.
Impersonation attacks: exploiting powers of attorney to transfer vehicle ownership without the owner’s knowledge.
Fowler noted that criminals can merge data from different people to create fake identities for fraud.
Following Fowler’s disclosure, ClaimPix responded: “Thank you for alerting us to the security issues that you mentioned. We have investigated and confirmed your findings… We have updated policies and our code to address this issue and will be making those changes live later this evening.”
Fowler advises that, “companies in the insurance industry… encrypt all sensitive data… enforce access controls with multi-factor authentication… and perform regular audits of cloud storage systems to ensure they restrict public access.”