 InfoSecBulletin Cybersecurity for mankind
Tuesday (16 January) Atlassian released advisory for CVE-2023-22527 – RCE (Remote Code Execution) Vulnerability In Confluence Data Center and Confluence Server.
A template injection vulnerability on out-of-date versions of Confluence Data Center and Server allows an unauthenticated attacker to achieve RCE on an affected version. Customers using an affected version must take immediate action.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

Most recent supported versions of Confluence Data Center and Server are not affected by this vulnerability as it was ultimately mitigated during regular updates. However, Atlassian recommends that customers take care to install the latest version to protect their instances from non-critical vulnerabilities outlined in Atlassian’s January Security Bulletin.
Atlassian Cloud sites are not affected by this vulnerability. If your Confluence site is accessed via an atlassian.net domain, it is hosted by Atlassian and is not vulnerable to this issue.
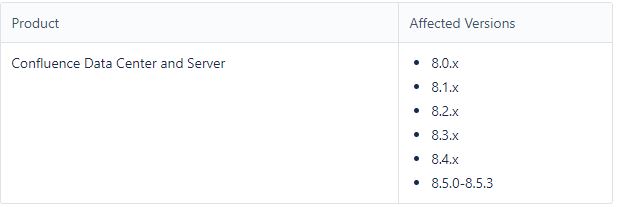
Affected Versions:
This RCE (Remote Code Execution) vulnerability affects out-of-date Confluence Data Center and Server 8 versions released before Dec. 5, 2023 as well as 8.4.5 which no longer receives backported fixes in accordance with our Security Bug Fix Policy. Atlassian recommends patching to the latest version.
What You Need To Do:
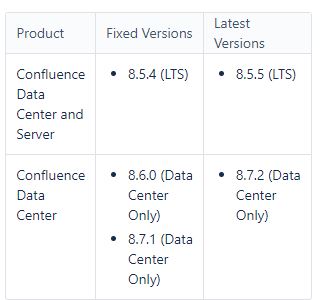
Immediately patch to the latest version
If you are on an out-of-date version, you must immediately patch. Atlassian recommends that you patch each of your affected installations to the latest version available. The listed Fixed Versions are no longer the most up-to-date and do not protect your instance from other non-critical vulnerabilities as outlined in Atlassian’s January Security Bulletin.
Mitigations:
There are no known workarounds. To remediate this vulnerability, update each affected product installation to the latest version.



