 InfoSecBulletin Cybersecurity for mankind
A study revealed that almost 5 million servers expose Git metadata, including 250,000 that leak deployment credentials through .git/config files.
A 2026 study from the Mysterium VPN research team found that about 5 million public web servers are leaking Git repository metadata, including over 250,000 that expose .git/config files with deployment credentials.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Misconfigurations allow attackers to access source code and steal sensitive information. This problem continues due to deployment errors, exposed hidden folders, and servers not automatically protecting these files, making minor mistakes lead to major security breaches.
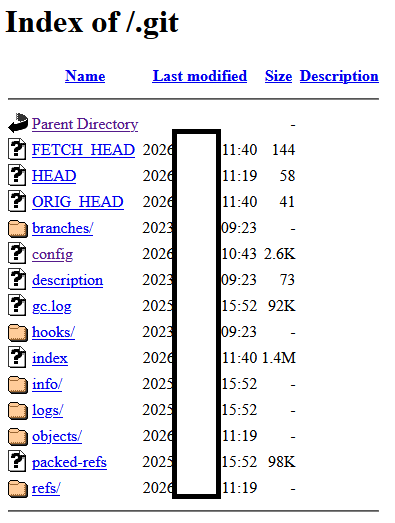
Some key takeaways:
Number of IP addresses found with publicly accessible .git structures: 4,964,815;
.git/config files with deployment credentials inside the config: 252,733 (~5.09%);
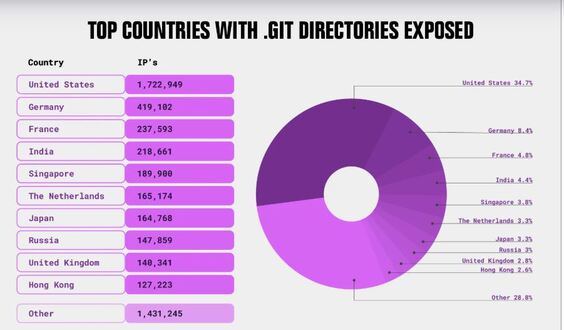
Countries with the most websites found vulnerable include the United States with 1,722,949 IPs (~34.70%), Germany (419,102 IPs), France (237,593 IPs), India (218,661 IPs), Singapore (189,900 IPs), The Netherlands (165,174 IPs), Japan (164,768 IPs), Russia (147,859 IPs), United Kingdom (140,341 IPs), and Hong Kong with 127,223 IPs.
This is more than a technical mistake; it’s a major vulnerability affecting websites and organizations worldwide.
The study reveals that exposed Git servers are mainly found in the US, Europe, and APAC regions. Exposed .git folders can lead to source code theft, credential abuse, supply chain attacks, and unauthorized access to cloud services, turning a misconfiguration into a serious breach.
To fix exposed .git folders, restrict public access, ensure Git data isn’t in production, and update any leaked credentials. Even 5% of exposed credentials can lead to hundreds of thousands of usable secrets. Teams should implement server rules, use secrets management, conduct pre-commit checks, monitor activity, and have rapid response plans.
“The findings highlight a widespread issue caused by deployment practices, inconsistent server configuration, and misplaced assumptions about safety. While the presence of exposed Git metadata alone is dangerous, the inclusion of credentials dramatically increases risk, enabling repository takeover, supply chain attacks, and access to cloud infrastructure.” said the report.
“The research underscores that even small percentages of credential exposure become severe at the internet scale and that attackers can automate discovery with ease.”



