 InfoSecBulletin Cybersecurity for mankind
Norway accused the hacker group Salt Typhoon of breaching various organizations. The Norwegian Police Security Service reports that the hacker group is targeting weak network devices for espionage.
The disclosure was made in the Norwegian Police Security Service’s (PST) annual threat assessment for 2026. The agency’s director general, Beate Gangås, said Norway was “facing its most serious security situation since World War II,” citing pressure from multiple foreign intelligence services.
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Norway has confirmed breaches related to Salt Typhoon. This threat, recognized by U.S. national security officials as significant in cybersecurity, has infiltrated critical networks globally, including telecoms in Canada and the U.S., where it reportedly intercepted communications of top officials.
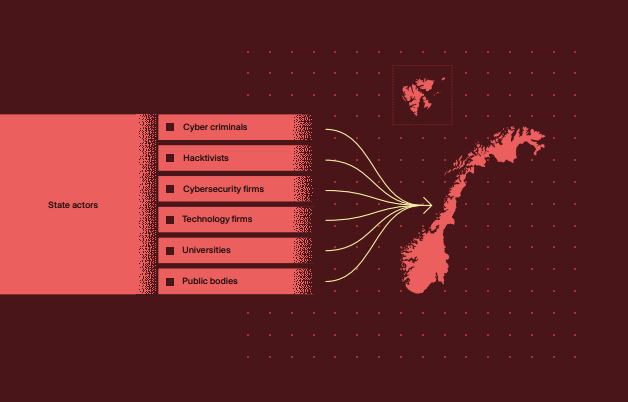
Gangås said foreign states — particularly China, Russia and Iran — are “conducting intelligence operations and employing hybrid tactics in Norway to undermine our resilience,” stressing the “vital” need for stronger protective security, intelligence and situational awareness.
Telecom providers had to improve their security and reassess their cyber defense policies due to these breaches. The report did not disclose many details about this cyber campaign aimed at Norway.
This case highlights the importance of improving cyber defense, enhancing global cooperation, and addressing threats from transnational cyber actors.



