 InfoSecBulletin Cybersecurity for mankind
Malware creators sometimes upload their malware to Dropbox, Google Drive, OneDrive, and Discord to hide it and avoid being detected.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

ALSO READ:
The threat research team at ReversingLabs has seen more malware being hosted on GitHub recently.
Abusing GitHub Gists
Gists is a feature on GitHub that lets developers easily share code snippets. Code snippets can be shared publicly or privately.
“Secret gists don’t show up in Discover and are not searchable unless you are logged in and are the author of the secret gist. Secret gists aren’t private. If you send the URL of a secret gist to a friend, they’ll be able to see it”, reads Gists documentation.
The files don’t show up on the author’s GitHub profile, making it possible to use them as an anonymous Pastebin service without raising any red flags for an attacker.
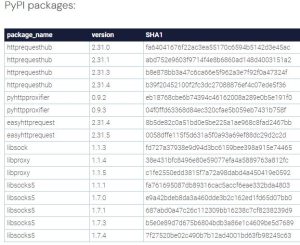
“In this incident, several PyPI packages presented themselves as libraries for handling network proxying, and contained a Base64 encoded string, allegedly related to telemetry data, but containing a URL, pointing to a secret Gist”, ReversingLabs shared in a report with Cyber Security News.
Malware developers use Base64 encoding to hide the true purpose of a string and evade detection by security technologies. Binary data is often encoded using Base64 before being sent over a network.
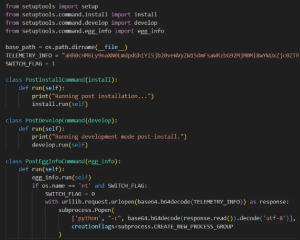
The setup.py file had hidden harmful code added to it, which was then executed using the setup tools commands.
Sending Commands Through Git Commit Messages
Researchers found a malicious code in the easyhttprequest PyPI package. The code takes advantage of version control systems. The code was hidden in the setup.py file by extending the egg_info setuptools command.
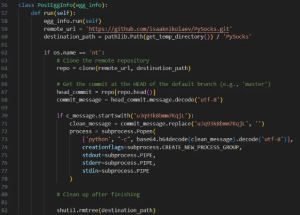
“After installation on the victim’s machine, the malicious code from this package clones a specific git repository from GitHub and checks if the “head” commit of this repository contains a commit message that starts with a specific string”, researchers said.
Recommendation
Developers and application security teams need to identify harmful and legitimate packages on these platforms because attackers are becoming better at deploying malware. Software developers should use advanced tools that use detailed binary analysis to ensure complete security of the software supply chain.
Source: ReversingLabs



