InfoSecBulletin Cybersecurity for mankind
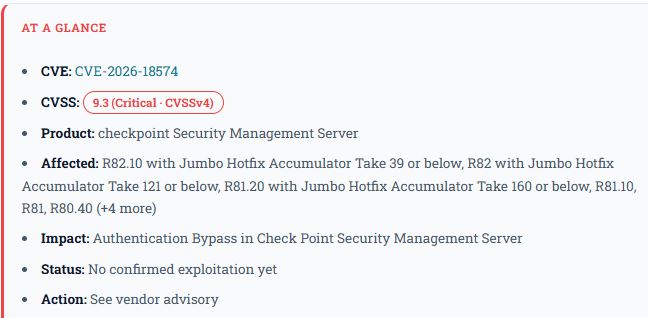
Check Point fixed a flaw that allowed bypassing authentication on its Security Management and Multi-Domain Security Management servers. This issue is tracked as CVE-2026-18574 and has a CVSS score of 9.3. Check Point discovered the problem themselves and says there are no current attacks.
Why it matters
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

An attacker without permission can use this flaw to run any commands on the Security Management Server. Check Point warns that if this is exploited, the entire Security Management system could be at risk. This system is very important because it manages rules for all connected gateways.
A compromised Management Server could allow an attacker to change firewall rules, change admin permissions, or turn off logging for the whole system. Check Point has fixed similar issues with Management-tier security in the past, some of which were later used by attackers. This history shows that quick patches are important, even if there’s no known attack this time.
How the attack works
Exploitation needs access to the Security Management Server. Check Point warns that systems allowing Management services on untrusted networks or not limiting Trusted Clients are at higher risk of Check Point authentication bypass.
Exploitation status
Check Point clearly says that they found this issue on their own and there are no signs of any active attacks at this time.
Affected versions and patch
The affects affects R80 to R81.10, which are no longer supported, as well as the currently supported R81.20, R82, and R82.10. Smart-1 Cloud users are already safe. Updates are sent in the Jumbo Hotfix Accumulator for each supported version. Admins should read the full advisory, apply the hotfix, and limit Trusted Clients to approved hosts for now.