 InfoSecBulletin Cybersecurity for mankind
A lot number of microsoft Exchange email servers in Europe, the United States, and Asia are at risk because they are accessible on the public internet. These servers are using an old and unsupported version of the software, which makes them vulnerable to multiple security issues, including some that are very serious.
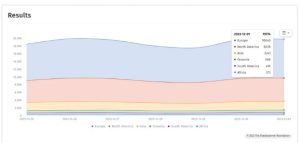
The ShadowServer Foundation found 20,000 Microsoft Exchange servers that have reached the end-of-life stage are still accessible online. Most of these servers are in Europe, but there are also many in North America and Asia.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

ShadowServer’s statistics may not show the complete situation. Macnica security researcher Yutaka Sejiyama discovered that there are 30,000 Microsoft Exchange servers that are no longer supported. Sejiyama’s scans on Shodan revealed that these unsupported servers include versions such as Exchange Server 2007, Exchange Server 2010, and most instances of Exchange Server 2013.
Outdated Exchange servers found by ShadowServer and Sejiyama have many vulnerabilities that allow remote code execution. An important security problem is ProxyLogon (CVE-2021-26855) which, when combined with another bug (CVE-2021-27065), allows remote code execution. Sejiyama’s analysis shows that around 1,800 vulnerable Exchange systems are exposed to ProxyLogon, ProxyShell, or ProxyToken vulnerabilities.
Organizations have taken steps to deal with these vulnerabilities, but it’s important to know that these measures are not enough. Microsoft advises companies to prioritize updating servers connected to external networks. If servers are no longer supported, upgrading to a version that still receives security updates is the only viable option.
Organizations must act immediately to address the ongoing exploitation of these vulnerabilities and the large number of exposed servers. They should secure their Exchange servers and ensure they are using supported and updated software versions. This will help protect sensitive data and minimize risks.



