 InfoSecBulletin Cybersecurity for mankind
More than 84,000 Roundcube webmail installations are at risk due to CVE-2025-49113, a severe remote code execution (RCE) vulnerability that comes with an available public exploit. The flaw in Roundcube (versions 1.1.0 to 1.6.10) was discovered by Kirill Firsov and was patched on June 1, 2025.
The bug stems from unsanitized $_GET[‘_from’] input, enabling PHP object deserialization and session corruption when session keys begin with an exclamation mark.
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Soon after the patch was out, hackers created a working exploit by reverse-engineering it and sold it on underground forums.
Though CVE-2025-49113 needs authentication to exploit, attackers assert they can acquire valid credentials using CSRF, log scraping, or brute-force methods.
Firsov shared technical details about the flaw on his blog to help defend against active exploitation attempts that are very likely to occur.
Massive exposure:
Roundcube is commonly used by web hosting providers and in sectors like government, education, and tech, with over 1,200,000 instances visible online.
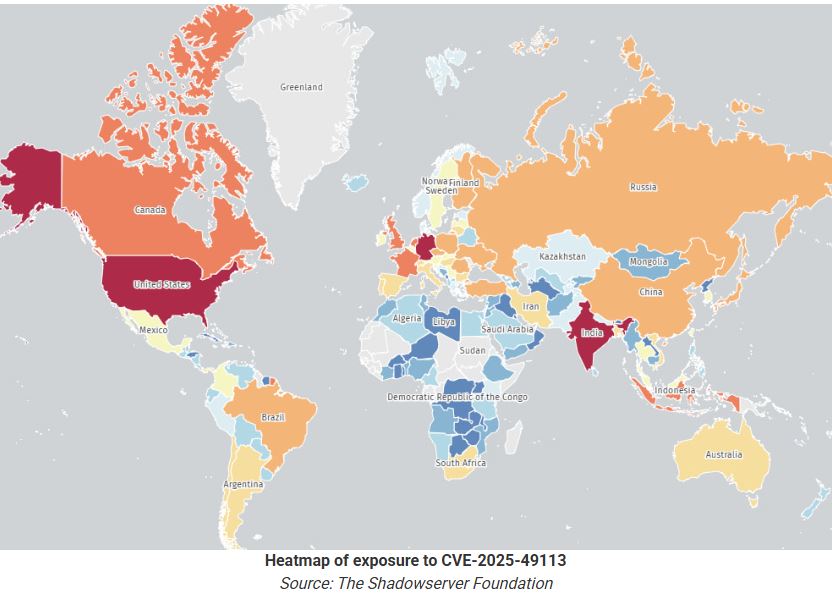
As of June 8, 2025, The Shadowserver Foundation reports 84,925 vulnerable Roundcube instances related to CVE-2025-49113.
The majority of instances are located in the United States (19,500), India (15,500), Germany (13,600), France (3,600), Canada (3,500), and the United Kingdom (2,400). The risk of exploitation and data theft makes this a serious cybersecurity issue. Admins should upgrade to versions 1.6.11 and 1.5.10 to fix CVE-2025-49113 promptly.
Bleepingcomputer reported, It is unclear if the flaw is being leveraged in actual attacks and at what scale, but immediate action is advised nonetheless.
If upgrading is impossible, it is recommended to restrict access to webmail, turn off file uploads, add CSRF protection, block risky PHP functions, and monitor for exploit indicators.



