InfoSecBulletin Cybersecurity for mankind
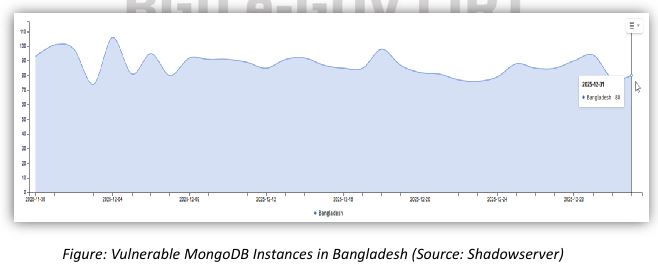
BGD e-GOV CIRT found 80 insecure MongoDB databases in Bangladesh exposed online, affected by the CVE-2025-14847 vulnerability (MongoBleed). This critical flaw allows remote attackers to access sensitive server data when zlib compression is enabled.
MongoDB is often used to store personal, financial, and operational information. This exposure poses significant risks to data protection and public confidence in digital services in Bangladesh.
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Vulnerability Overview: CVE-2025-14847
The critical security flaw, CVE-2025-14847, has been discovered in both MongoDB Community and Enterprise versions. It stems from poor access control and insecure settings, posing a risk of unauthorized remote access from untrusted networks.
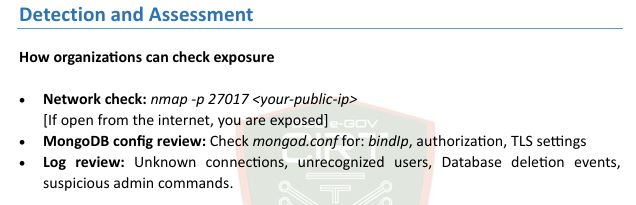
The vulnerability affects network-exposed MongoDB services on TCP port 27017. Often, no authentication is needed or the authentication is weak, raising the risk of being compromised.
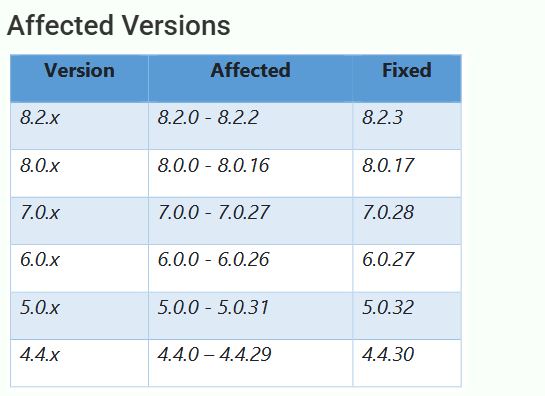
CIRT advises that to manage the risk of CVE-2025-14847, organizations using MongoDB should strengthen security immediately. MongoDB should not be publicly accessible and should only bind to localhost or trusted internal IPs. Strong authentication and access controls should be applied by enabling authorization, removing unused accounts, and following the least privilege principle. Organizations should upgrade to the latest patched MongoDB version and ensure all vendor fixes are implemented. In addition, network protections must restrict database access to trusted servers and block public connectivity through firewalls and ACLs.