 InfoSecBulletin Cybersecurity for mankind
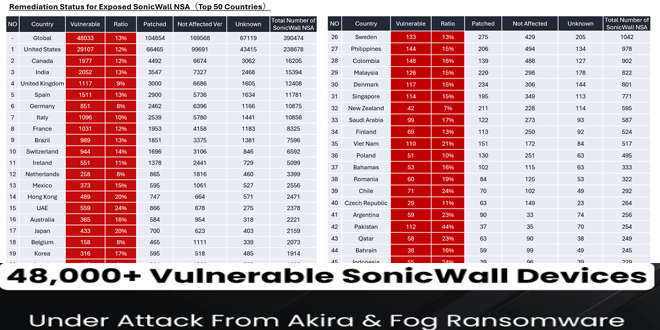
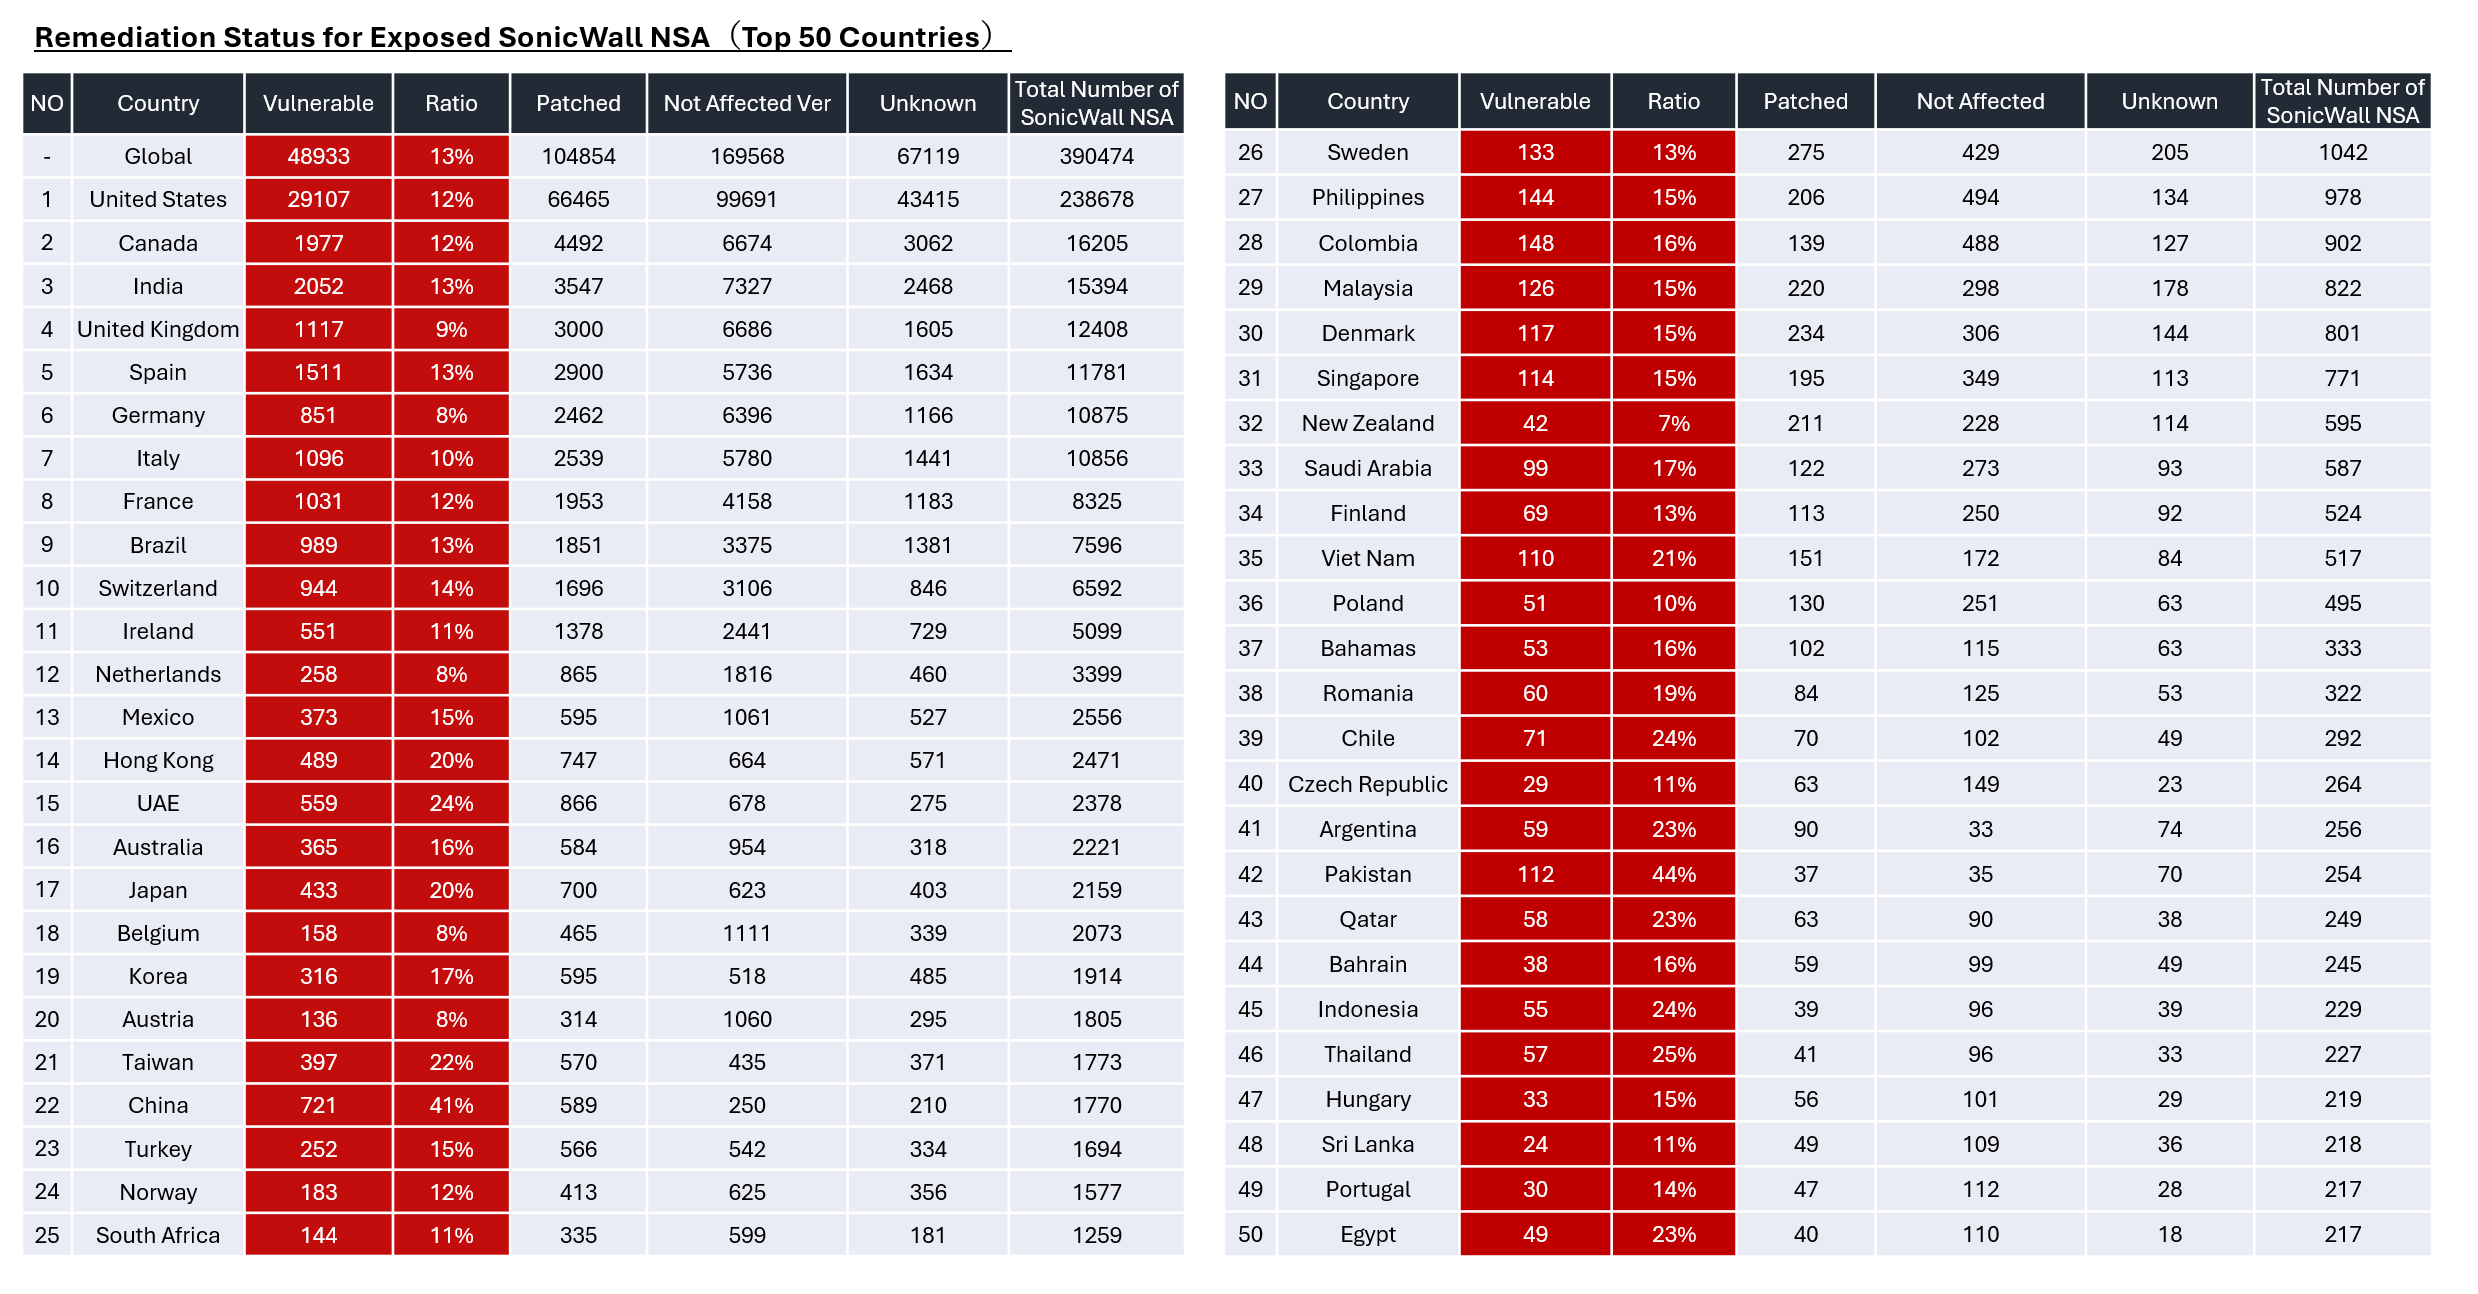
Over 48,000 SonicWall devices are still vulnerable to a serious security flaw, putting organizations worldwide at risk of ransomware attacks. The CVE-2024-40766 vulnerability was disclosed in September 2024 and is actively exploited by ransomware groups Akira and Fog.
CVE-2024-40766 is a serious access control vulnerability in SonicWall’s SonicOS, used in its firewalls and VPNs.
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

A CVSS score of 9.3 indicates a vulnerability that enables attackers to gain unauthorized administrative access to affected devices. This puts systems at risk of data breaches, operational disruptions, and ransomware attacks.
Many organizations still haven’t secured their devices, despite patches being available since August 2024, leaving them vulnerable to exploitation.
Investigations show that these groups have targeted organizations with vulnerable, unpatched SonicWall devices for initial access.
From September to December 2024, over 100 companies were confirmed victims of ransomware groups using this exploit.
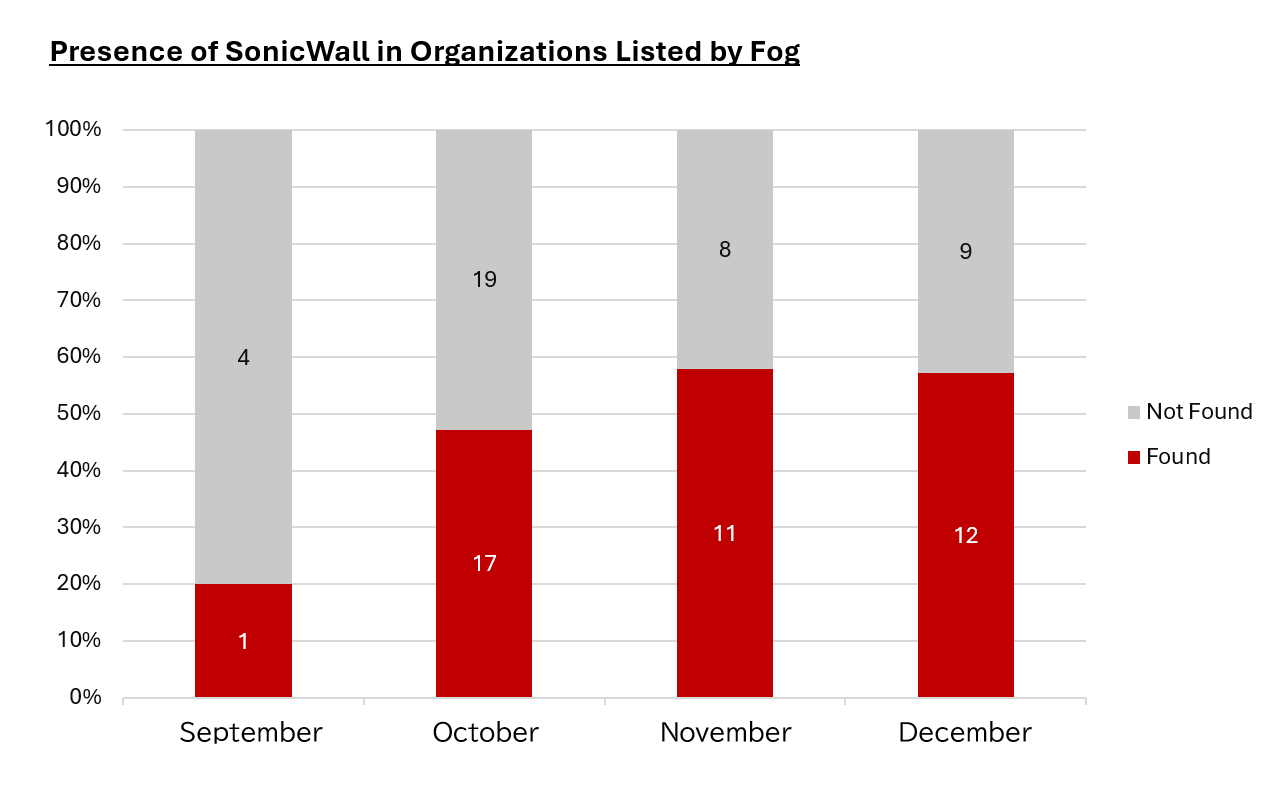
According to a Macnica report, about 46% of organizations listed on leak sites as victims of Akira and Fog were affected, compared to less than 5% of victims of other ransomware groups who used SonicWall.
Akira ransomware was used in 75% of the attacks, while Fog was responsible for the other 25%. The time from initial access to encryption has been alarmingly short, varying from just 1.5 to 10 hours.
As of late December 2024, over 48,933 SonicWall devices are still unpatched and vulnerable, highlighting serious cybersecurity gaps despite ongoing warnings from SonicWall and experts.
With over 48,000 devices at risk, organizations need to address this vulnerability to avoid falling victim to ransomware attacks.



