Monday , November 16 2026
3.3 Million

3.3 Million Email Server Expose User Passwords and Messages in Plain Text

Around 3.3 million servers are running POP3/IMAP email services without encryption (TLS) enabled, the Shadowserver Foundation, a nonprofit security organization, has discovered. Most of these servers reside in the US, Germany, and Poland.

POP3 (Post Office Protocol version 3) is an aging protocol used by email clients to retrieve emails from a mail server. It is often used alongside the newer protocol IMAP (Internet Message Access Protocol).

Six 0-Days Discovered by Researchers Allow Unauthorized Access to Supermarket Fridge Systems

Six remote code flaws were found in the Danfoss AK-SM800A supermarket fridge controller. These flaws let someone take control from...
Read More
Six 0-Days Discovered by Researchers Allow Unauthorized Access to Supermarket Fridge Systems

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

The Shadowserver Foundation tracks 3.3 million POP3/IMAP servers along the globe that do not have TLS encryption.
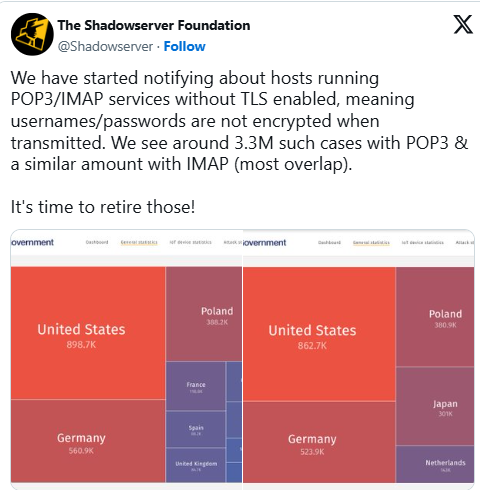
“It’s time to retire those services!” the organization warns.

“We have started notifying about hosts running POP3/IMAP services without TLS enabled, meaning usernames/passwords are not encrypted when transmitted. We see around 3.3M such cases with POP3 & a similar amount with IMAP (most overlap).”

Almost 900,000 of these servers are from the US, while Germany follows in second place with 523,000 servers. Poland and Japan are next on the list, with 381,800 and 301,800 unprotected servers, respectively.

Users of such email services should be aware that anyone with basic network monitoring tools can intercept their communications and steal their credentials.

“Note that regardless of whether TLS is enabled or not, service exposure may enable password-guessing attacks against the server,” the Shadowserver Foundation said.


Check Also

API Connect

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out …