 InfoSecBulletin Cybersecurity for mankind
Security researchers have discovered a database with 184 million account credentials, highlighting the need to update compromised passwords, strengthen weak ones, and enable multi-factor authentication. Although the database is not new, it shows the ongoing circulation of leaked data from major platforms like Apple, Google, Microsoft, Amazon, Facebook, Instagram, and X (formerly Twitter).
Cybersecurity expert Jeremiah Fowler recently released a report urging users not to panic about a new extensive database on the internet. Instead, he calls for action: users should update weak or compromised passwords, particularly if the same ones are used on multiple platforms.
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

The exposed database has 184 million entries with usernames, email addresses, passwords, and login URLs. It was left unprotected—without a password or encryption—granting anyone easy access.
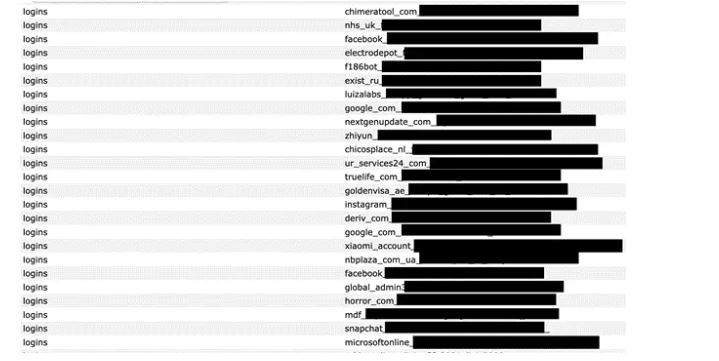
There’s no need to panic; the dataset likely consists of aggregated records from earlier breaches rather than a new leak. However, the situation is still serious. Currently, there’s no evidence indicating that this database is notably different from others previously found on the dark web.
The dataset has not been shared with Have I Been Pwned, a popular service for checking compromised credentials. Sharing it could alert millions of users through their browsers or password managers, promoting better password hygiene.
Wired conducted an independent review of 10,000 samples from the dataset, confirming it includes various services such as Google, Facebook, Instagram, Discord, Microsoft, Netflix, PayPal, Amazon, Apple, X/Twitter, and Spotify.
The database lacks two-factor or multi-factor authentication (2FA/MFA) details. Therefore, users with these security measures are protected, even if their passwords are compromised. This highlights the importance of enabling 2FA.
Users should review breach notifications in their browsers or password managers. Replace any reused passwords, even strong ones. If you receive a notification about a compromised password, change it right away. Most importantly, enable multi-factor authentication on all platforms that offer it for better security.



