 InfoSecBulletin Cybersecurity for mankind
The FBI has issued a warning stating that even after being patched against a critical flaw, Barracuda Networks Email Security Gateway (ESG) appliances are still vulnerable to potential compromise by suspected Chinese hacking groups.
It said that the fixes were not effective and that it still sees intrusions and considers all affected Barracuda ESG devices to be compromised and vulnerable to this attack.
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

ALSO READ:
WinRAR zero-day exploited since April to hack trading accounts
CVE-2023-2868 is a zero-day bug that was tracked with a CVSS score of 9.8. It was discovered to have been weaponized in October 2022, more than seven months before it was fixed. Mandiant, owned by Google, is diligently monitoring the China-nexus activity cluster known as UNC4841.
With the presence of a remote command injection vulnerability in versions 5.1.3.001 through 9.2.0.006, unauthorized individuals can gain administrator privileges and execute system commands on the ESG product.
The observed attacks have shown that a successful breach serves as a gateway to unleash numerous malware strains, including SALTWATER, SEASIDE, SEASPY, SANDBAR, SEASPRAY, SKIPJACK, WHIRLPOOL, and SUBMARINE (also known as DEPTHCHARGE). These strains enable the execution of any commands and effectively evade defense mechanisms.
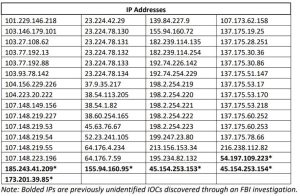
The FBI stated that cyber actors used a vulnerability to add harmful payloads to the ESG appliance. These payloads had various capabilities like persistent access, email scanning, credential harvesting, and data exfiltration.
The threat intelligence company has identified UNC4841 as an aggressive and highly skilled group, showcasing a remarkable ability to adapt their custom tools and employ advanced tactics to maintain control over high-value targets with remarkable persistence.
The federal agency strongly advises customers to immediately isolate and replace all affected ESG devices. It is also crucial to conduct thorough network scans to identify any suspicious outgoing traffic.



