 InfoSecBulletin Cybersecurity for mankind
UnitedHealth confirmed that the ransomware attack on its Change Healthcare unit last February impacted about 190 million Americans, nearly double earlier estimates. The U.S. health insurance company confirmed the latest figures to TechCrunch on Friday after the markets closed.
“Change Healthcare has determined the estimated total number of individuals impacted by the Change Healthcare cyberattack is approximately 190 million,” said Tyler Mason, a spokesperson for UnitedHealth Group in an email to TechCrunch. “The vast majority of those people have already been provided individual or substitute notice. The final number will be confirmed and filed with the Office for Civil Rights at a later date.”
NetamLoader malware to attack Win10: Customized for Gov.t in Asia

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

UnitedHealth’s spokesperson said the company was “not aware of any misuse of individuals’ information as a result of this incident and has not seen electronic medical record databases appear in the data during the analysis.”The February 2024 cyberattack is the largest medical data breach in U.S. history, leading to months of healthcare system outages. Change Healthcare, a major health tech company and UnitedHealth subsidiary, processes a significant amount of health data and healthcare claims in the U.S.
The data breach resulted in the theft of massive quantities of health and insurance-related information, some of which was published online by the hackers who claimed responsibility for the breach.
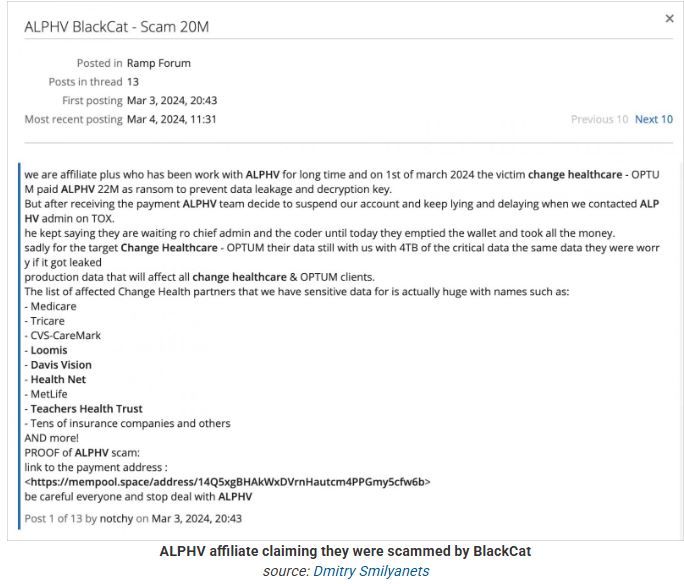
Change Healthcare paid at least two ransoms to stop the stolen files from being published. UnitedHealth initially reported that about 100 million individuals were affected when it submitted a preliminary analysis to the Office for Civil Rights, which investigates data breaches.
Change Healthcare’s data breach notice revealed that cybercriminals stole personal information, including names, addresses, dates of birth, phone numbers, email addresses, and government IDs like Social Security numbers, driver’s license numbers, and passport numbers.
The stolen health data includes diagnoses, medications, test results, treatment plans, and health insurance details. It also contains financial and banking information from patient claims.
It was later learned that the BlackCat ransomware gang, aka ALPHV, was behind the attack. UnitedHealth Group’s CEO Andrew Witty testified that the hackers accessed Change’s systems using a stolen account credential that lacked multi-factor authentication.



