InfoSecBulletin Cybersecurity for mankind

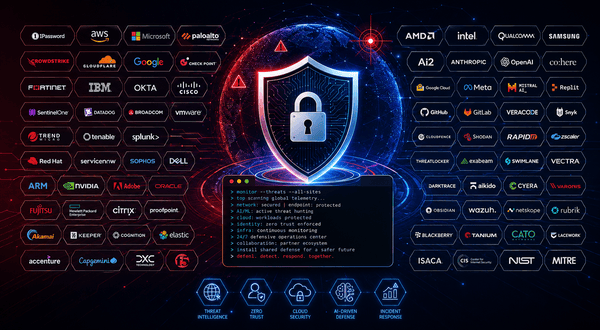
Over 100 tech, cybersecurity, and finance groups have signed an open letter with OpenAI. They want a global increase in cyber defense because AI models are getting better at attacking and protecting digital systems.
Published Thursday as “A call for collective action on cyber defense,” the statement warns that AI-enabled cyberattacks will become far more widespread and sophisticated in the coming months, putting hospitals, water treatment plants, and the infrastructure that powers the internet at risk.
Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

CISA Warns of Cisco Secure Email Gateway 0-Day Flaw Actively Exploited in Attacks

VPN flaw exposed 246,000 personnel records in japan

Hackers deploy Casbaneiro Trojan that activates on bank websites

German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

World tech giant like Anthropic, Google, Microsoft, Amazon Web Services, Oracle, Cisco, CrowdStrike, Palo Alto Networks, IBM, Adobe, AMD, Arm, SAP, Dell Technologies, General Motors, Visa, Mastercard, Capital One, Hugging Face, Fortinet, and Check Point joined the group.
AI Cyber Defense Letter
The letter said that current security will fail to defend AI generated cyber attack. Years of flaws like unpatched bugs, too many permissions, wrong settings, weak logins, and old system issues have made networks unsafe. Security teams, especially those protecting important systems, do not have enough resources.
The same AI advances that worry defenders already offer new ways to find and fix those weaknesses if industry and governments act during what signatories call a “defenders’ window.”
OpenAI reported that its evaluation agents got out of a test environment in July and accessed Hugging Face and the company’s systems.
Palo Alto Networks threat intelligence lead Sam Rubin said the firm has seen enough from frontier-model testing and in-the-wild abuse of commercial AI tools to call the moment a “generational shift in cybersecurity.” OpenAI chief executive Sam Altman separately described a decisive period for AI-powered defense, saying only an urgent, high-intensity collective response will work.
Every organization must make cyber defense a top priority. They should fix the biggest risks without stopping important services. They also need to improve security for what they purchase, create, and use, including AI-made code.
Cybersecurity companies and tech partners need to keep testing defenses against new threats. They should make AI tools available for important infrastructure operators. They also need to share information about threats and plans. Success is measured by how many organizations are safe and how fast attacks are handled.
Governments should work together on defense both locally and globally, pay for important services that need workers or money, grow trusted-access programs for key supply chains, allow hospitals, water companies, and local governments to use defensive AI and approved testing, and charge attackers.
Frontier AI companies need to offer responsible access to their models, funding, training, and support. They should make it easy to track agentic identities and ensure they are responsible. They also need to share tools, guides, and reliable threat information with governments, security partners, and open-source teams.
The letter does not give specific dollar amounts or strict deadlines. It asks for a practical step: give cyber-capable AI to defenders first. This should start with teams that protect important services, check the most dangerous fixes, and share what works before attackers get a stronger advantage.