InfoSecBulletin Cybersecurity for mankind
Ireland’s Data Protection Commission fined TikTok €530 million ($601 million) on Friday for violating data protection laws by transferring European users’ data to China.
“TikTok infringed the GDPR regarding its transfers of EEA [European Economic Area] User Data to China and its transparency requirements,” the DPC said in a statement. “The decision includes administrative fines totaling €530 million and an order requiring TikTok to bring its processing into compliance within 6 months.”
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

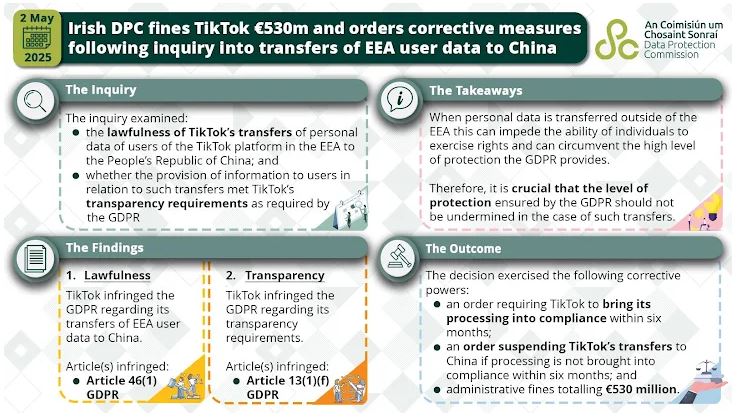
The order, in addition, requires the company to suspend data transfers to China within the time period.
The penalty stems from a September 2021 investigation into the company’s transfer of personal data to China and its adherence to strict data protection laws concerning data transfers to other countries.
DPC Deputy Commissioner Graham Doyle commented that TikTok’s transfer of personal data to China violated Article 46(1) of the GDPR because it did not ensure that EEA users’ data received the same privacy protections as in the EU.
Doyle further added that TikTok did not address concerns arising from potential access by Chinese authorities under anti-terrorism and counter-espionage laws in the country and which “materially” diverged from European Union standards.
The DPC criticized TikTok for giving incorrect information during an investigation, claiming it didn’t store EEA users’ data on Chinese servers. However, last month, TikTok revealed that it found an issue in February 2025, confirming that some EEA data had been stored on servers in China.
“Whilst TikTok has informed the DPC that the data has now been deleted, we are considering what further regulatory action may be warranted, in consultation with our peer EU Data Protection Authorities,” Doyle said.
Christine Grahn, TikTok’s head of public policy and government relations for Europe, said the decision failed to take into account Project Clover, a data security initiative aimed at protecting European user data, and that the ruling does not reflect the current safeguards put in place.
“The DPC itself recorded in its report what TikTok has consistently said: it has never received a request for European user data from the Chinese authorities, and has never provided European user data to them,” Grahn said.
This is the second fine levied by the DPC against the ByteDance-owned company. In September 2023, TikTok was handed a €345 million (then about $368 million) fine for violating GDPR laws in relation to its handling of children’s data.