 InfoSecBulletin Cybersecurity for mankind
A free tool is now available to scan public GitHub repositories for exposed AWS credentials. Security engineer Anmol Singh Yadav created AWS-Key-Hunter after discovering over 100 exposed AWS access keys, many with high privileges, in public repositories. He described these findings as “just waiting to be exploited” in his blog about the tool.
Leaked security keys can allow criminals to take over cloud accounts and access AWS resources. This can result in theft of computing power, illegal cryptocurrency mining, data breaches, ransom demands, and unauthorized changes to system settings.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Real-Time Alerting via Discord Webhooks:
The tool uses Discord’s webhook API to send instant notifications to a set channel. When it detects valid credentials, AWS-Key-Hunter sends a POST request with repository metadata and partial key details.
Security teams can tailor alert thresholds and set up automated key rotation using AWS Lambda integrations.
To deploy AWS-Key-Hunter:
Generate GitHub personal access token with repo scope
Configure Discord webhook URL in .env
Launch via Docker
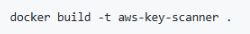
Build the Docker image:
Run the container:




