 InfoSecBulletin Cybersecurity for mankind
SonicWall’s Product Security Incident Response Team (PSIRT) has released a critical update for its SMA1000 series appliances due to a Server-Side Request Forgery (SSRF) vulnerability, identified as CVE-2025-2170, with a CVSS base score of 7.2.
The flaw in the SMA1000 appliances’ WorkPlace interface allows unauthenticated remote attackers to send unauthorized outbound requests to any destination under specific conditions.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

“A Server-side request forgery (SSRF) vulnerability has been identified in the SMA1000 Appliance Work Place interface, which in specific conditions could potentially enable a remote unauthenticated attacker to cause the appliance to make requests to an unintended location,” the advisory reads.
This vulnerability can be used to bypass access controls, scan internal networks, or extract data from restricted internal services.
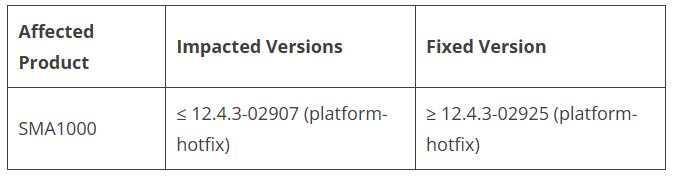 Only the SonicWall SMA1000 series appliances are affected; SonicWall Firewalls and SMA 100 series are not impacted.
“SonicWall PSIRT strongly advises users of the SMA1000 product to upgrade to the latest hotfix release version to address the vulnerability,” the advisory warns.
The recommended patch can be found on MySonicWall, SonicWall’s customer portal.



