InfoSecBulletin Cybersecurity for mankind
SoftBank has disclosed that personal information of more than 137,000 mobile subscribers—covering names, addresses, and phone numbers—might have been leaked by a contracted outsourcing firm. In response, the company intends to end its contract with the provider and will collaborate with the police to assess future actions.
SoftBank announced that 137,156 personal information records, including names, addresses, and phone numbers of SoftBank and Y! Mobile users, may have been leaked from an outsourced company called “UF Japan.”
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Credit card and account numbers remained safe. The incident was uncovered after the company investigated a third-party report in March.
The management of entry and exit protocols on the floors housing personal data was poorly handled by the outsourced company, resulting in a potential violation last December when a previous employee from a partner organization may have illegally entered the site and taken personal information.
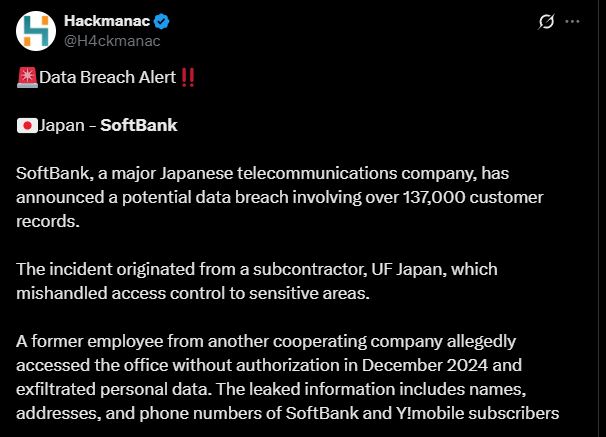
In addition, the personal information was made accessible to people unrelated to the company’s work.
NHK reported, The company has terminated its contract with the outsourced company and is consulting with the police to consider future responses.
SoftBank commented, “We take the serious incident seriously, and will strengthen management of outsourced companies that handle personal information to prevent recurrence.”
Trend Micro Apex One Flaw Allow Attackers to Inject Malicious Code