Friday , October 23 2026
ESHYFT

Researcher found non protected database form ESHYFT containig 86000 records

Cybersecurity researcher Jeremiah Fowler found and reported a non-password-protected database with over 86,000 records belonging to ESHYFT, a New Jersey-based HealthTech company.

ESHYFT operates in 29 states and provides a mobile app platform connecting healthcare facilities with workers like Certified Nursing Assistants (CNAs), Licensed Practical Nurses (LPNs), and Registered Nurses (RNs). Jeremiah Fowler said, the name of the database as well as the documents inside it indicated that the records belonged to ESHYFT.

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

NSA, CISA, and NIST have released security guidelines to find, control, and stop AI agents that go beyond their allowed...
Read More
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Anthropic says a Claude research model showed how the National Security Agency made seeds for five NIST elliptic curves in...
Read More
Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

The Indian Computer Emergency Response Team (CERT-In), which is the government's cybersecurity arm, has issued a "critical" rated advisory after...
Read More
Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In
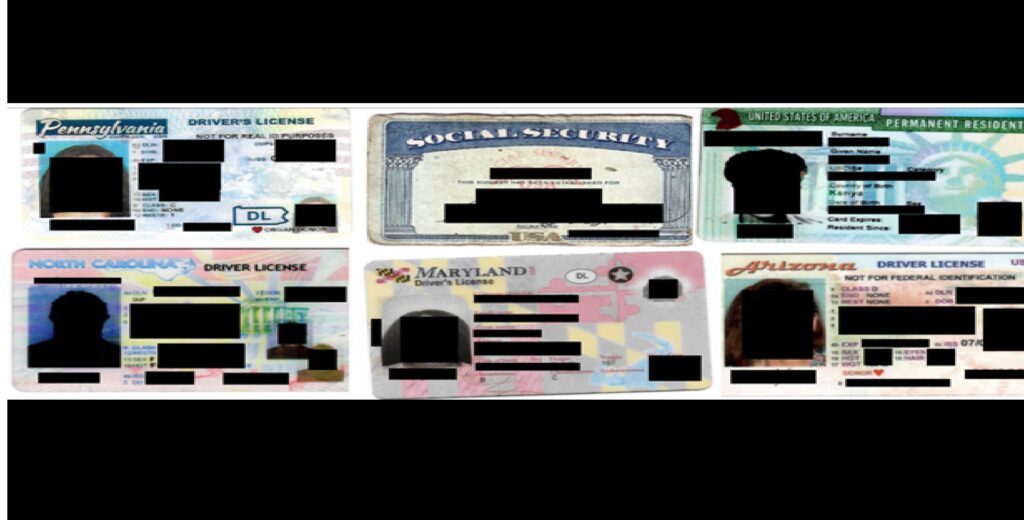
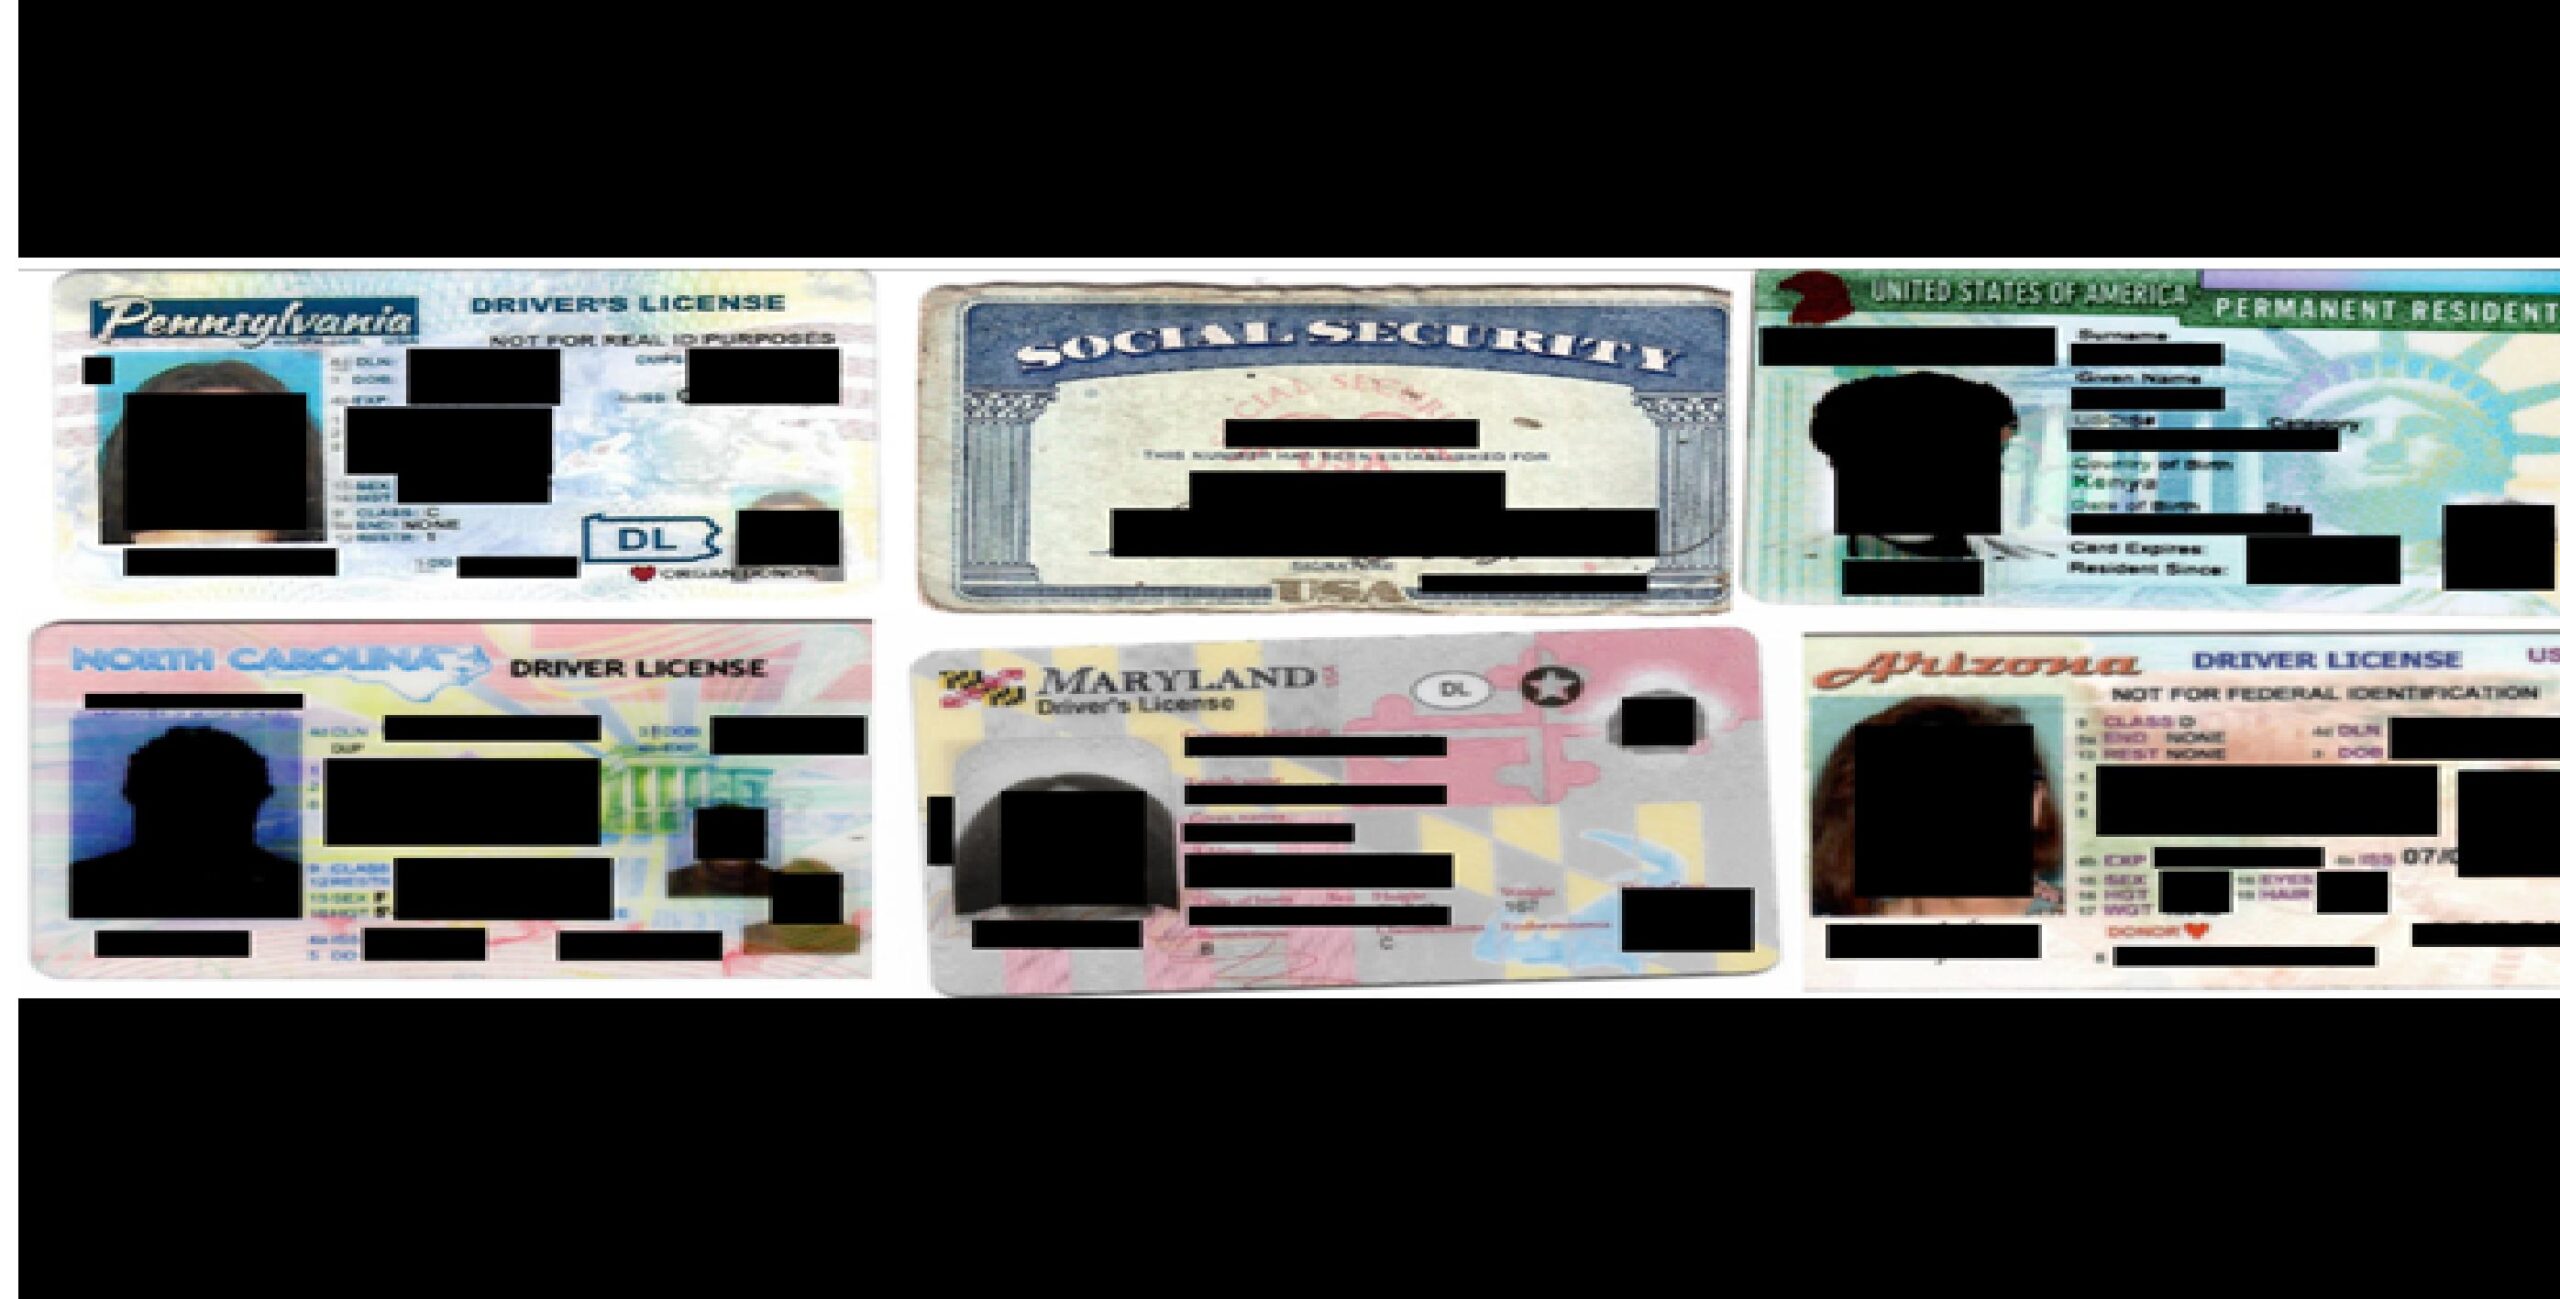
This collage of screenshots shows how identity or tax docuetns appered in the database

The exposed database, which was not password-protected or encrypted, contained 86,341 records and was 108.8 GB in size. Most documents were in a folder labeled “App,” including user profile images, monthly work schedules, professional certificates, work agreements, CVs, and other personal identifiable information (PII). One spreadsheet alone had over 800,000 entries detailing nurses’ IDs, facility names, shift times, and hours worked.

After notifying the issue, the authority tanked the researcher saying “Thank you! we’re actively looking into this and working on a solution” and restricted the dataset from public access.

ESHYFT is a mobile app that links healthcare facilities with qualified nurses. It’s available on both the Apple App Store and Google Play Store, with over 50,000 downloads on Google Play.

Jeremiah Fowler suggested Health tech companies and medical software providers should prioritize cybersecurity to safeguard data and prevent unauthorized access. They should implement mandatory encryption for sensitive information and conduct regular security audits to find vulnerabilities. It’s advisable to limit the storage of sensitive data, anonymize records when possible, and set expiration dates for unused information.


Check Also

email addresses

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Nearly 100,000 Bee Cheng Hiang customers had their email addresses leaked when an employee used …