Thursday , November 12 2026
SuperBlack

CVE-2024-55591 and CVE-2025-24472
New SuperBlack ransomware exploits Fortinet flaws

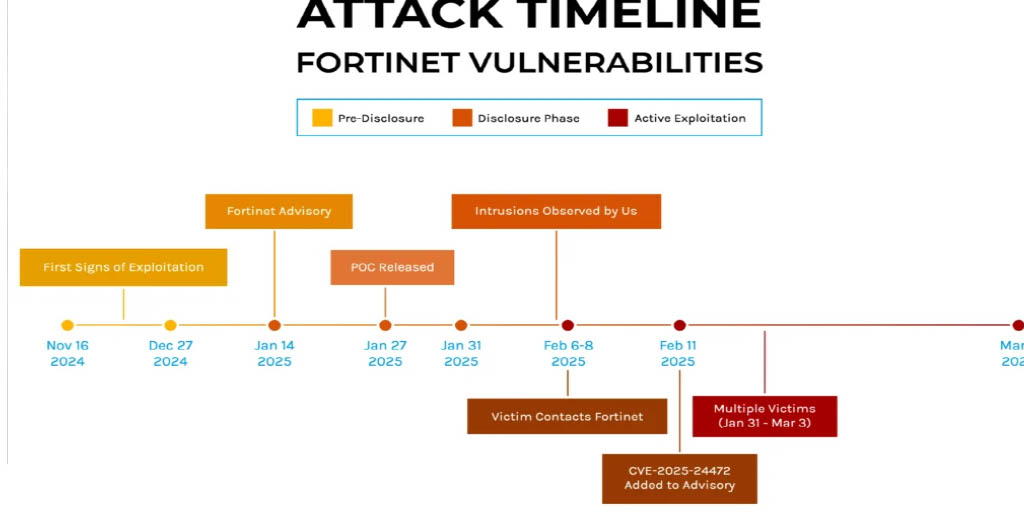
Forescout Research- Vedere Labs identified a series of intrusion based on two Fortinet vulnerabilities which began with the exploitation of FortiGate firewall appliance dubbed SuperBlack. Researchers track this between late january and early March.

Fortinet disclosed two authentication bypass vulnerabilities: CVE-2024-55591 in January and CVE-2025-24472 in February.

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

When Fortinet first disclosed CVE-2024-55591 on January 14, they confirmed it had been exploited as a zero-day, with Arctic Wolf stating it had been used in attacks since November 2024 to breach FortiGate firewalls.

Confusingly, on February 11, Fortinet added CVE-2025-2447 to their January advisory, which led many to believe it was a newly exploited flaw. However, Fortinet told BleepingComputer that this bug was also fixed in January 2024 and was not exploited.

“We are not aware of CVE-2025-24472 ever being exploited,” Fortinet told BleepingComputer at the time.

However, a new report by Forescout researchers, says they discovered the SuperBlack attacks in late January 2025, with the threat actor utilizing CVE-2025-24472 as early as February 2, 2025.

“While Forescout itself did not directly report the 24472 exploitation to Fortinet, as one of the affected organizations we worked with was sharing findings from our investigation with Fortinet’s PSIRT team,” Forescout told BleepingComputer.

“Shortly afterward, Fortinet updated their advisory on February 11 to acknowledge CVE-2025-24472 as actively exploited.”


BleepingComputer reported to wait for a responses from Fortinet to clarify this point.
Source: Forescout, BleepingComputer


Cisco released High Security Alert for IOS XR Software

Check Also

API Connect

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out …