InfoSecBulletin Cybersecurity for mankind
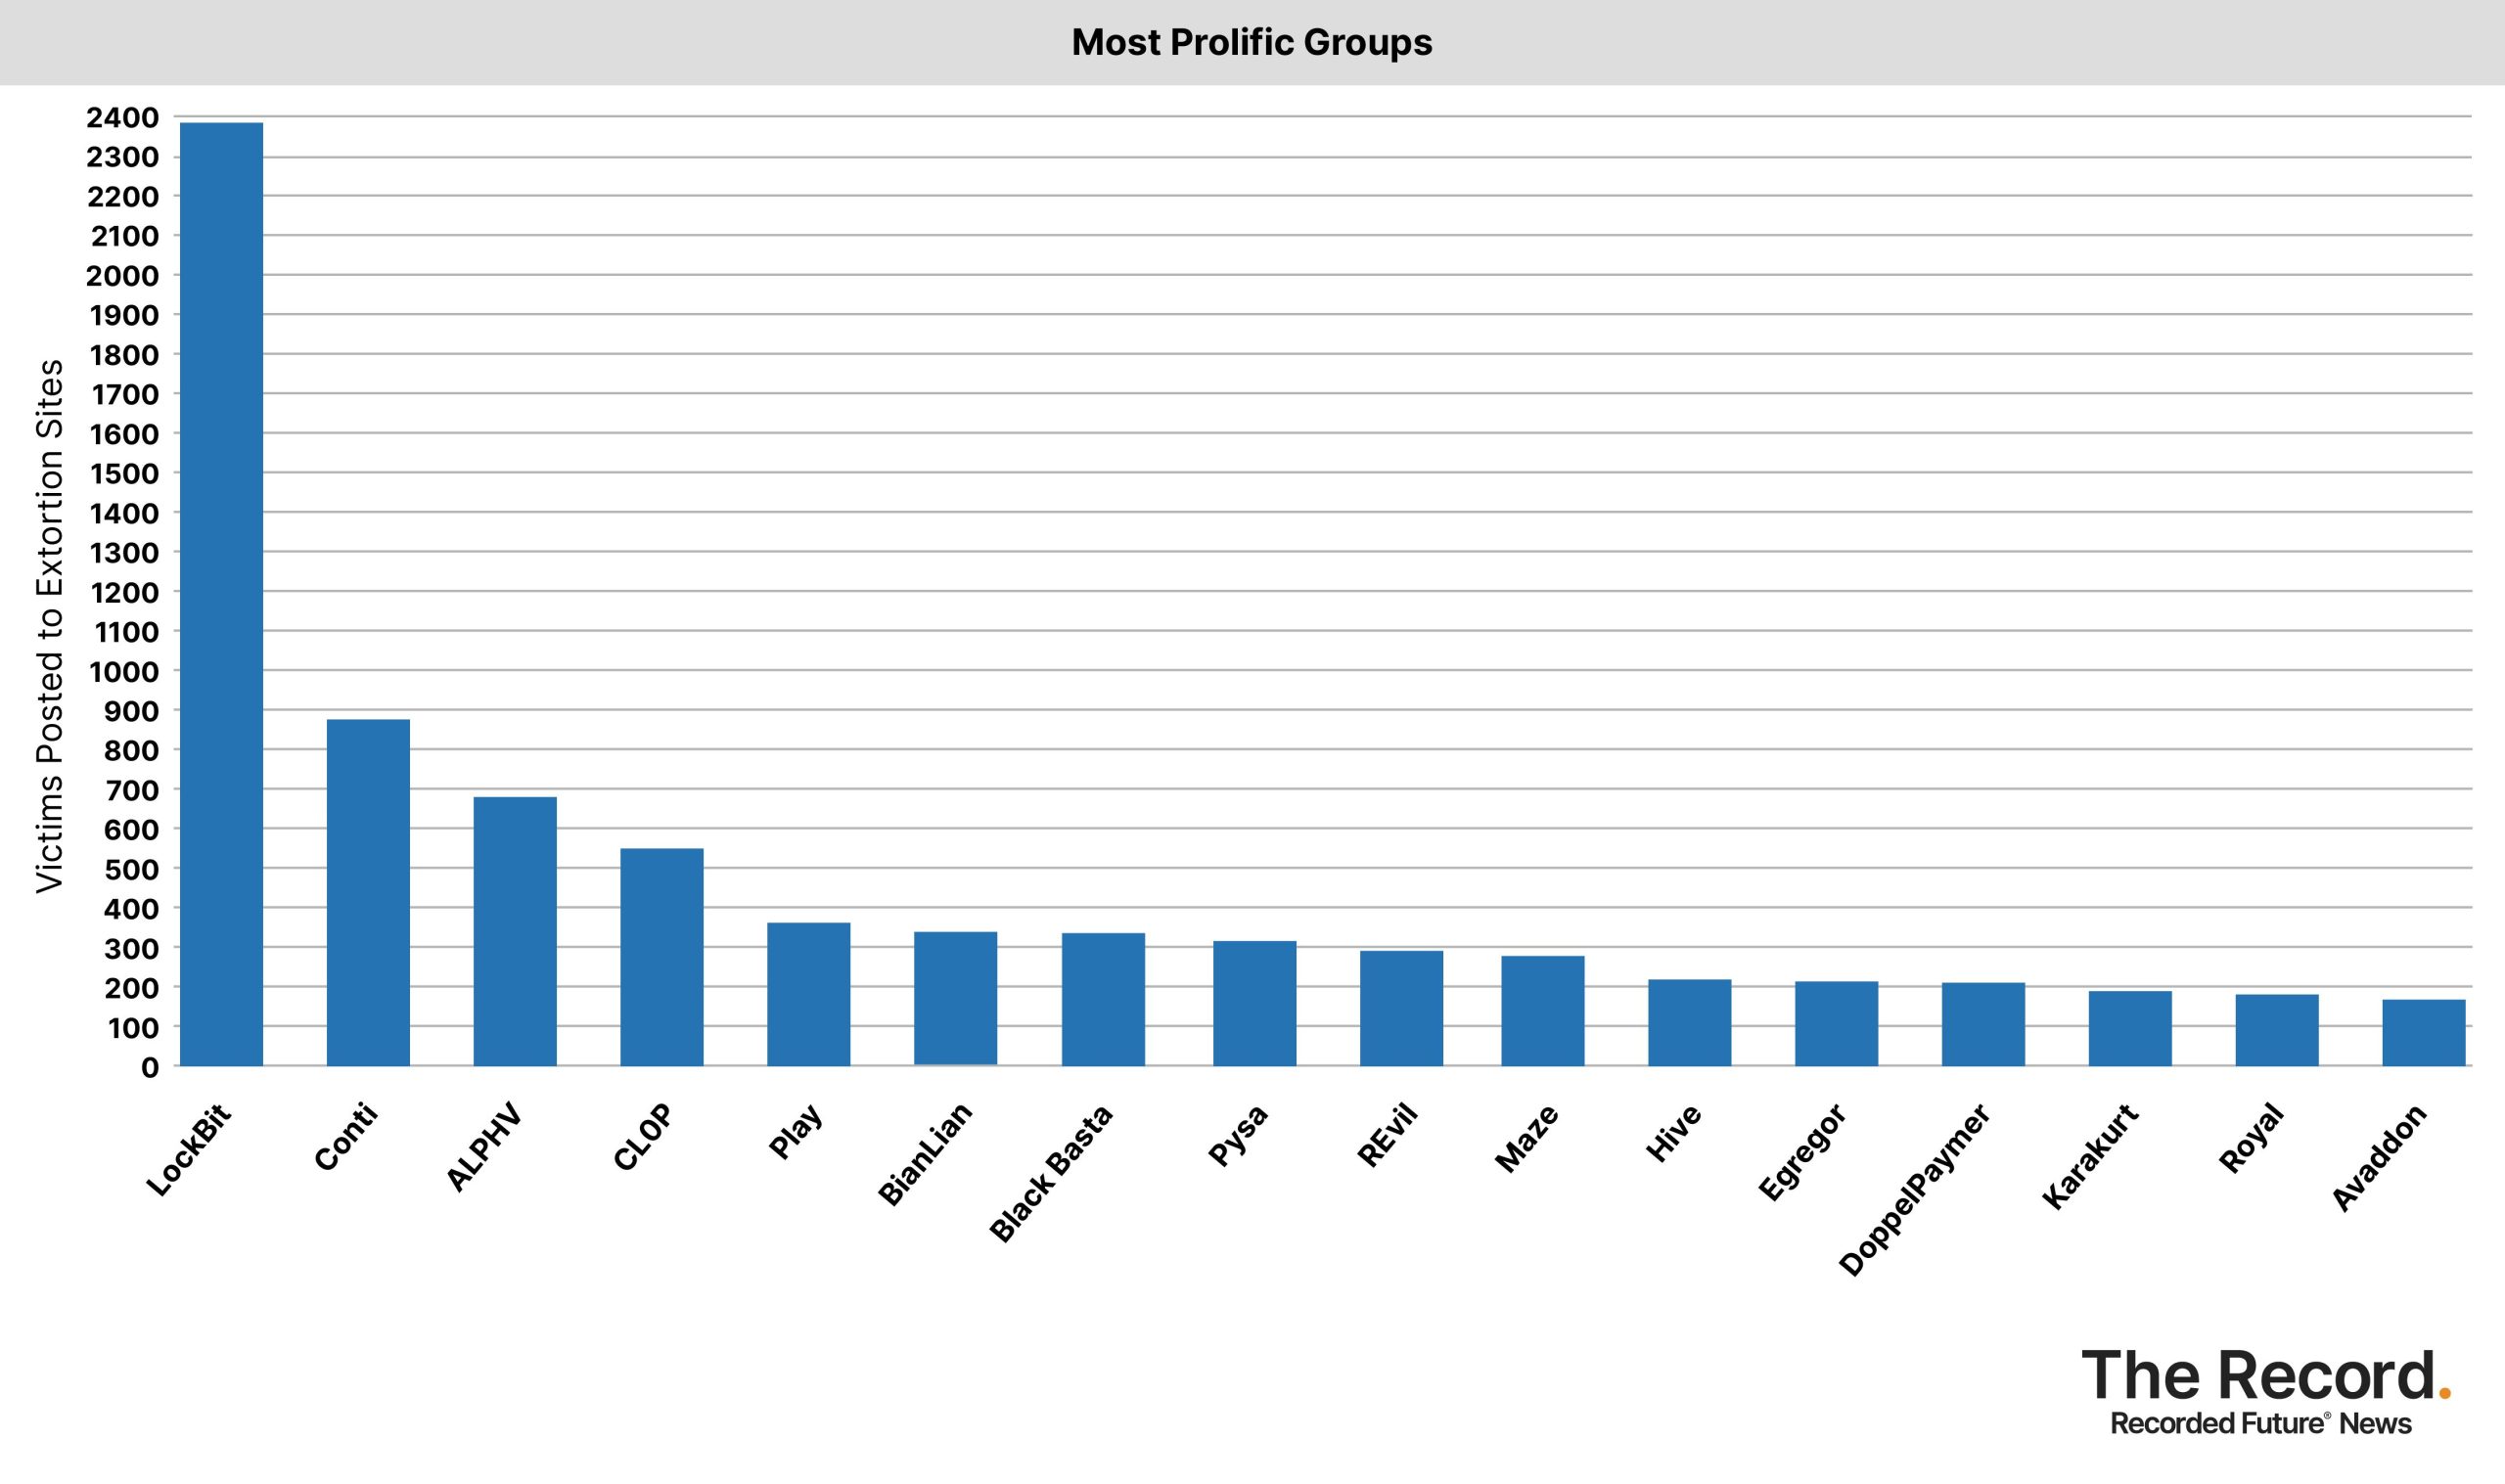
Ransomware attacks increased in several important sectors in February 2024 despite a slow start to the year. In February, ransomware gangs increased the number of victims posted on their extortion sites. There were 310 victims, compared to 242 in the previous month and 229 in February 2023.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

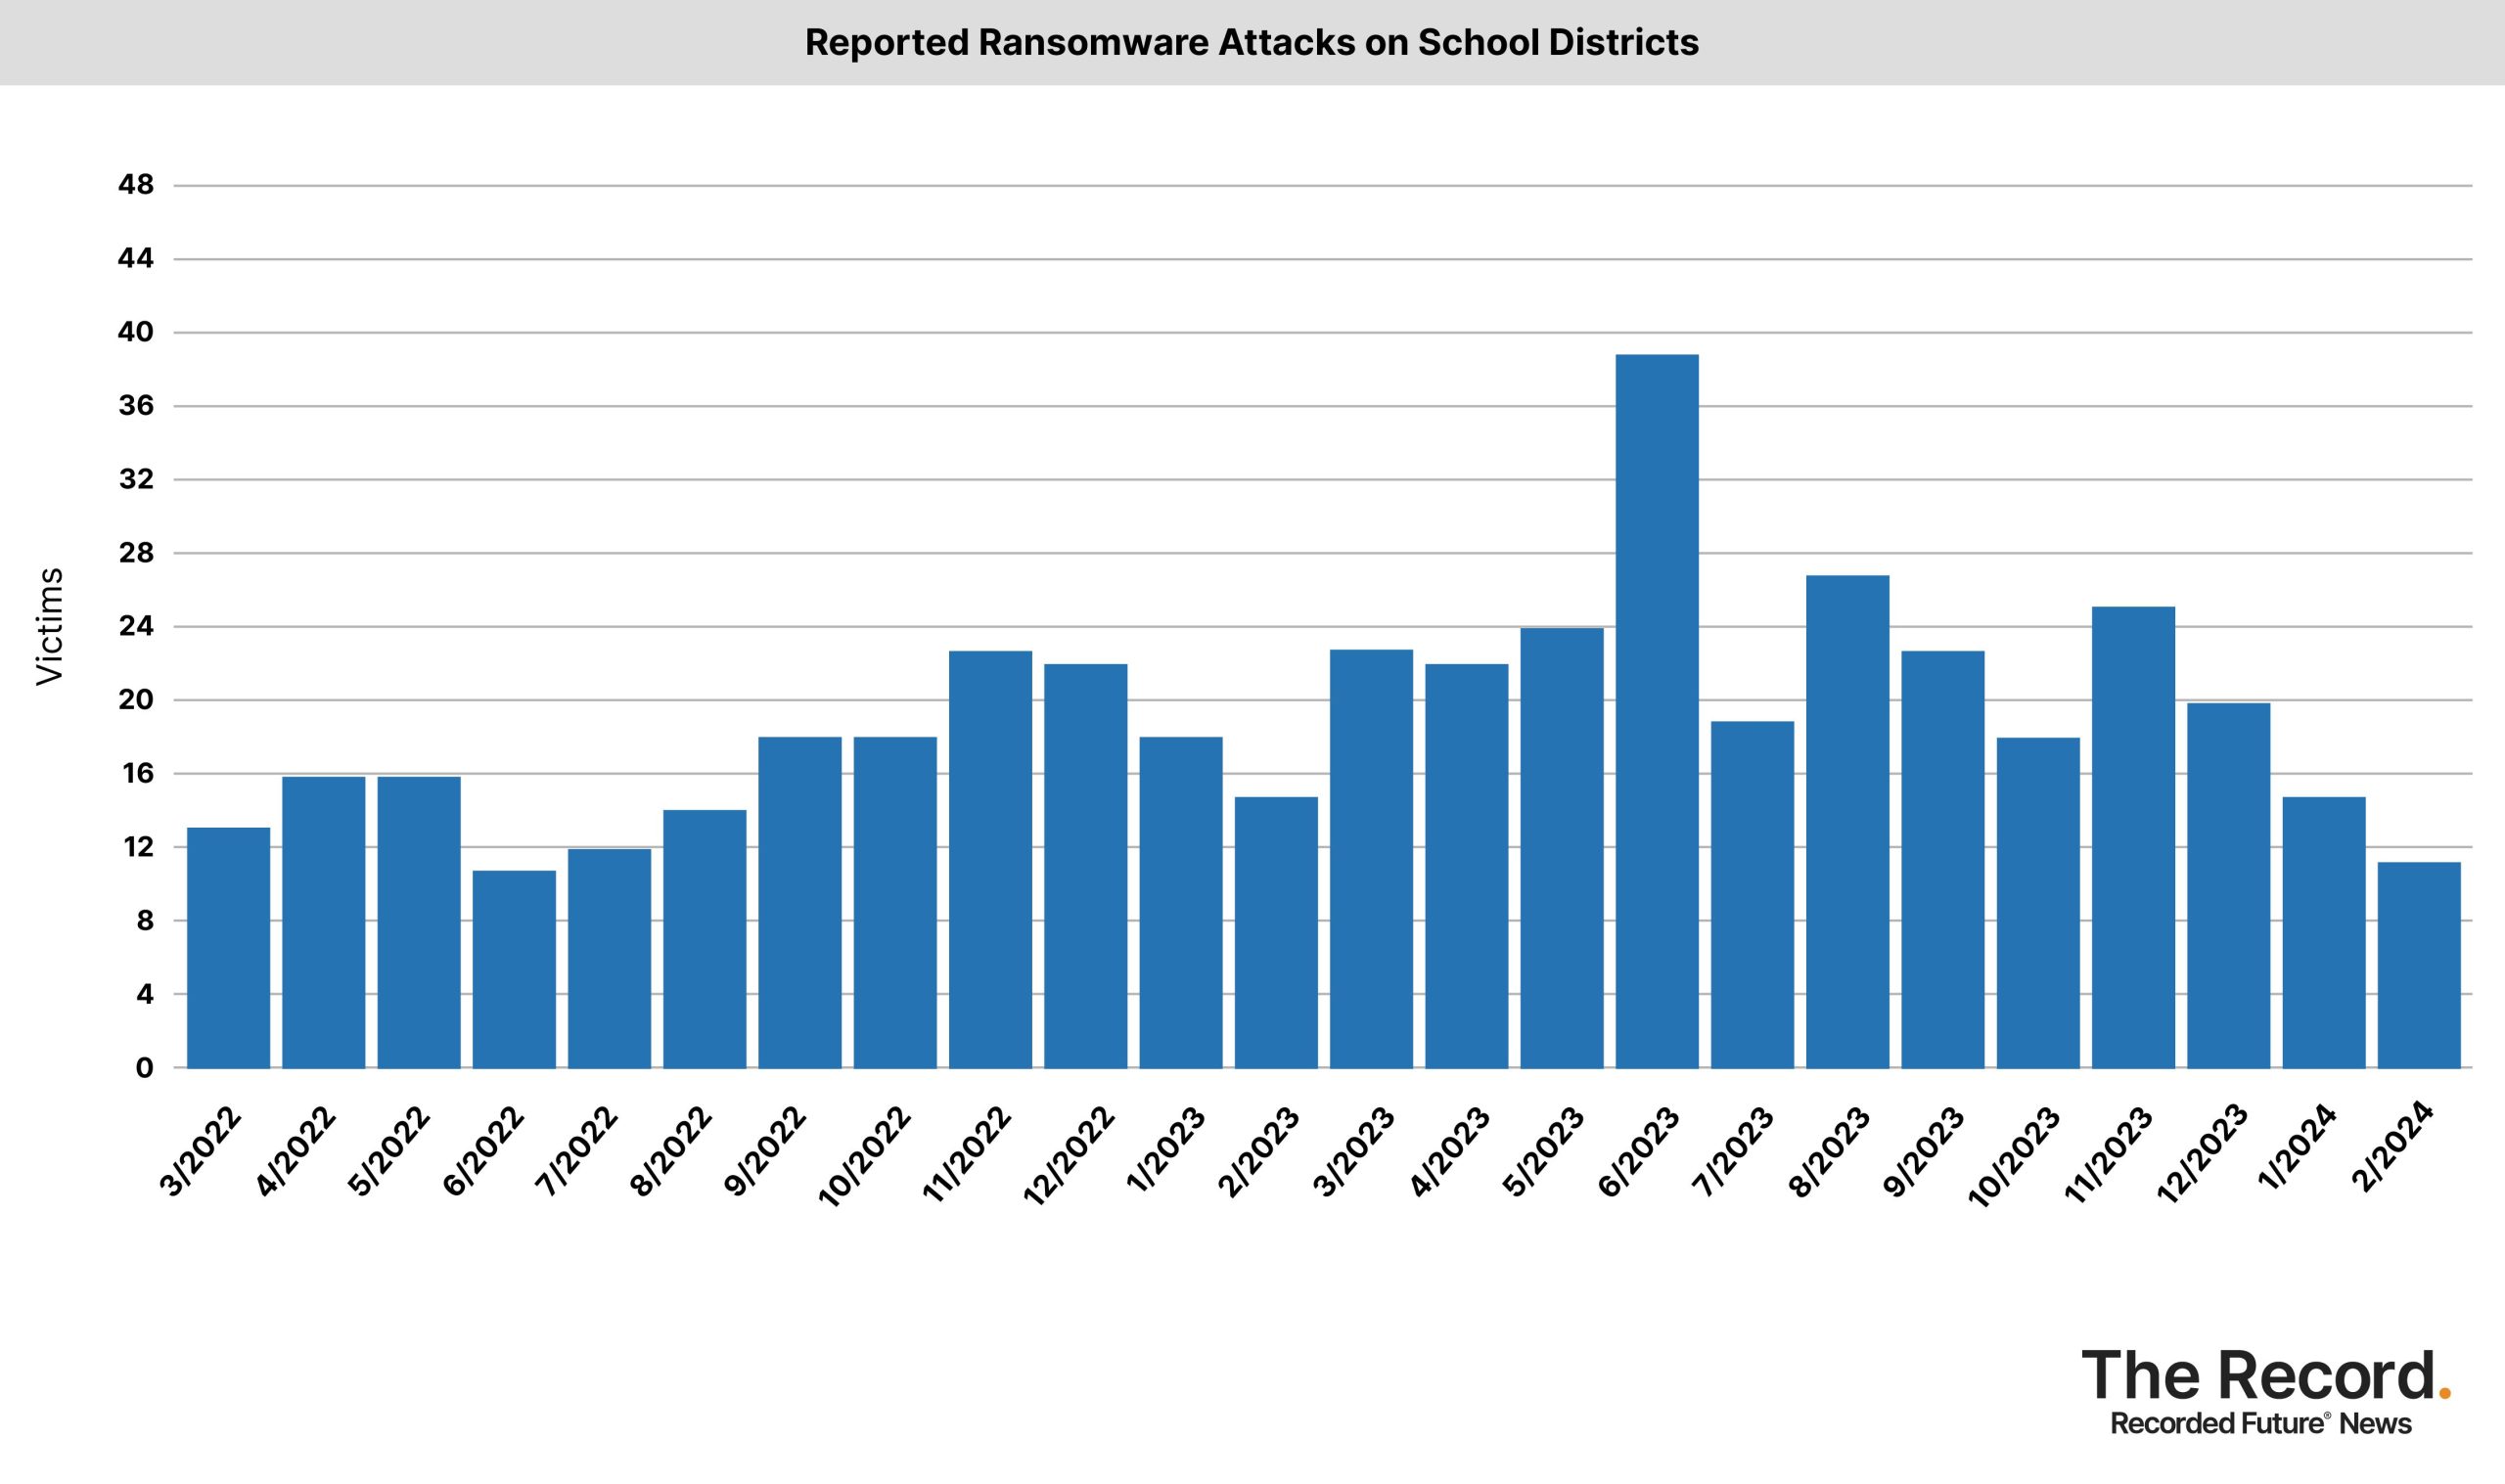
In February, attacks on healthcare providers and state/local governments increased, based on data collected by Recorded Future from various sources including extortion sites, government agencies, news reports, and hacking forums.

A hack targeted Change Healthcare, causing disruptions for pharmacies and hospitals. The BlackCat/Alphv group is responsible and has attempted an exit scam. Law enforcement tried to stop the cybercrime gang in December.
“I think one of the big things we saw in February was the re-emergence of ALPHV after the takedown. Their numbers were way down, compared to before [the takedown], but they were trying to make a comeback,” said Allan Liska, a Recorded Future ransomware expert who helps track and analyze the data.
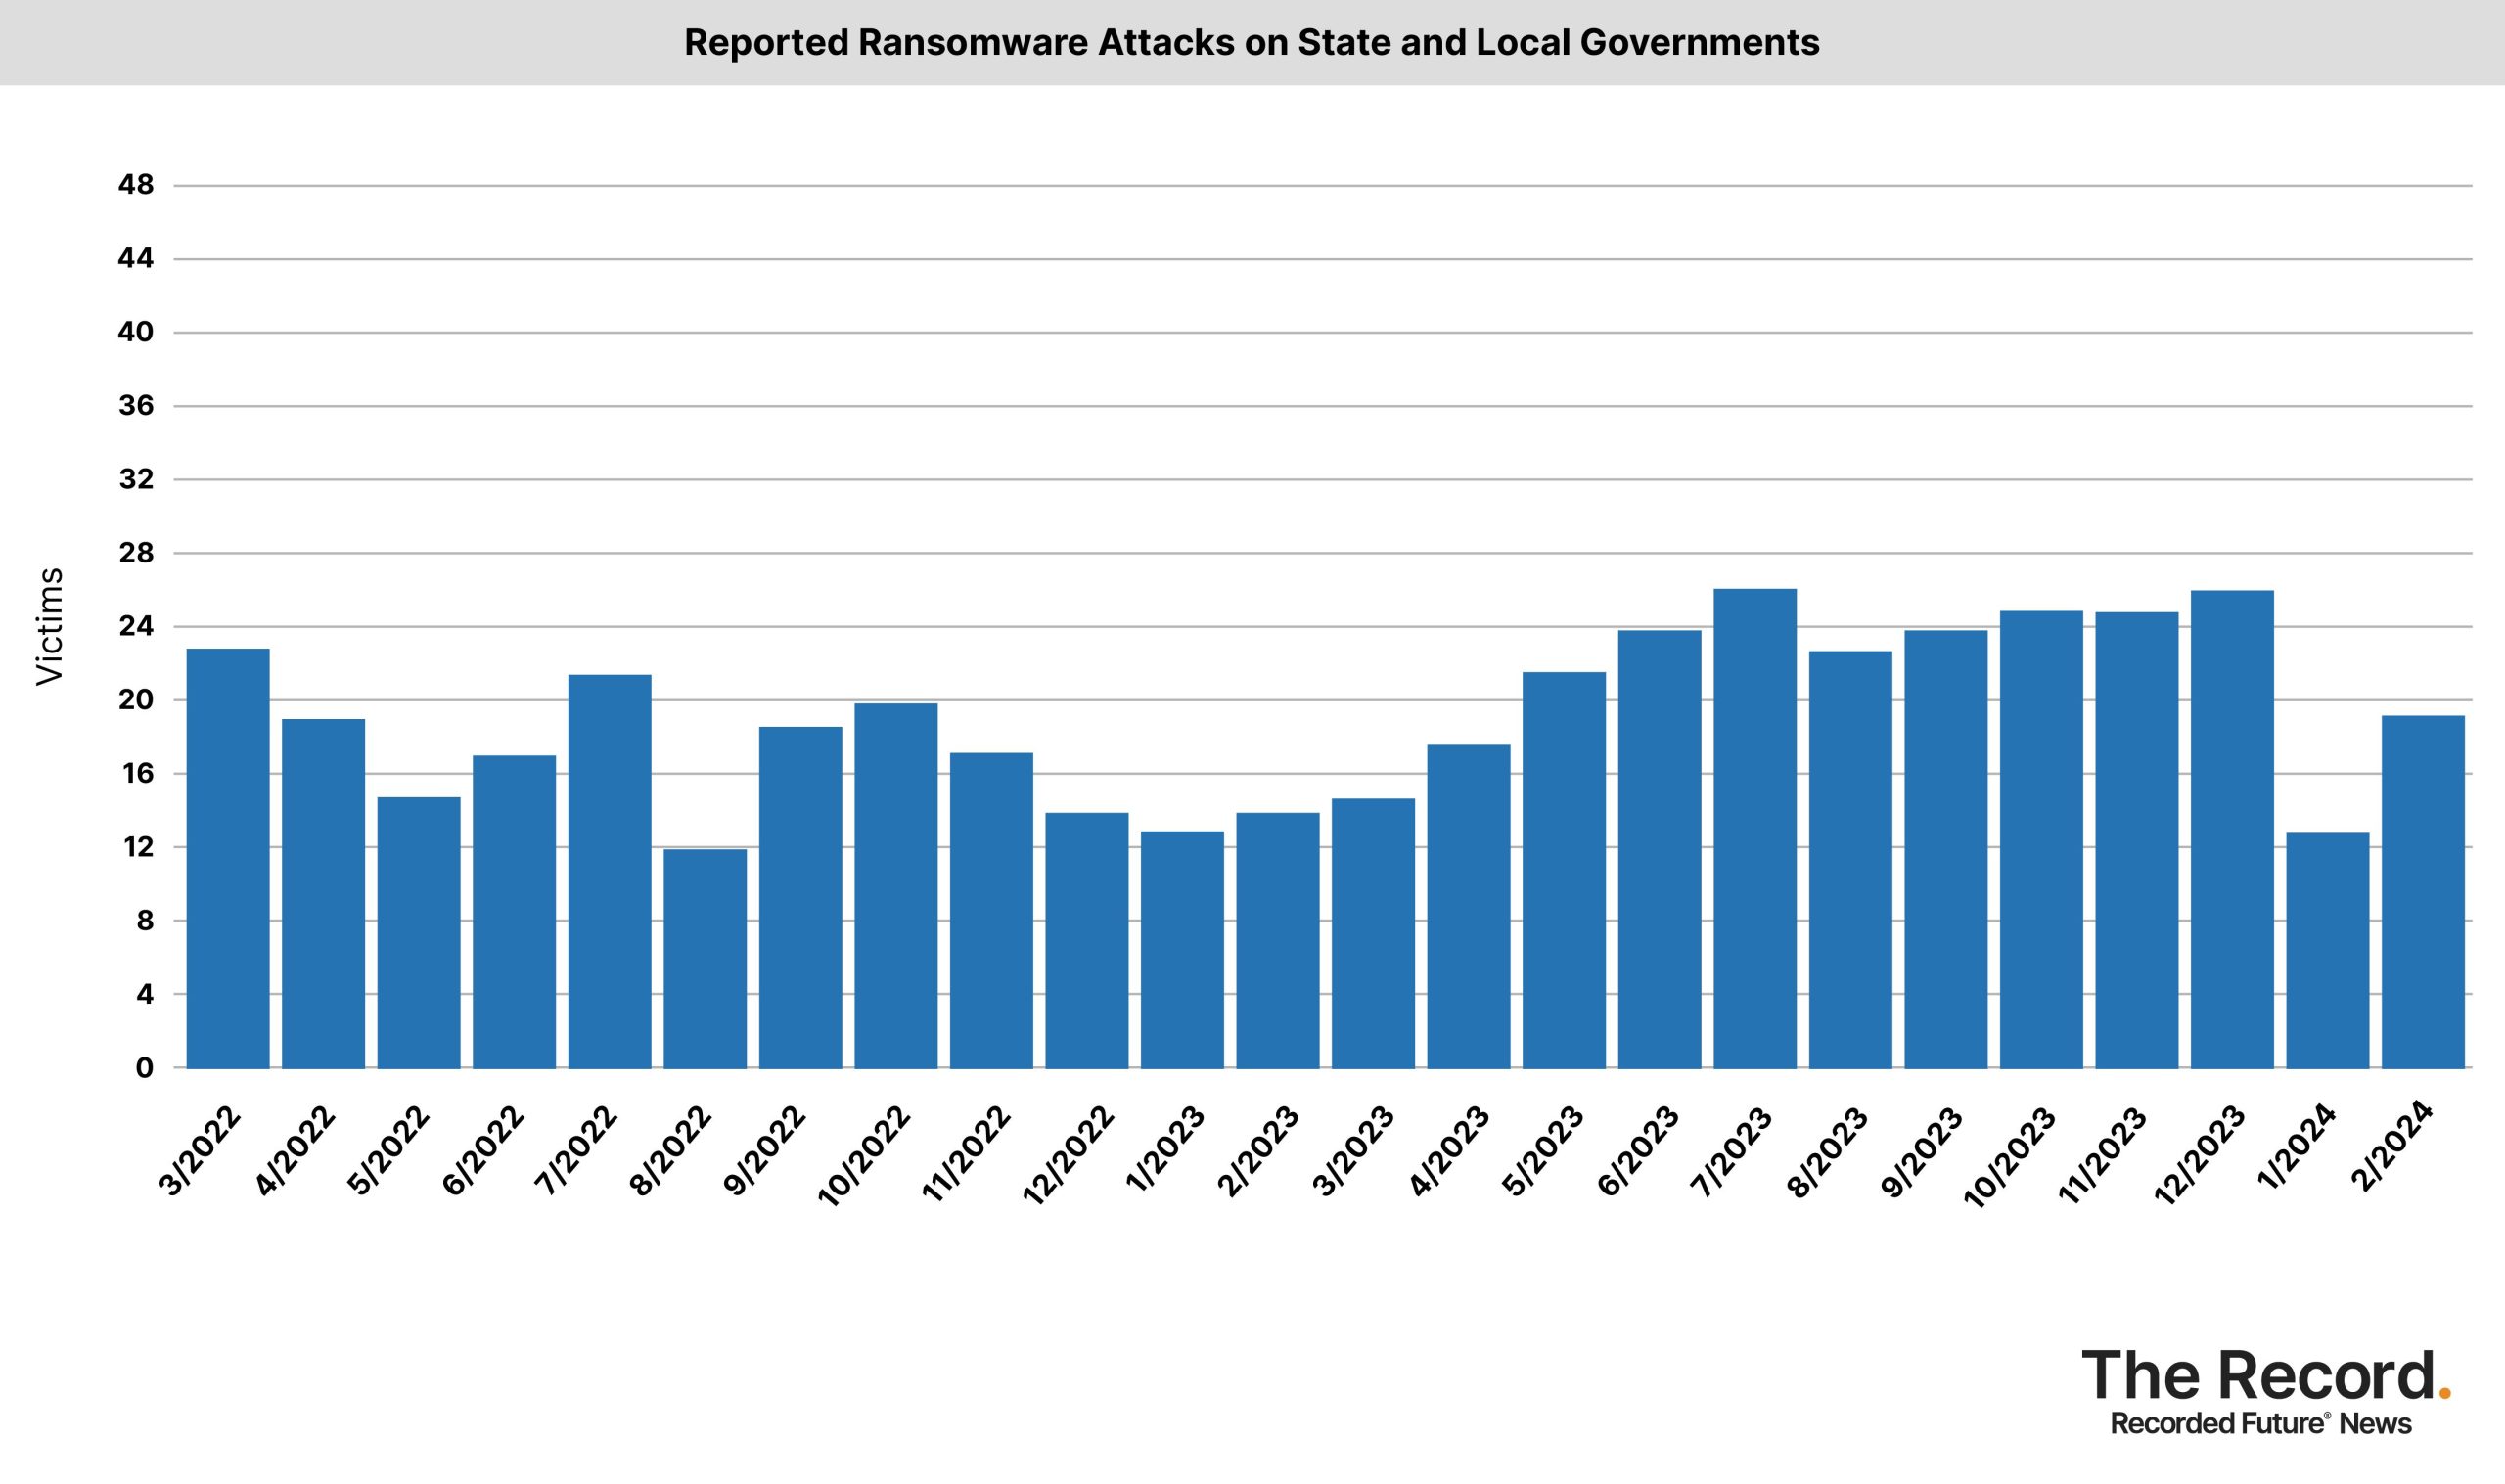
“I think we’re staring to see that takedowns, especially large ones, do have a temporary dampening effect, but ransomware remains resilient. After the LockBit takedown and the ALPHV implosion, the next few months will be interesting to watch,” Lisa added.
In August, the FBI stopped the Qakbot ransomware gang and eliminated the ransomware from infected devices.
In late 2023, law enforcement shut down the Ragnar Locker ransomware site in an international operation. At the same time, Ukrainian hackers claimed to have wiped the servers of the Trigona ransomware gang, which was allegedly linked to Russia.
Source: Record Future