Saturday , October 10 2026
StopCrypt

StopCrypt: Most widely distributed ransomware evades detection

The SonicWall Capture Labs threat research team recently observed a new variant of StopCrypt ransomware. The ransomware executes its malicious activities by utilizing multi-stage shellcodes before launching a final payload that contains the file encryption code.

StopCrypt, also known as STOP Djvu, is a widely spread ransomware, as reported by BleepingComputer. Unlike other ransomware that focuses on big corporations, StopCrypt specifically targets everyday users.

Rise on RCE Exploits Targeting Hikvision Camera Flaw

There was a rise in scanning and remote code execution attempts on video surveillance devices in Ukraine from September 21...
Read More
Rise on RCE Exploits Targeting Hikvision Camera Flaw

FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws CVSS 10

The FBI and U.S. Secret Service released a joint warning about cybersecurity. The warning said that the FortiBleed campaign is...
Read More
FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws  CVSS 10

Contract and server dispute brought down Bangladesh’s digital payment

Bangladesh's digital payments system remains severely disrupted after a technology conflict forces core card and interbank services offline for millions...
Read More
Contract and server dispute brought down Bangladesh’s digital payment

Critical Atlassian & IBM Flaws Expose Files and Enable Remote Code Execution

Atlassian has fixed CVE-2026-21589, a serious flaw in Atlassian Data Center with a score of 9.3. This bug allows an...
Read More
Critical Atlassian & IBM Flaws Expose Files and Enable Remote Code Execution

Citrix NetScaler SAML 0-Day Flaw Under Attack

Citrix has put out emergency security updates for a NetScaler SAML flaw that hackers are using. Known as CVE-2026-88779, this...
Read More
Citrix NetScaler SAML 0-Day Flaw Under Attack

Major Danish university breached, 200,000 users at risk

Hackers got into the identity and access management system at the Technical University of Denmark (DTU) and downloaded a lot...
Read More
Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Microsoft's official X account was taken over to promote an unapproved Clippy-themed cryptocurrency. The tech giant’s X account, with 13...
Read More
Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

CPanel has put out security updates to fix three problems in cPanel & WHM. These problems could let attackers take...
Read More
Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Nearly 100,000 Bee Cheng Hiang customers had their email addresses leaked when an employee used an AI tool to generate...
Read More
Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Hackers to exploit a flaw in Zimbra mail servers that are connected to the Internet. They send special emails that...
Read More
Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

This malware is spread through websites used for sharing copyrighted software. When you download the software, the malware is also downloaded.
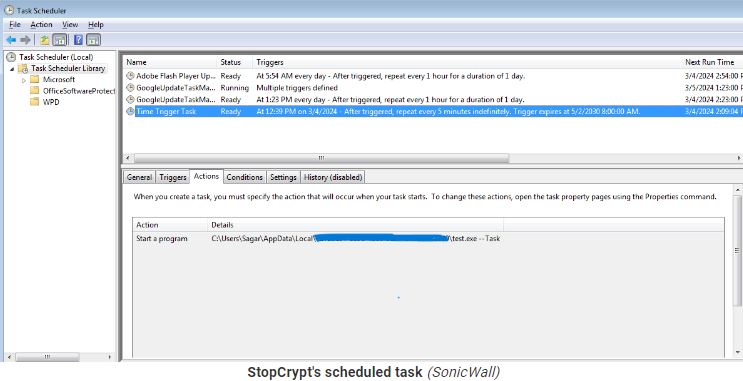
This malware isn’t new, it has been around since 2018, but it has evolved over the years to be harder to detect.

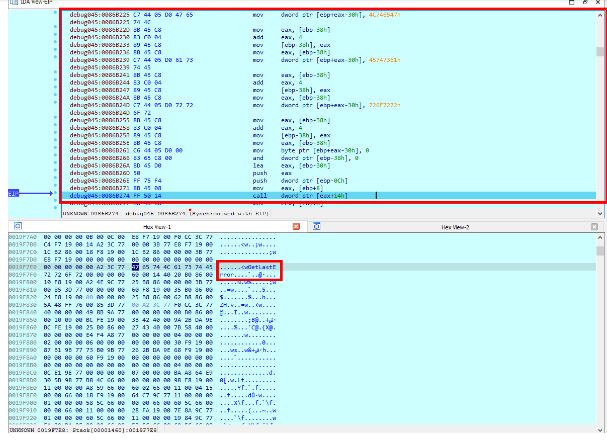
The new version of this malware is more complex and difficult to detect because it uses multiple stages of execution. It also utilizes API calls on the stack to allocate memory.
The malware will take control of other processes and run its code in the background.

Malware can modify access control lists, preventing users from deleting crucial malware files and directories.

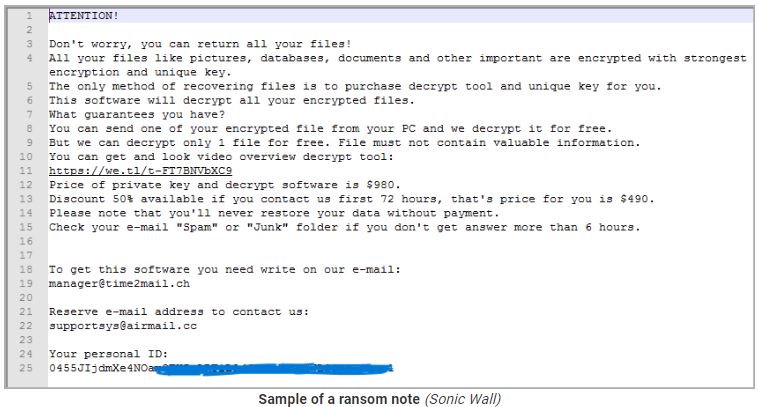
Once everything is done, you will receive a _readme.txt message in each directory with instructions on how to unlock your files.
Source: SonicWall

This malware has been a problem for years. To stay safe, be vigilant and avoid shady websites.

Ransomware is a big threat. It stole data from 27,000 people at Stanford. There are other malwares causing trouble, and a recent one is Vcrums malware targeting browsers.
Check Also

Ransomware

Ransomware Explosion
807 Ransomware Victims Hit in March by 67 Active Hacker Groups

In March, 807 ransomware victims were recorded as per ransomware.live. It is gradually increasing comparing …