InfoSecBulletin Cybersecurity for mankind

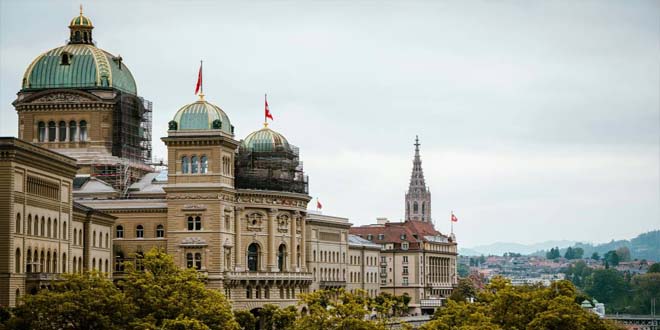
Swiss authorities discovered 65,000 leaked government documents containing classified information and sensitive personal data. The leak occurred after a ransomware attack on an IT vendor last year.
The National Cyber Security Centre (NCSC) of Switzerland recently released a report analyzing the data stolen during a cyber attack in May. The attack was conducted by hackers connected to the Play ransomware gang and targeted IT vendor Xplain. In response to the incident, the government ordered a review, and the NCSC has now published its preliminary findings.
German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

Palo Alto PAN-OS Flaw Enables Root Arbitrary Code Execution

Critical Check Point VPN flaws allow remote code execution attacks

Cisco confirms CVE-2026-20079 flaw in Secure FMC is exploited in attacks

Hackers exploit PaperCut flaws using hundreds of AI agents, compromising 440 servers globally

CISA Says Chinese Firms Extracted Billions of Tokens From Frontier AI Models

Nightmare Eclipse Drops New Microsoft Defender ‘ShieldCrash’ zero-day

cPanel Flaw Lets Hosting Accounts With Mail Privileges Execute Code as Root

FortiSandbox, FortiOS, FortiProxy ZTNA flaws unveil, while Fortigate firewall actively exploited

1.3 million files were published on the dark web. Approximately 5% of those files were related to the country’s federal government.
Most of the files belonged to Xplain and were related to the company’s work with the government. However, around 14% of the files came directly from the country’s federal administration.
Most of the government files were from the administrative units of the Federal Department of Justice and Police. These units include the Federal Office of Justice, Federal Office of Police, State Secretariat for Migration, and the internal IT service center ISC-FDJP, according to the NCSC.
“With just over 3% of the data, the Federal Department of Defence, Civil Protection and Sport (DDPS) is slightly affected and the other departments are only marginally affected in terms of volume,” the agency said.
The files included personal data, technical information, classified documents, and passwords. Names, email addresses, phone numbers, and addresses were found in about 4,700 files. More than 250 files contained technical information, like documentation on IT systems, software requirement documents, or architectural descriptions.
The investigation will be completed by the end of March. A report will then be sent to the Federal Council of the country.
The Play ransomware group said they attacked on May 23 and leaked 907 gigabytes of financial and other data on June 1. Since June 2022, Play ransomware has caused over 300 cyberattacks, according to the FBI.