 InfoSecBulletin Cybersecurity for mankind
Security researchers have warned that a Proof-of-Concept (PoC) exploit has been publicly released for a critical vulnerability affecting Oracle WebLogic Server.
The flaw tracked as CVE-2024-21182, poses a significant risk to organizations using the server, as it allows an unauthenticated attacker with network access to compromise the targeted system.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The vulnerability impacts Oracle WebLogic Server versions 12.2.1.4.0 and 14.1.1.0.0, among the most widely used middleware solutions for deploying enterprise applications.
The exploitation is possible through T3 and IIOP (Internet Inter-ORB Protocol), which are commonly enabled by default for remote communication.
Cybersecurity advisors have highlighted that this vulnerability is classified as “easily exploitable.”
An attacker can leverage it without requiring credentials or sophisticated technical expertise, broadening the scope of potential misuse.
According to the advisory, successful exploitation could lead to arbitrary code execution, granting attackers full control over the compromised server.
Concerns surrounding CVE-2024-21182 grew rapidly after an exploit was shared on GitHub by a user named “k4it0k1d.”
The repository includes a ready-to-use PoC that lowers the barrier for potential attackers. Cybersecurity updates posted on social media platforms, such as X (formerly Twitter), have also drawn attention to the vulnerability.
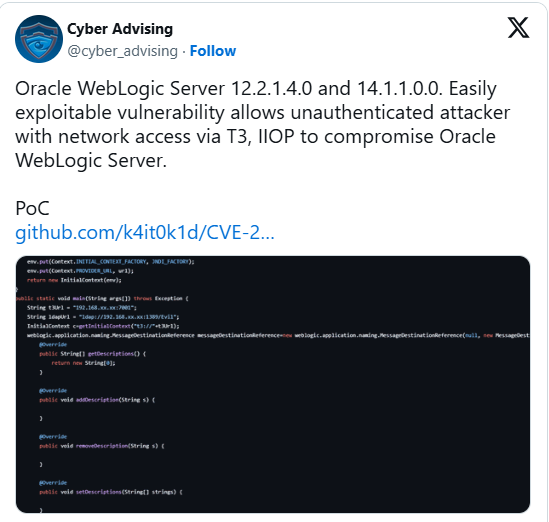
A post shared by Cyber Advising includes a link to the exploit and warns of its accessibility.
With the exploit now public, proactive defense measures are critical to protecting sensitive systems and data.



