 InfoSecBulletin Cybersecurity for mankind
The US Treasury Department said on Monday that Chinese-linked hackers were able to gain access to ‘unclassified documents’ after compromising the agency’s networks earlier this month.
According to a US Treasury letter addressed to US Senators Sherrod Brown (D-OH) and Tim Scott (R-SC) on Monday – the Chinese hackers gained access to the documents via a third-party vendor responsible for providing cybersecurity services to the agency.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The cybersecurity firm, BeyondTrust, was the first to become aware of the breach, alerting the Treasury Department on December 8th.
According to the Treasury, the hackers broke into employee workstations and were able to access the documents using a stolen key to its cloud-based tech support platform. The letter called the state-sponsored cyberattack a “major incident,” under US Treasury guidelines.
Attributed to a Chinese APT (advanced persistent threat), the Beijing threat actors “gained access to a key used by the vendor to secure a cloud-based service used to remotely provide technical support for Treasury Departmental Offices (DO) end users,” the letter said.
Once the key was in their possession, the hackers were able to “override the service’s security, remotely access certain Treasury DO user workstations, and access certain unclassified documents maintained by those users,” it stated.
Following incident response protocols, the compromised BeyondTrust service was taken offline, disrupting any further access to Treasury information.
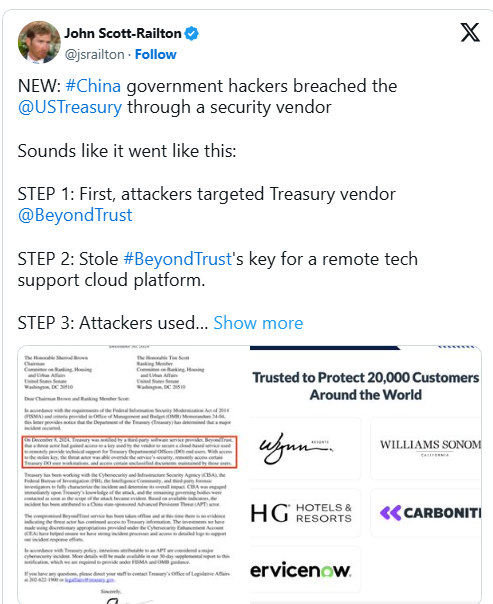
Senior Researcher John Scott-Railton of the Citizen Lab at the University of Toronto posted about the incident on X noting that the “attackers used the platform like a backdoor on Treasury machines where it was installed.”
“Given BeyondTrust’s big client list, makes one wonder if other customers were targeted,” he commented.
The letter also said that the US Cybersecurity and Security Infrastructure Agency (CISA) was immediately notified and an official investigation was launched with the FBI and other third-party experts.
A spokesperson for BeyondTrust, based in Johns Creek, Georgia, told Reuters in an email that the company “previously identified and took measures to address a security incident in early December 2024” involving its remote support product. BeyondTrust “notified the limited number of customers who were involved,” and law enforcement was notified, the spokesperson said. “BeyondTrust has been supporting the investigative efforts.”
Referring to a statement on its website updated on December 18th, the cybersecurity firm said it had “notified the limited number of customers who were involved.” The spokesperson added that “BeyondTrust has been supporting the investigative efforts.”
Meantime, Tom Hegel, a threat researcher at SentinelOne, said the reported security incident “fits a well-documented pattern of operations by PRC-linked groups, with a particular focus on abusing trusted third-party services – a method that has become increasingly prominent in recent years,” although added that BeyondTrust had not officially confirmed the link.
A spokesperson for the Chinese Embassy in Washington on Monday denied involvement, instead stating that Beijing “firmly opposes the US smear attacks against China without any factual basis,” Reuters reported.
CISA and the FBI had no formal comment as of Monday.
“Beijing has hit back at accusations that a China state-sponsored actor was behind a cyber breach at the US treasury department, calling the claims “groundless”.
On Tuesday, China denied the claims, with the foreign ministry saying Beijing “has always opposed all forms of hacker attacks, and we are even more opposed to the spread of false information against China for political purposes”.
“We have stated our position many times regarding such groundless accusations that lack evidence,” the foreign ministry spokesperson Mao Ning said, reported by The Guardian.



