 InfoSecBulletin Cybersecurity for mankind
A recent Aqua Security report highlights major security risks in Kubernetes policy enforcement, especially with Open Policy Agent (OPA) Gatekeeper. Although OPA Gatekeeper is commonly used for security policies in Kubernetes, researchers found methods to bypass its controls due to frequent misconfigurations and weak policies.

According to the report, “Implementing Kubernetes securely can be a daunting task.” OPA Gatekeeper is an essential tool that provides out-of-the-box security policies for Kubernetes, but Aqua Security’s research highlights critical flaws that may allow attackers to evade restrictions. The report warns that “seemingly secure rules, such as those used in OPA Gatekeeper, can be bypassed if not carefully configured.”
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

A key vulnerability identified is the ability to bypass the k8sallowedrepos policy, which limits access to certain container image repositories. Researchers found that misconfigurations, like missing trailing slashes in policies, can allow unauthorized image pulls. “We found a way to bypass the k8sallowedrepos policy. If the user omits placing / at the end of the constraint repos value, this enables attackers to completely bypass the policy,” the report states.
Two major attack scenarios were demonstrated in the report:
Domain Bypass:

If an organization restricts images to my-ecr.azurecr.io, attackers can exploit the absence of a trailing slash by using a subdomain like my-ecr.azurecr.io.attacker.com. Kubernetes may mistakenly accept this as a valid source, circumventing security measures.
Docker Hub Namespace Bypass:
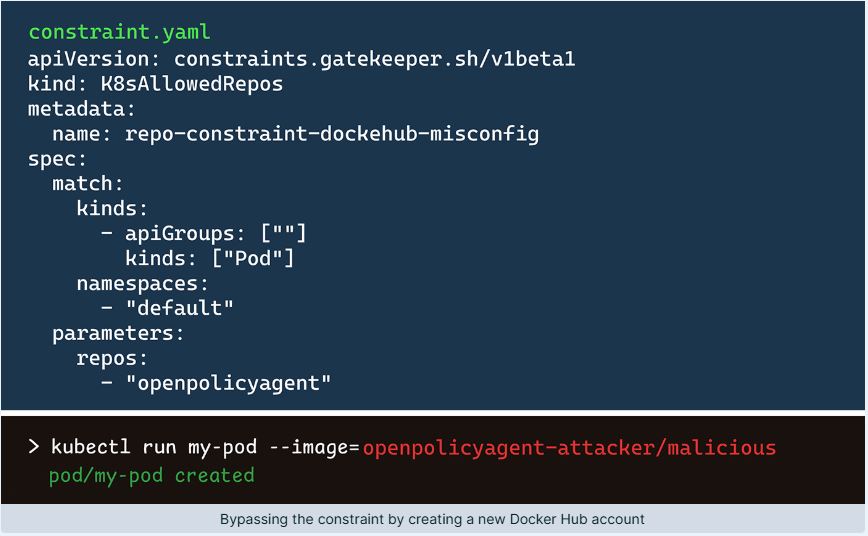
The report explains that attackers can create misleading repositories on Docker Hub, like “openpolicyagent-attacker,” to exploit poorly configured policies. It highlights a method called “namespace bypass,” allowing attackers to use repository names that match permitted values.
A major concern is the Rego policy logic in OPA Gatekeeper. The report notes that functions like any_prefix_match() can be misused to match unintended values, enabling attackers to deploy malicious containers. Using functions such as endswith(), startswith(), and any_prefix_match() on domains, repositories, or namespaces poses risks.



