Thursday , November 12 2026
Trojan

New Banking Trojan “CHAVECLOAK” Targets Brazil

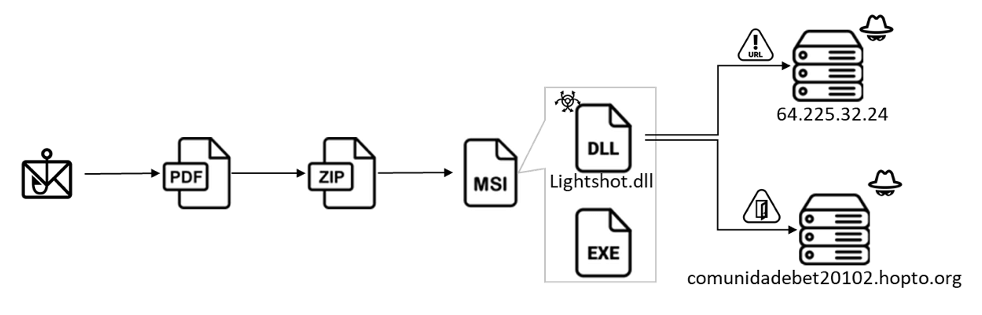
FortiGuard Labs found a threat using a harmful PDF to spread the CHAVECLOAK banking Trojan. The attack involves the PDF downloading a ZIP file and then using DLL side-loading to run the malware. CHAVECLOAK targets Brazilian users to steal financial information. Figure 1 shows the detailed flow of this cyber threat.

Figure 1: Attack flow

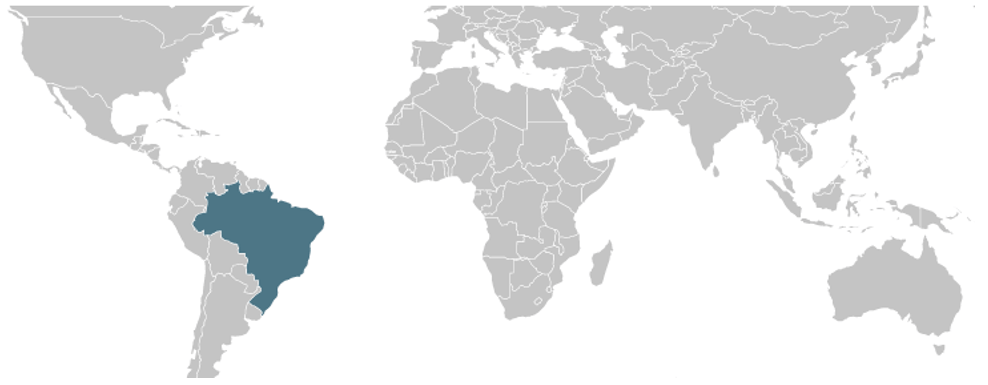
Banking trojans in South America use various tactics, like phishing emails, malicious attachments, and manipulating web browsers. Some examples are Casbaneiro (Metamorfo/Ponteiro), Guildma, Mekotio, and Grandoreiro. These trojans focus on stealing online banking credentials and personal information, which poses a major threat to users in countries like Brazil and Mexico. Figure 2 shows the telemetry of CHAVECLOAK’s Command and Control (C2) server.

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026
Figure 2: Telemetry

Initial Vector PDF:

Figure 3 shows a PDF that allegedly contains contract-related documents with Portuguese instructions. The PDF prompts users to click a button to read and sign the attached documents. However, there is a hidden malicious downloader link in the PDF’s stream object, as revealed in Figure 4. This URL undergoes processing via the free link shortening service “Goo.su,” ultimately leading to a redirect at hxxps://webattach.mail.yandex.net/message_part_real/NotaFiscalEsdeletronicasufactrub66667kujhdfdjrWEWGFG09t5H6854JHGJUUR[.]zip for downloading the ZIP file. Upon decompression, the file yields the MSI file “NotafiscalGFGJKHKHGUURTURTF345.msi.”
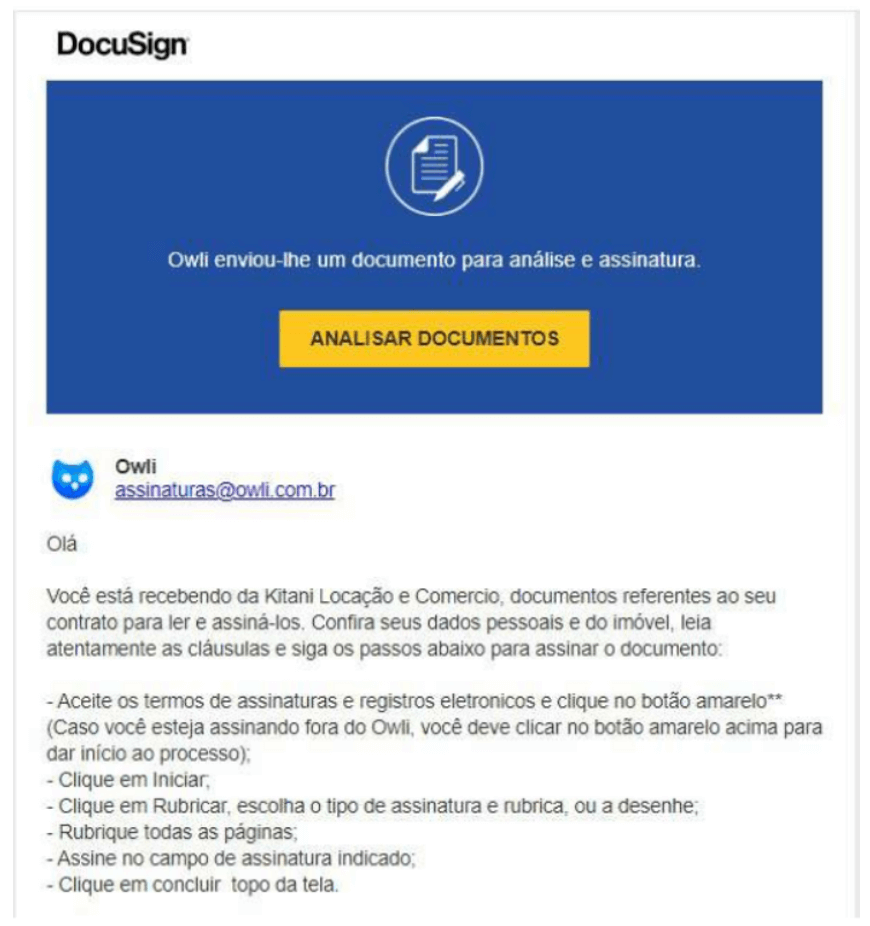
Figure 4: The embedded URL

Upon decompressing the MSI installer, researchers found additional files including TXT files for different languages, a legitimate execution file, and a suspicious DLL named “Lightshot.dll” with a more recent modified date compared to other files.
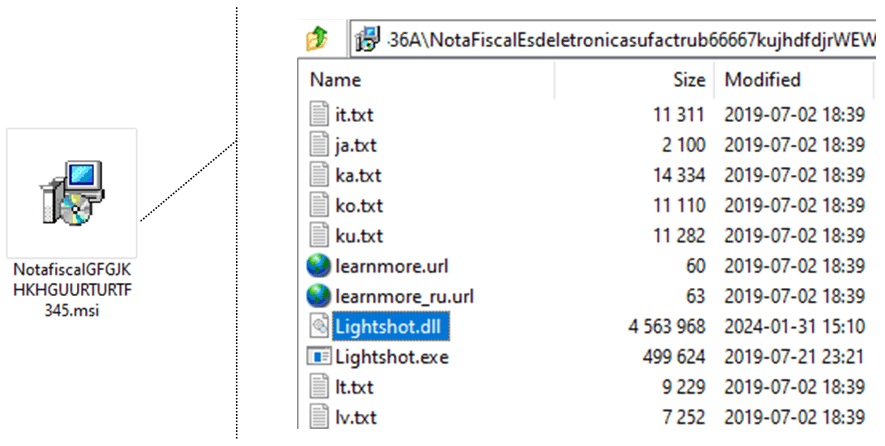
Figure 5: The decompressed MSI file

Examining the MSI installer reveals its entire configuration, which is written in Portuguese. It executes the file “Lightshot.exe,” extracting and depositing files at “%AppData%\Skillbrains\lightshot\5.5.0.7,” as shown in Figure 6.
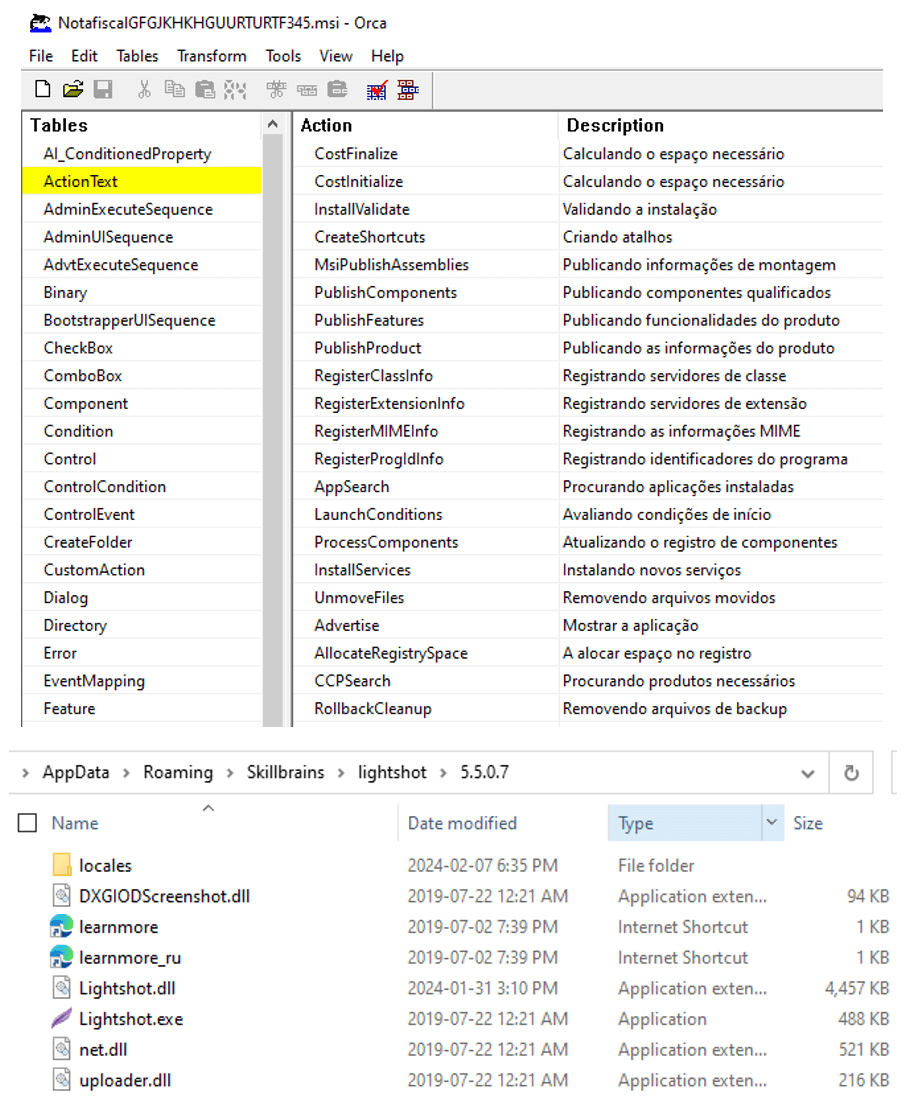
Figure 6: The “ActionText” in the MSI file and the extracted folder

The file “Lightshot.exe” uses DLL sideloading to run the malicious “Lightshot.dll” discreetly, allowing unauthorized activities like data theft. This technique poses a significant security threat by letting malware exploit legitimate processes for harmful purposes without being detected. To read out the full report click here.

Source: FortiGuard Labs

Check Also

973 flaws

Microsoft Patch Tuesday September 2026 Fixed 973 Flaws Fixed, 2 Zero-Days

Microsoft shared its September 2026 security updates on September 8. These updates fix 973 flaws, …