 InfoSecBulletin Cybersecurity for mankind
The Cyber Threat Intelligence Unit at BGD e-GOV CIRT has noticed an increase in cyber-attacks on organizations. These attacks are aimed at compromising third-party service providers. Several organizations in Bangladesh have experienced data breaches.
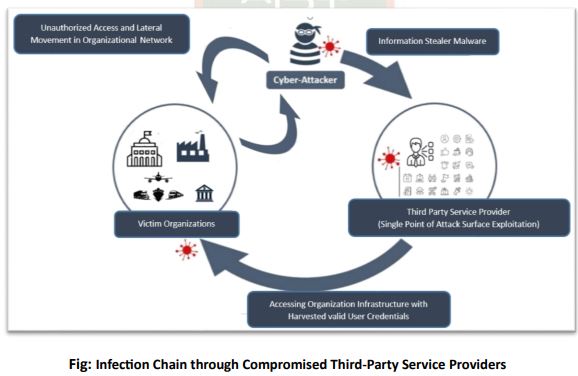
Some individuals employed by third party service providers, tasked with offering technical support to various client organizations, have been targeted by information-stealing malware.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The malware stole important data like system information, browser cookies, and user account credentials. Then, the hackers used this stolen data to get into the client organizations’ networks without permission. The attack got worse quickly, as the hackers used advanced techniques to gain more access to important assets and move around within the compromised organization.
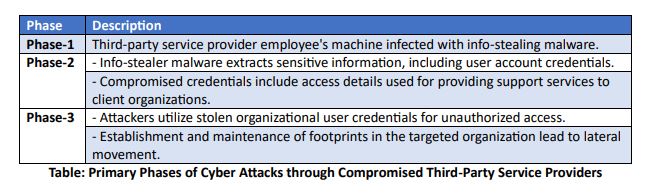
BGD e-GOV CIRT issues this alert to all organizations in Bangladesh, warning about the significant risks stemming from compromises at third-party service providers. CIRT strongly encouraged organizations to take proactive steps to protect their assets from potential attacks.
CIRT instructs some the preventive measures to follow for attack risks originating from third party service
providers:
1. Clearly define access control policies for third-party employees.
2. Limit network access to specific segments required for their tasks.
3. Use VPN with strict access policies.
4. Provide regular phishing awareness training.
5. Enforce device security policies.
6. Use temporary credentials with limited validity.
7. Monitor and audit their activities.
8. Establish an incident response plan.
9. Include security requirements in contractual agreements and CIRT mention to their cyber threat alert that organization to report any incidents to BGD e-GOV CIRT at [email protected].



