 InfoSecBulletin Cybersecurity for mankind
Jeremiah Fowler, a cybersecurity researcher, found an unprotected server revealing 378 GB of Navy Federal Credit Union files, including operational Tableau data, but no customer details.
The misconfigured server has been found with sensitive internal files from Navy Federal Credit Union (NFCU), the largest credit union for military members.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

He discovered unencrypted backup data in an open database that anyone could access without a password.
The 378 GB database didn’t have any plain text credit union member data, but it did expose internal usernames, email addresses, and possibly hashed passwords and keys.
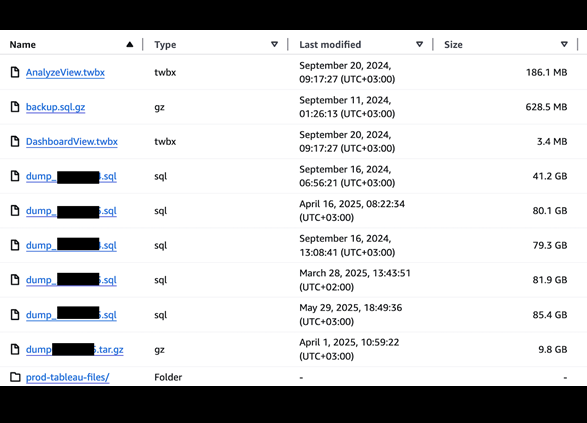
Fowler’s screenshots verified user roles in the credit union. He also discovered many Tableau workbooks in the database, which are files used for data analysis. These files included important details like connections to other internal databases and formulas for calculating financial metrics like loan performance and profits.
This information, while not customer data, could act as a “blueprint” for how the credit union’s internal systems operate. Furthermore, the backup files included important system information, such as logs, product codes, and data that should have remained private.
Although customer data wasn’t directly exposed, the security issue poses a significant risk. Fowler notes that this leaked information can guide criminals in future attacks. Hackers might use the leaked internal emails and names to craft convincing phishing attempts, allowing them to gain deeper network access.
“These files can sometimes be just a representation of the production data, but they still may reveal underlying structures or metadata that indicate how the backup software associates or connects these files to production systems,” Fowler noted in his report.
Fowler quickly informed NFCU, and they secured the database within hours. However, it’s unclear how long it was exposed or if anyone else accessed the data.
This incident highlights that organizations should secure backup data just like live data. It also emphasizes the importance of encrypting backup files and regularly reviewing security protocols, including those of third-party contractors.
NVIDIA Releases Security Updates for BlueField, DOCA, Mellanox, ConnectX and NVOS



