Sunday , October 25 2026
Rat

BANKING, MALWARE, FINANCIAL SERVICES, RAT, JS
JSOUTPROX ATTACK FINANCIAL INSTITUTIONS IN APAC

A new version of JSOutProx has been detected by Resecurity. This version is targeting financial services and organizations in the APAC and MENA regions. JSOutProx is a sophisticated attack framework that uses both JavaScript and .NET to carry out its attacks.

The malware allows for the loading of various plugins that carry out additional malicious activities once executed. This malware was first identified in 2019 and was linked to SOLAR SPIDER’s phishing campaigns, distributing the JSOutProx RAT to financial institutions in Africa, the Middle East, South Asia, and Southeast Asia.

Daily Cyber security update for 24. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

NSA, CISA, and NIST have released security guidelines to find, control, and stop AI agents that go beyond their allowed...
Read More
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines
            Source: Resecurity

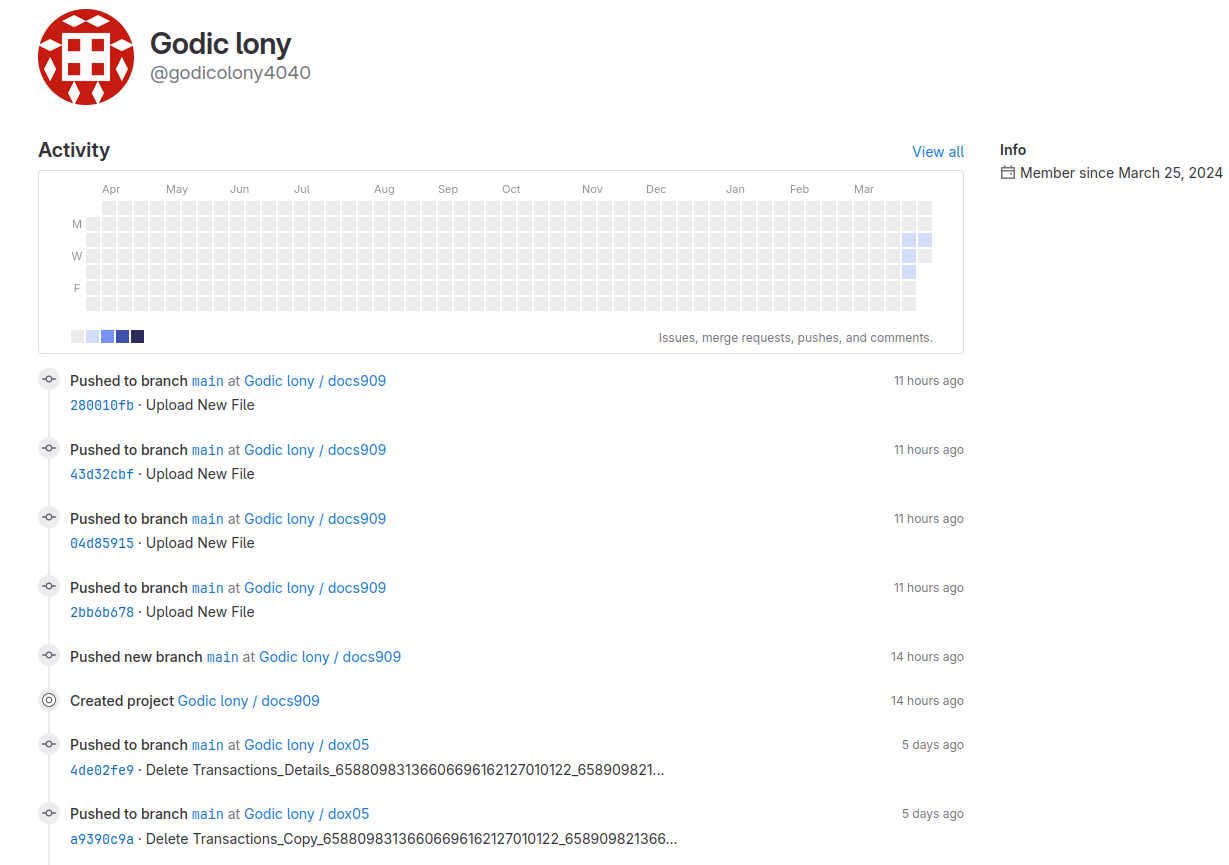
On February 8, 2024, a system integration company based in Saudi Arabia reported an incident where customers of a major bank in the region were targeted. Resecurity helped victims by obtaining the malicious code and recovering the payload. On April 2, 2024, there was another attack, where banking customers were tricked with fake notifications and malicious code.

The new version of JSOutProx, along with the use of platforms like GitHub and GitLab, shows that malicious actors are working hard and smart. JSOutProx has been a threat for five years and continues to evolve, especially for financial institutions’ customers. This year, the threat has expanded to the MENA region, increasing their cybercriminal activity. Resecurity is committed to tracking JSOutProx and protecting financial institutions and their customers worldwide from these harmful activities. To read out the full report click here.


Check Also

Qwen

Claude, DeepSeek, and Qwen AI agents combinedly used to hit gov.t across Asia

Chinese-speaking hackers have added Claude, Qwen, and DeepSeek to their hacking system to automate cyberattacks …