Saturday , November 14 2026
Ducktail malware family

Kaspersky reveals report
Indian marketers targeted by Delphi-powered malware linked with Vietnam

Vietnamese hackers behind the Ducktail stealer malware recently carried out a new campaign from March to early October 2023. They specifically targeted marketing professionals in India in order to take over Facebook business accounts.

“An important feature that sets it apart is that, unlike previous campaigns, which relied on .NET applications, this one used Delphi as the programming language,” Kaspersky said in a report published last week.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

Ducktail, Duckport, and NodeStealer are cybercrime groups in Vietnam. They use sponsored ads on Facebook to spread malicious ads and deploy malware. This malware steals login cookies and allows them to control victims’ accounts.

These attacks mainly target users who have access to a Facebook Business account. The attackers gain unauthorized access and use it to place advertisements for their own financial benefit, spreading the infections even more.

ALSO READ:

Juniper Patches Over 30 Vulnerabilities in Junos OS

A Russian cybersecurity company has documented a campaign where individuals seeking a career change are sent archive files. These files contain a harmful executable file disguised with a PDF icon. The intention is to deceive the targets into opening the binary file.

Doing so results in the malicious file saving a PowerShell script named param.ps1 and a decoy PDF document locally to the “C:\Users\Public” folder in Windows.

“The script uses the default PDF viewer on the device to open the decoy, pauses for five minutes, and then terminates the Chrome browser process,” Kaspersky said.

The parent executable also downloads and launches a rogue library named libEGL.dll, which scans the “C:\ProgramData\Microsoft\Windows\Start Menu\Programs” and “C:\ProgramData\Microsoft\Internet Explorer\Quick Launch\User Pinned\TaskBar\” folders for any shortcut (i.e., LNK file) to a Chromium-based web browser.
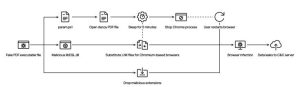
        Malicious file usage flowchart (Securelist)

To proceed, you need to modify the browser’s LNK shortcut file. Add the “–load-extension” command line switch to launch a deceptive extension that pretends to be the real Google Docs Offline add-on in order to remain undetected.

The extension is designed to send information about open tabs to a server controlled by an actor in Vietnam. It is used to hijack Facebook business accounts.

Source: Securelist by Kaspersky

Check Also

Anthropic

Anthropic’s Claude Code Source Code Reportedly Leaked

Anthropic’s special Claude Code CLI tool had its complete TypeScript source code inadvertently exposed due …