 InfoSecBulletin Cybersecurity for mankind
A critical permission misconfiguration in the IBM QRadar Security Information and Event Management (SIEM) platform could allow local privileged users to manipulate configuration files without authorization.
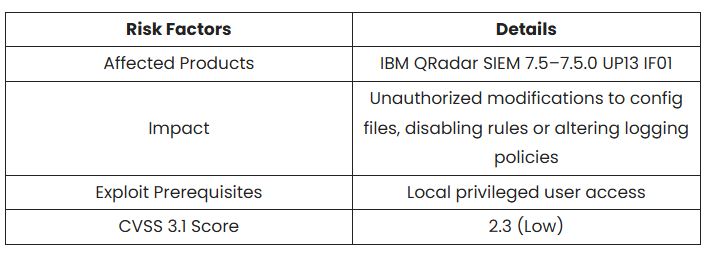
The flaw, identified as CVE-2025-0164, results from incorrect permission assignments and has a CVSS 3.1 score of 2.3 AV:L/AC:L/PR:H/UI:N/S:U/C:L/I:N/A:N).
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Incorrect Permission Assignment Flaw:
The vulnerability exists due to incorrect permission settings for crucial resources (CWE-732), which does not apply proper access controls on configuration files in QRadar SIEM versions 7.5 to 7.5.0 UP13 IF01.
A local user with high-level privileges can misuse poor file system permissions to change important settings, alter logging policies, or turn off detection rules.
Unauthorized changes may continue until manually fixed, complicating incident response and hiding malicious activities in logs, which could permit further undetected actions.
Mitigations:
IBM has released QRadar 7.5.0 UP13 IF02 to fix CVE-2025-0164, ensuring file and directory permissions only allow write access for the QRadar service account.
Administrators should apply the interim fix immediately on affected systems by downloading the update from IBM Fix Central.



