 InfoSecBulletin Cybersecurity for mankind
Scammers called a victim using Google’s official support number and sent an email from an official subdomain. It’s unclear how they managed to use Google’s services. Software engineer Zach Latta, founder of Hack Club, reported a unique attack on GitHub.
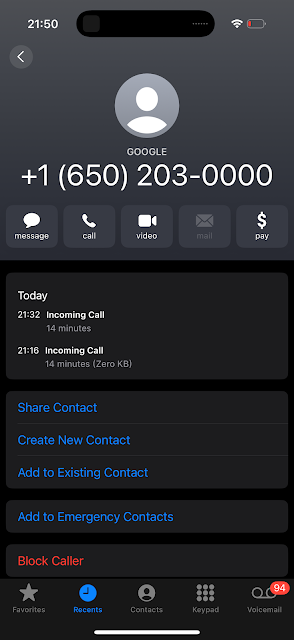
Chloe called Latta from 650-203-0000, identified as “Google.” According to Google’s support page, this number is used by Google Assistant for automated calls like booking appointments or checking restaurant wait times.
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

“She sounded like a real engineer, the connection was super clear, and she had an American accent,” the developer said.
Scammers pretending to be Google Workspace support warned Latta that they had blocked her account after unauthorized access from Frankfurt.
Latta suspected a scam and requested email confirmation.
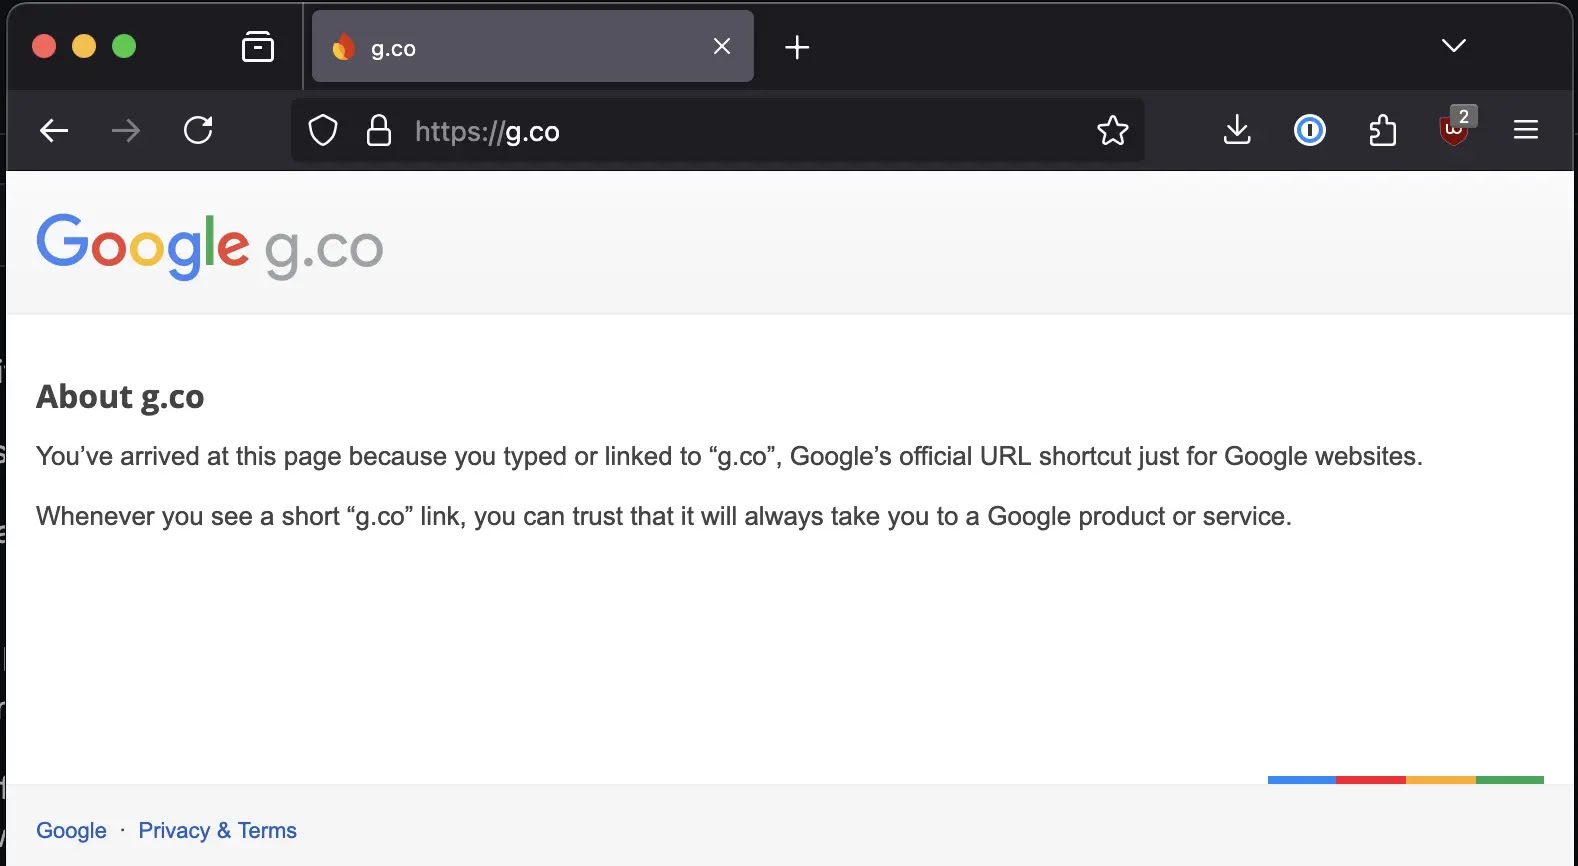
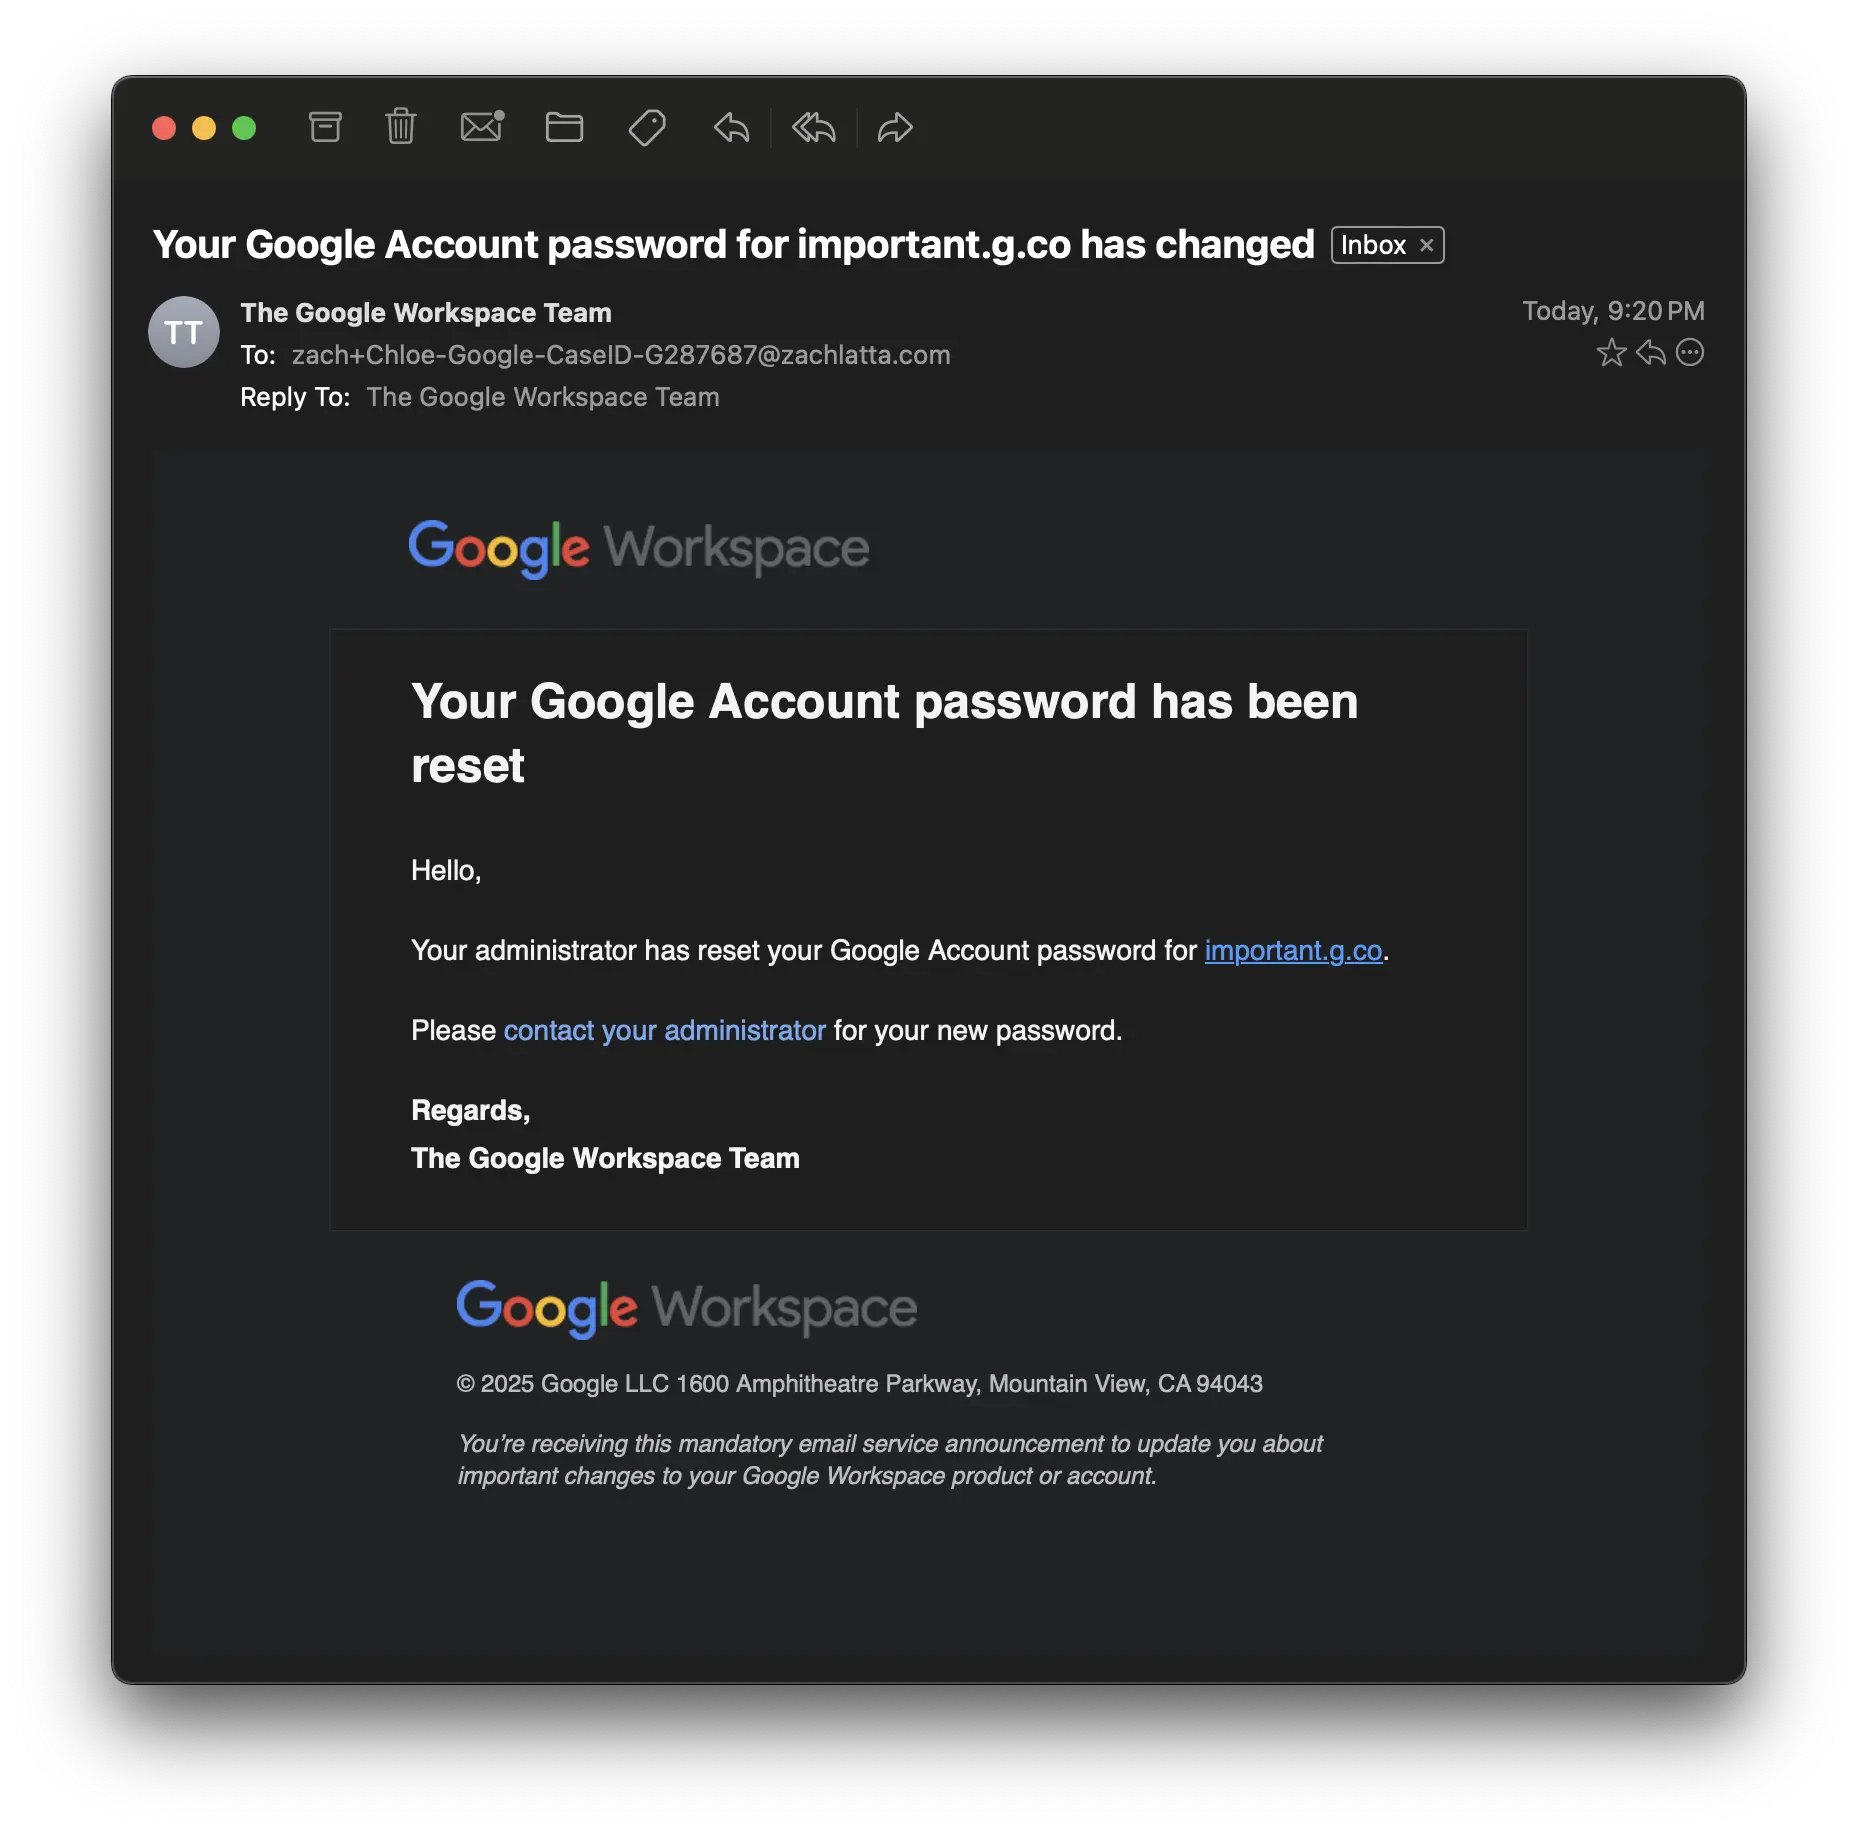
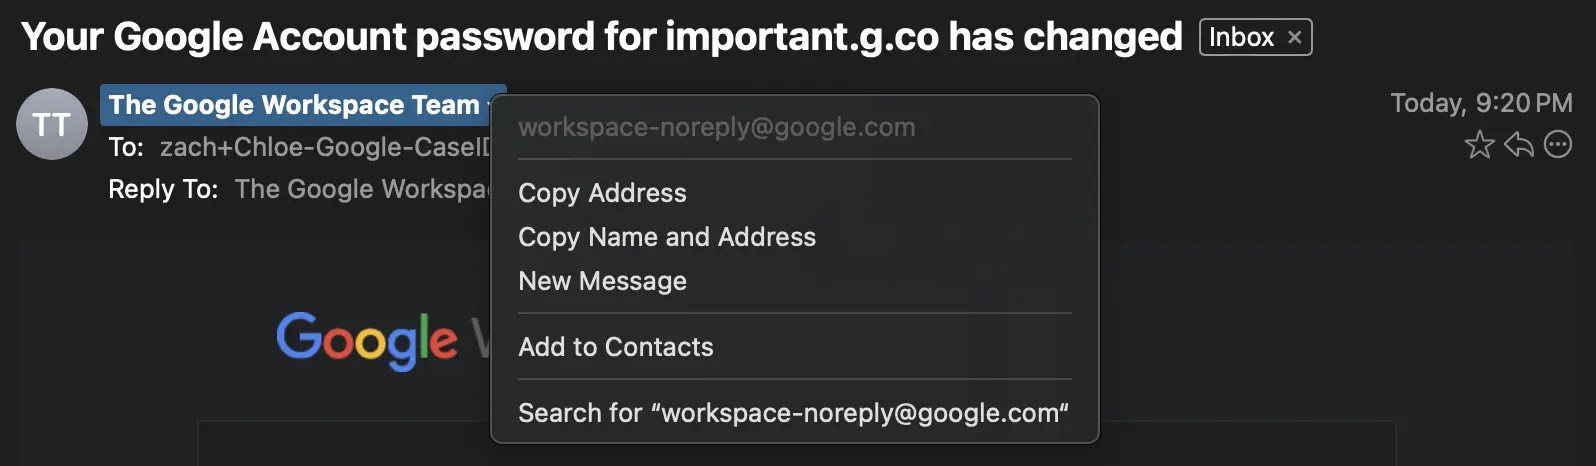
Hackers surprisingly agreed and sent an email from a legitimate Google subdomain, g.co. The email looked authentic, with no signs of spoofing, and it successfully passed DKIM, SPF, and DMARC authentication checks. Latta shared the evidence in a post.
According to Google, g.co is an official URL shortcut that is “just for Google websites.”
“You can trust that it will always take you to a Google product or service,” the landing page for the domain reads.
Scammers suggested that the account may have been hacked via a Chrome extension and used fake LinkedIn accounts to falsely claim they worked at Google.
“Chloe” tried to trick the developer into taping one of the three numbers that popped up on his phone to “reset the account.” In reality, this action would have given scammers access to the account if performed.
The software engineer recorded the conversation when he suspected it was a phishing attempt.
“The thing that’s crazy is that if I followed the two ‘best practices’ of verifying the phone number + getting them to send an email to you from a legit domain, I would have been compromised,” Latta warns.
Google has not yet publicly addressed this specific issue.
Users should be careful with suspicious calls or emails and report any suspicious activity to Google’s security team.
Source: Cybernews, GitHub



