InfoSecBulletin Cybersecurity for mankind
The Dutch military security service MIVD recently revealed that a cyber espionage campaign, which was initially mentioned in February, managed to gain access to around 20,000 Fortigate-secured systems between 2022 and 2023. It is now believed that this campaign “appears to be much more extensive than previously known”.
The Nationaal Cyber Security Centre stated on Monday that the hack was larger than initially believed. The MIVD suspects that the Chinese still have access to certain systems.
Daily Cyber security update for 14.11. 2026

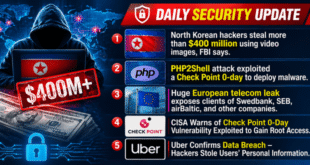
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The MIVD said the Chinese espionage campaign targeted “dozens of western governments, international organizations and a large number of defense ministry firms”.
National Cyber Security Centre (NCSC) said that the state-sponsored hackers behind the spying operation were exploiting a vulnerability in FortiGate devices for “at least two months before Fortinet announced the vulnerability.”
The vulnerability, tracked as CVE-2022- 42475 was exploited during this “so-called ‘zero day’ period” to infect 14,000 devices, according to the alert, with targets including “dozens of (Western) governments, international organizations and a large number of companies within the defense industry.”
Since February, the Dutch military intelligence service has discovered that the Chinese threat group obtained access to at least 20,000 FortiGate systems worldwide in 2022 and 2023 over a span of a few months, at least two months before Fortinet disclosed the CVE-2022-42475 vulnerability.
Dutch new reported, China has denied any involvement in the February report, saying the country “always firmly opposes and cracks down on cyber attacks in all forms in accordance with the law.”
“We will not allow any country or individual using Chinese infrastructure to engage in such illegal activities,” the February statement said.
Source: Source: dutchnews, therecord, bleepingcomputer, ncsc
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)