
Thursday , October 22 2026

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum.

The threat actor claims “We have breached Rajasthan Police, and its data is now available for purchase,” Scarlettgroup said on the forum. The hackers claim that they have access to around 70,000 identity records, and 59,460 mobile numbers. The group says it also obtained details about FIRs, eKYCs, and witness statements.

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

NSA, CISA, and NIST have released security guidelines to find, control, and stop AI agents that go beyond their allowed...
Read More
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Anthropic says a Claude research model showed how the National Security Agency made seeds for five NIST elliptic curves in...
Read More
Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

The Indian Computer Emergency Response Team (CERT-In), which is the government's cybersecurity arm, has issued a "critical" rated advisory after...
Read More
Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

MITRE released ATT&CK v20 adding nine Enterprise techniques that explain how attackers might target AI systems, steal app-specific passwords to...
Read More
MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Cybersecurity researchers at Palo Alto Networks’ Unit 42 have uncovered a sophisticated cyberattack targeting Fortinet network management infrastructure, involving the...
Read More
Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

According to the claimed exposure:

• 5,926 mailboxes containing 8.63 million emails
• 22,686 attachments (6.63 GB)
• 783,495 unique email addresses
• 70,301 identity records
• 59,460 mobile numbers
• 69 verified credentials
• 21 VPN logins and 64 VPN certificates
• 1,065 senior officer mailboxes

The posted sample data reportedly include government communications, financial records, KYC documents and internal access information. If true, it could expose as much as 70,000 identity records, 59,000 mobile numbers, millions of emails, and more.
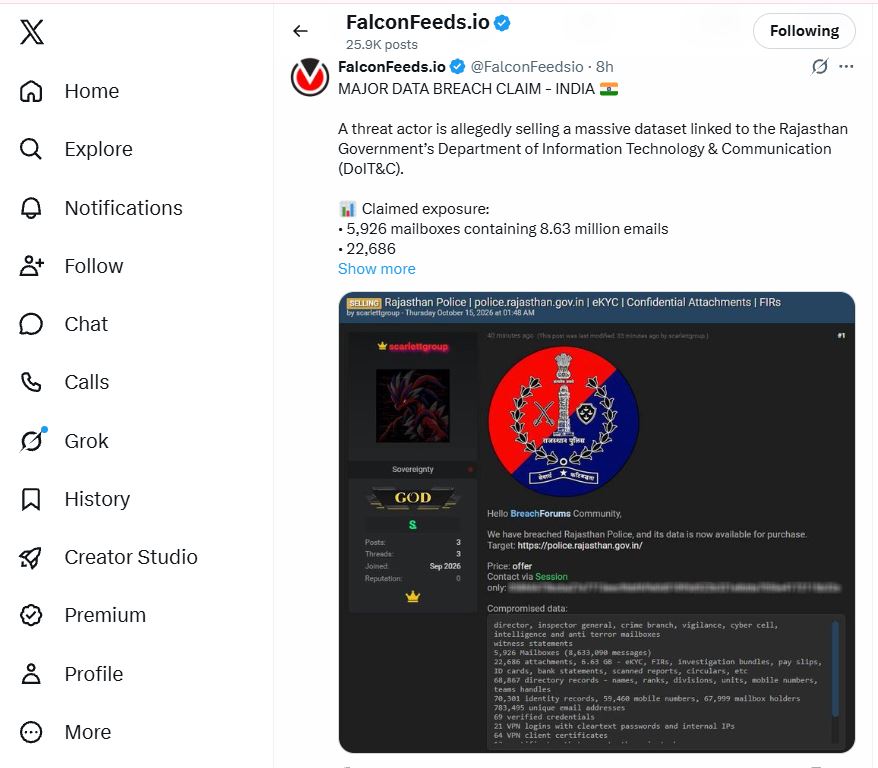
                                                                                       Source: FalconFeeds.io x post

On X, cybersecurity account FalconFeeds.io first reported the breach. As per the post, a hacker group called “Scarlettgroup” is behind the incident. Scarlettgroup has shared details about the incident on BreachForums, a dark web forum.

Indiatoday reported “Scarlettgroup attached redacted images of sample documents from the data set. They say that unredacted versions of them would be provided upon purchase. Though no price was given for the sale. The group claims that they will be selling the data to multiple buyers”.

At the time of publishing, no official statement was found on these claims publicly, and infosecbulleltin could not independently verify and confirm the authenticity of the breach.

However, the authenticity, attribution, and full extent of the claimed breach remain unverified. We cannot claim whether this data is genuine or if it came directly from the Rajasthan Police website.


(Media Disclaimer: This report has been prepared based on information gathered through internal and external research, including publicly available sources. The information is provided for general informational and reference purposes only and should not be construed as independently verified fact unless expressly stated. Readers are encouraged to verify the information through reliable sources before relying on it or taking any action based on its contents. InfosecBulletin shall not be held liable, to the extent permitted by applicable law, for any errors, omissions, inaccuracies, or losses, damages, or consequences arising from the use of, or reliance on, the information presented in this report.)

Check Also

200,000

Major Danish university breached, 200,000 users at risk

Hackers got into the identity and access management system at the Technical University of Denmark …

