 InfoSecBulletin Cybersecurity for mankind
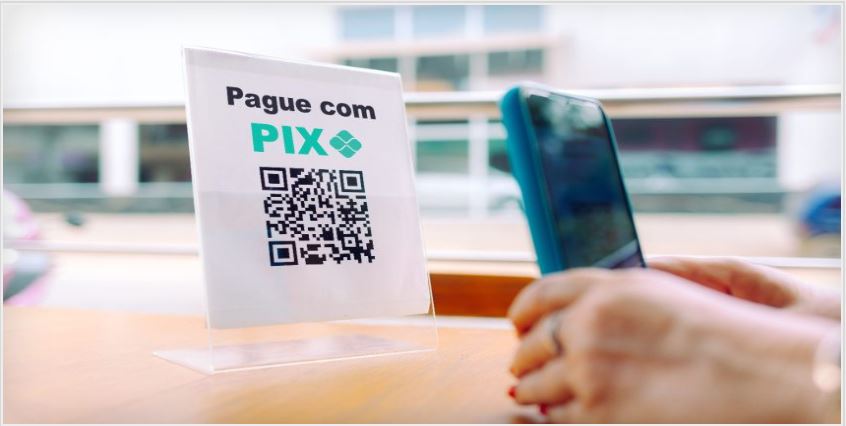
Attackers attempted to steal $130 million from Brazil’s real-time payment system on Friday by wielding valid credentials for an IT service provider. Unauthorized funds were transferred through a breach of the IT system of Sinqia, a Brazilian subsidiary of Evertec. Some of the funds have been recovered. Sinqia, based in Sao Paulo, serves 24 banks using the Brazilian Central Bank’s real-time payment platform, Pix.
Preliminary results from an ongoing digital forensic investigation into the attack “indicate that the unauthorized transactions were introduced into Sinqia’s Pix environment by exploiting legitimate Sinqia IT vendors’ credentials,” Evertec disclosed to investors.
Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Evertec, a leading financial technology and transaction processing provider in Latin America and the Caribbean, based in San Juan, Puerto Rico, acquired Sinqia in November 2023.
Sinqia said that it “halted transaction processing in its Pix environment and began working with outside cybersecurity forensics experts” after detecting hacking activity.
The Central Bank of Brazil introduced Pix in 2020, enabling mobile fund transfers. With 169 million registered users, it processed $6.4 billion in transactions in July. A recent Google survey shows that 94% of Brazilian adults use it, making it the most common payment method for two-thirds of the population of 211 million, slightly surpassing debit cards and cash.
The Brazilian Central Bank quickly disconnected the company’s IT platform from Pix to stop unauthorized transfers and freeze some stolen funds, totaling $64 million so far. They aim to recover more money, while law enforcement investigates the attack.
Sinqia reported that among the two dozen Brazilian financial firms using its platform for Pix, attackers managed to steal funds through “business-to-business financial transactions” from two companies. Local media named the victims as HSBC, which lost $70 million, and fintech Artta, which lost $7 million.
Sinqia’s connection to Pix remains offline, pending a full review by the central bank. The company said that it believes the incident solely affected its systems that connect to the Pix environment and said it’s seen no signs of further compromise, or exposure of personal data.
An HSBC spokeswoman told Information Security Media Group that it “identified financial transactions via Pix in an account with one of the bank’s providers” and that “no customer accounts or funds were impacted by the transaction, as they occurred exclusively within the provider’s system.” The bank said Sinqia took steps to block the rogue transactions in its own environment.*
Fintech Artta said in a statement it’s liaising with Sinqia and the BCB, and hopes to resume service as quickly as possible.
Evertec warned investors that “the financial and reputational impact of the incident, including any impact on the company’s internal controls, are not yet known and could be material,” and also that it has yet to determine “the scope of any liability associated with this matter, the applicability of any insurance coverage or what claims” that it may have against any culpable vendors or suppliers.
HexStrike AI Connects ChatGPT, Claude, Copilot with 150+ Security Tools



