 InfoSecBulletin Cybersecurity for mankind
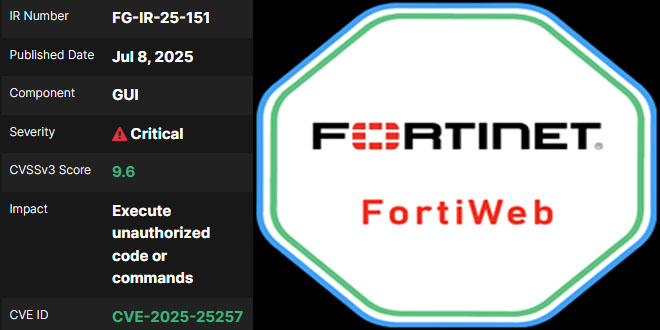
Fortinet has issued a critical patch for a critical vulnerability in its FortiWeb product, a web application firewall commonly used in enterprises. Identified as CVE-2025-25257, this high-severity issue is an unauthenticated SQL injection flaw that lets remote attackers run unauthorized SQL commands through specially crafted HTTP or HTTPS requests.
“An improper neutralization of special elements used in an SQL command (‘SQL Injection’) vulnerability [CWE-89] in FortiWeb may allow an unauthenticated attacker to execute unauthorized SQL code or commands via crafted HTTP or HTTPs requests,” Fortinet stated in its advisory.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The issue, with a CVSS score of 9.6, is critical as it doesn’t require authentication to exploit, making it an attractive target for attackers.

If not fixed, the vulnerability allows attackers to access sensitive data, change database content, or compromise backend systems.
For organizations that can’t upgrade right away, Fortinet suggests disabling the HTTP/HTTPS administrative interface as a temporary workaround:
“Disable HTTP/HTTPS administrative interface,” the advisory recommends, as this interface is the primary attack vector.
However, disabling the GUI interface may limit manageability and is not considered a permanent solution. Organizations are strongly urged to apply the vendor-supplied patches.
Fortinet is pleased to thank Kentaro Kawane from GMO Cybersecurity by Ierae for reporting this vulnerability under responsible disclosure.



