InfoSecBulletin Cybersecurity for mankind
Cybersecurity researcher Jeremiah Fowler found a non-password-protected database with 780,000 records from FleetPanda, a tech provider for dispatch management. The database included invoices, driver applications, and images of licenses and background checks containing personal identifiable information (PII).
A non-password-protected database held 780,191 documents, totaling 193 GB. The exposed files included .PDFs, .jpgs, and other image formats, detailing fuel and petroleum shipments to various companies and industries. These documents, dating from 2019 to August 2024, included invoices, delivery tickets, and records related to drivers, licenses, vehicles, and workers. Invoices provided billing and delivery details, such as addresses, order numbers, and tracking data.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

The database had sensitive information, including high-resolution images of driver’s licenses and employment applications with Social Security numbers and personal information. Exposed business records and personal data pose serious security and privacy risks. I noticed documents showing deliveries to various states, including California, Oregon, Texas, and Colorado.
Fowler said, a deeper examination revealed that the documents and the database name were linked to FleetPanda, a California-based software and technology firm specializing in services and support for the petroleum and fuel sector.
After discover, Fowler report it to FleetPanda, but he did’t get any response. However, It’s not clear how long the documents were accessible or if anyone else accessed the database. An internal forensic audit would be needed to discover any unauthorized access or unusual activity.
According to FleetPanda’s LinkedIn page, FleetPanda modernizes outdated manual and spreadsheet methods with an easy dispatch tool. It efficiently manages all order types, provides a live dashboard for tracking, includes an Uber-like driver app, automates pricing and contracts, and integrates seamlessly with your existing tech, consolidating all key business data into one digital platform.
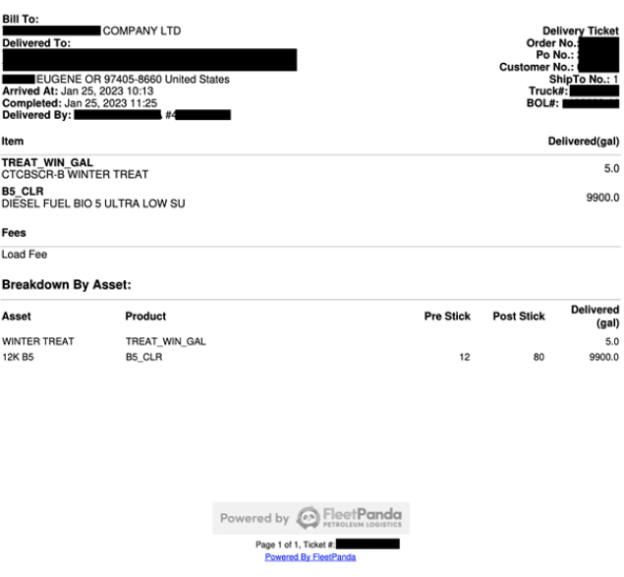
This screenshot is an invoice for a delivery of 9,900 gallons of diesel fuel, valued at around $41,000 based on the average retail price of $4.21 per gallon in 2023. Industries with significant financial transactions are likely high-value targets for criminals.
The DarkSide hacker group’s attack exposed weaknesses in critical infrastructure, leading to a greater emphasis on cybersecurity. In response, the U.S. government prioritized the protection of energy infrastructure. In January 2024, the Department of Energy announced a $70 million investment to develop technologies aimed at securing energy delivery against cyber and physical threats.
According to a report published in Security Magazine, From 2021 to 2022, cyberattacks on energy companies in the U.S. and Canada increased by about 71%. The U.S. energy infrastructure, which includes electricity, oil, and natural gas, is at risk due to its interconnected systems and outdated components. While I am not suggesting that FleetPanda’s customers are currently at risk, the industry shows a high potential for cyber threats based on past incidents.
The exposure of thousands of internal documents poses a risk of invoice fraud, where criminals deceive organizations into paying fake invoices by pretending to be legitimate vendors. They often use real invoices from data breaches as templates for their scams. According to a 2022 FBI IC3 report, victims of invoice fraud lose an average of over $120,000 per incident, with about 68% of companies affected annually across all industries. This is just a risk scenario for businesses to consider; it does not imply that FleetPanda’s customers are at risk.
Exposed personal information poses significant risks to individuals and their organizations. The database included images of driver’s licenses, driving records, hazardous materials certifications, background checks, and employment applications containing personal information and Social Security numbers. This data could be misused for identity theft, financial fraud, or social engineering. In critical infrastructure sectors, criminals could impersonate employees to gather information, gain unauthorized access, or conduct sabotage.
Jeremiah Fowler advises organizations to keep important employee data separate from regular business documents like invoices. Individuals concerned about their personal information should consider annual credit checks and monitor for any suspicious activity involving their name, credit profile, or SSN. Both organizations and individuals must quickly identify any potential misuse of data. This is not to suggest an immediate threat of identity theft, but to raise awareness of potential risks.