InfoSecBulletin Cybersecurity for mankind
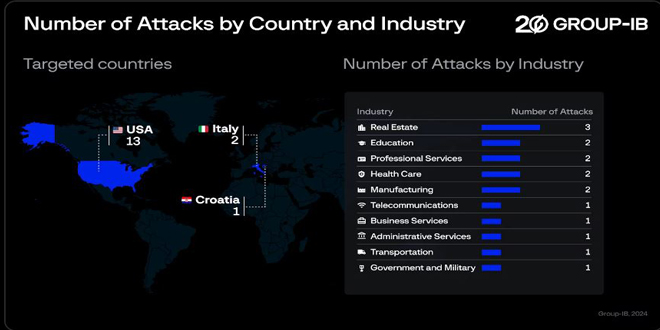
A new ransomware named Eldorado appeared in March and has locker versions for VMware ESXi and Windows. The gang has claimed 16 victims, mostly in the U.S., in various sectors including real estate, education, healthcare, and manufacturing.
Researchers from Group-IB observed the activity of Eldorado. They found that the operators of Eldorado were advertising their harmful service on RAMP forums and looking for experienced affiliates to join their program.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

Encrypting Windows and Linux:
Eldorado is a ransomware that can encrypt both Windows and Linux platforms. The researchers got an encryptor from the developer. The user manual says that there are 32/64-bit versions for VMware ESXi hypervisors and Windows.
Group-IB says that Eldorado is a unique development “and does not rely on previously published builder sources.”
The malware uses the ChaCha20 algorithm to encrypt files, with a unique 32-byte key and 12-byte nonce for each file. These keys and nonces are then encrypted using RSA with the Optimal Asymmetric Encryption Padding (OAEP) scheme.
Files are given a new extension “.00000001” after being encrypted. Ransom notes named “HOW_RETURN_YOUR_DATA.TXT” are placed in the Documents and Desktop folders.
Eldorado encrypts network shares using the SMB protocol to maximize its impact and deletes shadow volume copies on compromised Windows machines to prevent recovery.
The ransomware skips DLLs, LNK, SYS, and EXE files, as well as files and directories related to system boot and basic functionality to prevent rendering the system unbootable/unusable.
Finally, it’s set by default to self-delete to evade detection and analysis by response teams.
The researchers from Group-IB discovered that affiliates can personalize their attacks. They can choose specific directories to encrypt and avoid encrypting local files. Moreover, they can target network shares on certain subnets and make sure the malware cannot delete itself. Linux only allows customization up to setting encryption directories.