Saturday , October 24 2026
ICICI Bank

India’s ICICI Bank exposed thousands of credit cards to ‘wrong’ users

“Our customers are our utmost priority and we are wholeheartedly dedicated to safe guarding their interests. It has come to our notice that about 17,000 new credit cards which were issued in the past few days were erroneously mapped in our digital channels to wrong users. They constitute about 0.1% of the Bank’s credit card portfolio. As an immediate measure, we have blocked these cards and are issuing new ones to the customers. We regret the inconvenience caused. No instance of misuse of a card from this set has been reported to us. However, we assure that the Bank will appropriately compensate a customer in case of any financial loss,” said a statement from an ICICI Bank spokesperson.

Hindustantimes wrote, One Reddit user flagged a situation where another user’s Amazon Pay credit card details were mistakenly displayed. Additionally, users reported successful ICICI card transactions despite entering incorrect three-digit CVVs.

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

NSA, CISA, and NIST have released security guidelines to find, control, and stop AI agents that go beyond their allowed...
Read More
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Anthropic says a Claude research model showed how the National Security Agency made seeds for five NIST elliptic curves in...
Read More
Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

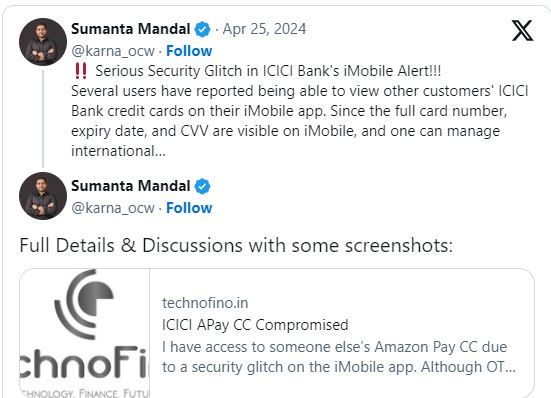
Sumantha Mandal, Founder of TechnoFino and CreditPedia, reiterated concerns about the security breach on platform X.

Source: Hindustantimes

He stated that this error allowed users to access other customers’ credit card details, including sensitive information such as full card numbers, expiry dates, and CVVs. Mandal also shared screenshots from concerned users.
Source: Hindustantimes

In one of the shared screenshots, a user highlighted that despite OTP restrictions for domestic transactions, he was able to perform international transactions using the details obtained from the iMobile app.

ICICI Bank, which has more than 6,000 branches in India, is in 17 countries worldwide. The iMobile Pay app, launched in 2008, has over 28 million users.


Check Also

email addresses

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Nearly 100,000 Bee Cheng Hiang customers had their email addresses leaked when an employee used …