InfoSecBulletin Cybersecurity for mankind
Dell is investigating claims of a data breach after a threat actor leaked information on over 10,000 employees. “We are aware of the claims and our security team is currently investigating,” Dell told BleepingComputer.
A hacker called “grep” claims that Dell suffered a “minor” data breach, stealing over 10,000 employee records. The hacker disclosed information on Breach Forums, a well-known cybercrime site, where they leaked stolen data today, September 19, 2024. The hacker also claims the breach happened earlier this month.
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

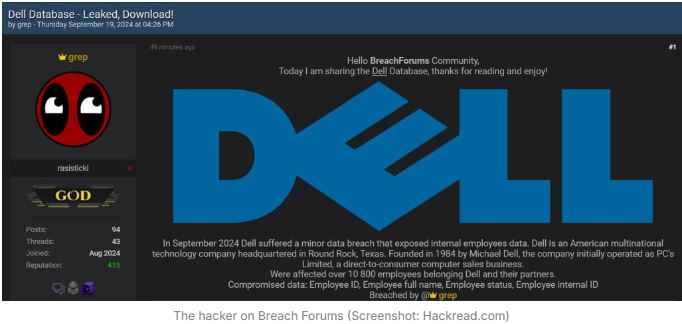
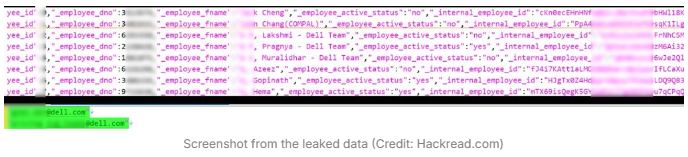
The leaked data revealed the following information:
Full names
Employee ID: A unique identifier for the employee.
Employee Active Status: Indicates whether the employee is currently active
Employee DNO: This may represent a department number or another internal identifier.
Internal Employee ID: A unique internal identifier that seems to be a hashed or encoded value.
Hackread.com reported, ” This is not the first time Dell has made headlines for cybersecurity-related issues. In May 2024, the Round Rock, Texas-based company disclosed a data breach after another hacker on a breach forum attempted to sell 49 million alleged customer records.”
Stephen Kowski, Field CTO at Pleasanton, Calif.-based SlashNext Email Security+ weighed in stating “The alleged Dell data breach serves as a stark reminder of the ongoing cybersecurity challenges faced by large corporations. With over 10,000 employee records reportedly exposed, including names, employee IDs, and internal identifiers, this incident highlights the potential vulnerabilities in even well-established tech companies.”
“While Dell has not yet confirmed the breach, the leaked information could be leveraged by threat actors for targeted phishing attempts or social engineering attacks, particularly given recent trends in cybercriminal tactics,” Stephen warned.
“Organizations must implement robust security measures, including advanced threat detection systems and regular security audits, to protect sensitive employee data and maintain trust. Timely incident response and transparent communication with affected individuals are also essential in mitigating the potential fallout from such breaches,” he advised.