Thursday , October 1 2026

DDoS Attacks at 633.7 Gbps Combining ACK, PUSH, RESET, and SYN Packets

The DDoS attack is constantly evolving due to advancements in technology and the changing motivations of attackers. Recent cases have shown that these attacks can cause significant damage and have severe legal consequences.

ALSO READ:

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Hackers to exploit a flaw in Zimbra mail servers that are connected to the Internet. They send special emails that...
Read More
Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

Google has said that hackers are using two serious Citrix NetScaler security holes to get root access, set up hidden...
Read More
Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is alerting people about a major flaw in MikroTik RouterOS. This could...
Read More
CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

Apple has launched iOS 26.7.1 and iPadOS 26.7.1 to fix a serious zero-day flaw that it believes might have been...
Read More
Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

The JadePuffer ransomware group is attacking Azure users with agent-based attacks that gather information, steal passwords, and damage key components. The...
Read More
JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

The 5th Edition of InfoSecCon-2026, a premier cybersecurity-focused event, has been successfully completed with the participation of cybersecurity professionals, technology...
Read More
“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

Microsoft has fixed a serious security flaw in Azure AI Foundry that could let bad actors gain privilege escalation. The...
Read More
Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Amazon Web Services cannot restore access to its cloud-computing facility in Bahrain and ‌one of three data-hosting zones in the...
Read More
AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

A threat actor is allegedly offering a private remote code execution exploit for Fortinet FortiGate SSL VPN appliances, claiming that...
Read More
Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

Anthropic is making a new Claude feature called “Money.” It's a separate tab in the mobile app. The new interface...
Read More
Anthropic prepares “Claude Money” to analyze bank account and financial data

MGM hacker hit at least 100 organizations

Akamai Prolexic’s DDoS defense platfam has successfully thwarted the most colossal DDoS attack ever recorded on a prominent U.S. financial institution’s platform. The attack, which unleashed a formidable torrent of 633.7 Gbps and 55.1 Mpps, was powerfully neutralized.

Akamai security analysts reported a major DDoS attack that lasted less than 2 minutes. During the attack, the threat actors used a combination of flood attack vectors.

ACK
PUSH
RESET
SYN

In Europe and the Asia-Pacific region, Prolexic‘s DDoS protection shield platform successfully thwarted numerous unprecedented attacks. Among them, a staggering 704.8 million packets per second (Mpps) spike in September 2022 and an astounding 900.1 gigabits per second (Gbps) surge in February 2023 were skillfully neutralized.
Malicious Traffic source

Here below, Akamai have mentioned the top malicious traffic sources:-

Bulgaria
Brazil
China
India
United States
Thailand
Russia
Ukraine
Vietnam
Japan
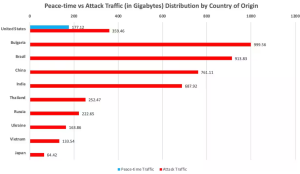
   Distribution of peacetime traffic and attack traffic (Source – Akamai)

Akamai mentioned the following recommendations :-

  • Make sure to adopt CISA recommendations promptly.
  • Check all the key subnets and IPs for effective mitigation controls.
  • Establish continuous DDoS security controls as your initial defense layer.
  • Enhance security with advanced network cloud firewall beyond basic DDoS protection.
  • Form a proactive crisis team and keep incident plans and runbooks up to date.

Check Also

Casbaneiro

Hackers deploy Casbaneiro Trojan that activates on bank websites

Casbaneiro is going after online banking users by sending fake messages that seem like urgent …