 InfoSecBulletin Cybersecurity for mankind
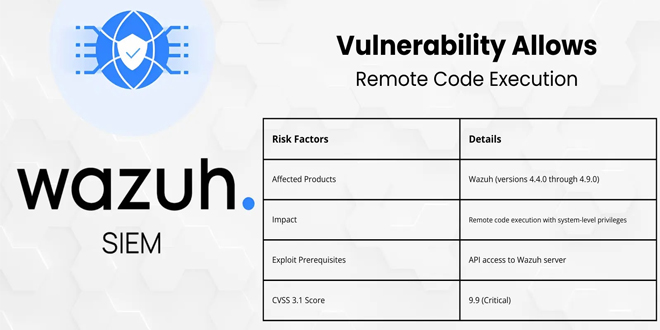
Cybersecurity researchers unveil a critical remote code execution vulnerability (CVE-2025-24016) in Wazuh, a popular open-source SIEM platform.
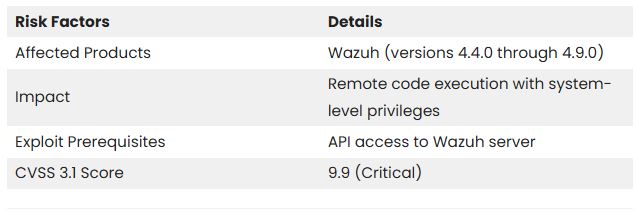
The vulnerability has a CVSS score of 9.9 affects Wazuh versions 4.4.0 to 4.9.0, enabling attackers with API access to run arbitrary Python code on the servers.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

The flaw is due to unsafe deserialization in the DistributedAPI (DAPI) component, where parameters are serialized as JSON and then deserialized using the as_wazuh_object function in framework/wazuh/core/cluster/common.py.
This function has a serious security flaw that allows arbitrary code execution when handling malicious JSON payloads.
Attackers can exploit this vulnerability by using a malicious JSON payload with the unhandled_exc key. This can execute arbitrary system commands.
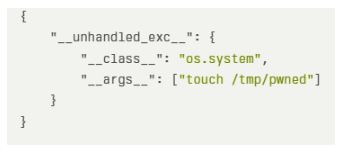
The vulnerable as_wazuh_object function would execute the command “touch /tmp/pwned” on the server when processed by this payload.
The summary of the vulnerability is given below:
Mitigations:
Wazuh fixed this vulnerability in version 4.9.1 by replacing the unsafe eval() function with the safer ast.literal_eval(), which evaluates strings with Python literals without running arbitrary code.
Security experts recommend that organizations with affected Wazuh versions update right away.
“This is a critical vulnerability that should be addressed with the highest priority,” warns the Centre for Cybersecurity Belgium.
Experts suggest organizations that can’t update immediately should use network segmentation, limit API access, monitor API traffic for suspicious activity, and employ Web Application Firewalls (WAFs) to block malicious requests.



