 InfoSecBulletin Cybersecurity for mankind
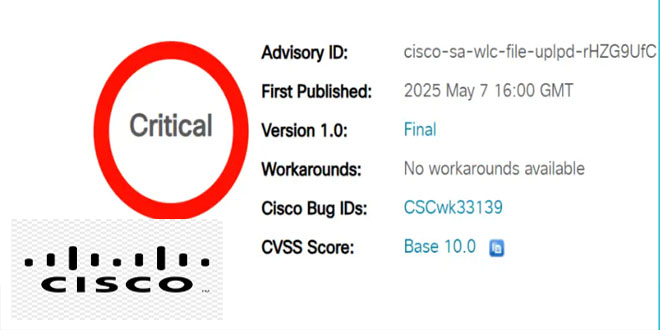
Cisco has issued a security advisory for a critical vulnerability in its IOS XE Software for Wireless LAN Controllers (WLCs). This vulnerability, known as CVE-2025-20188, has a CVSS score of 10, indicating the highest security flaw.
The advisory highlights a vulnerability in the Out-of-Band Access Point (AP) Image Download feature that may enable a remote, unauthenticated attacker to upload arbitrary files to an affected system. The root cause of this vulnerability is “the presence of a hard-coded JSON Web Token (JWT) on an affected system.”
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

An attacker could exploit this vulnerability by sending specially crafted HTTPS requests to the AP image download interface. This could allow them to upload files, perform path traversal, and execute arbitrary commands with root privileges, leading to severe consequences.
The vulnerability impacts certain Cisco products using a vulnerable version of Cisco IOS XE Software for WLCs that have the Out-of-Band AP Image Download feature turned on. Affected products include:
Catalyst 9800-CL Wireless Controllers for Cloud
Catalyst 9800 Embedded Wireless Controller for Catalyst 9300, 9400, and 9500 Series Switches
Catalyst 9800 Series Wireless Controllers
Embedded Wireless Controller on Catalyst APs
Cisco has released free software updates to fix this vulnerability. Customers with service contracts can get these security fixes through their regular update channels.
The Cisco Product Security Incident Response Team (PSIRT) is not aware of any public announcements or malicious use of this vulnerability as of now.



