 InfoSecBulletin Cybersecurity for mankind
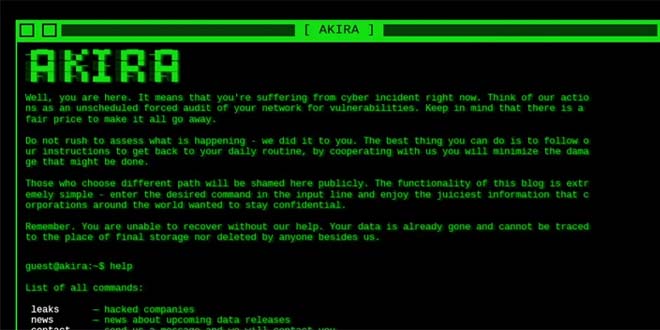
The US cybersecurity agency, CISA, added a security flaw in Cisco’s ASA and FTD software to its list of known exploited vulnerabilities following reports that it’s being likely exploited in Akira ransomware attacks.
The vulnerability is CVE-2020-3259, with a high severity level (CVSS score: 7.5). It allows attackers to access memory on the device. Cisco fixed it in updates from May 2020.
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

Cybersecurity firm Truesec recently discovered evidence that Cisco Anyconnect SSL VPN appliances have been targeted by Akira ransomware actors for over a year.
“There is no publicly available exploit code for […] CVE-2020-3259, meaning that a threat actor, such as Akira, exploiting that vulnerability would need to buy or produce exploit code themselves, which requires deep insights into the vulnerability,” security researcher Heresh Zaremand said.
According to Palo Alto Networks Unit 42, Akira is one of the 25 groups that have created new data leak sites in 2023, claiming to have nearly 200 victims. The group was first noticed in March 2023. It is believed to be linked to the Conti syndicate, as the ransom proceeds have been sent to Conti-affiliated wallet addresses.
In only the fourth quarter of 2023, the e-crime group had 49 victims listed on its data leak portal. This puts it behind LockBit (275), Play (110), ALPHV/BlackCat (102), NoEscape (76), 8Base (75), and Black Basta (72).
Federal Civilian Executive Branch (FCEB) agencies must fix any vulnerabilities by March 7, 2024, to protect their networks from potential threats.
CVE-2020-3259 is far from the only flaw to be exploited for delivering ransomware. Earlier this month, Arctic Wolf Labs revealed the abuse of CVE-2023-22527 – a recently uncovered shortcoming in Atlassian Confluence Data Center and Confluence Server – to deploy C3RB3R ransomware, as well as cryptocurrency miners and remote access trojans.
The development comes as the U.S. State Department announced rewards of up to $10 million for information that could lead to the identification or location of BlackCat ransomware gang key members, in addition to offering up to $5 million for information leading to the arrest or conviction of its affiliates.
The ransomware-as-a-service (RaaS) scheme, much like Hive, compromised over 1,000 victims globally, netting at least $300 million in illicit profits since its emergence in late 2021. It was disrupted in December 2023 following an international coordinated operation.
The ransomware landscape has become a lucrative market, attracting the attention of cybercriminals looking for quick financial gain, leading to the rise of new players such as Alpha (not to be confused with ALPHV) and Wing.
There are indications that Alpha could be connected to NetWalker, which shuttered in January 2021 following an international law enforcement operation. The links pertain to overlaps in the source code and the tactics, techniques, and procedures (TTPs) used in attacks.
“Alpha may be an attempt at reviving the old ransomware operation by one or more of the original NetWalker developers,” Broadcom-owned Symantec said. “Alternatively, the attackers behind Alpha may have acquired and modified the original NetWalker payload in order to launch their own ransomware operation.”
The U.S. Government Accountability Office (GAO), in a report published towards the end of January 2024, called for enhanced oversight into recommended practices for addressing ransomware, specifically for organizations from critical manufacturing, energy, healthcare and public health, and transportation systems sectors.
Source: CISA, Hackernews



